Insider threats are no longer a rounding error in the security budget. In 2026, the average organization spends $19.5 million a year dealing with insider risk, and 83% of organizations report at least one insider attack. The uncomfortable part: most of it is not sabotage. It is negligence, stolen credentials, and ordinary people making ordinary mistakes.
Key Takeaways
- Insider risk costs $19.5M per organization per year in 2026, up 123% from $8.76M in 2018 (Ponemon/DTEX).
- 83% of organizations had at least one insider attack in the prior year, and 48% say attacks are getting more frequent (Cybersecurity Insiders).
- 53% of insider incidents come from negligence, 27% from malicious insiders, and 20% from credential theft, so most incidents are not deliberate.
- Credential theft is the costliest per incident at $842,462; a full malicious-insider data breach averages $4.92M (Ponemon, IBM).
- Containment averages 67 days, and only 13% of incidents are contained within 30 days (Ponemon).
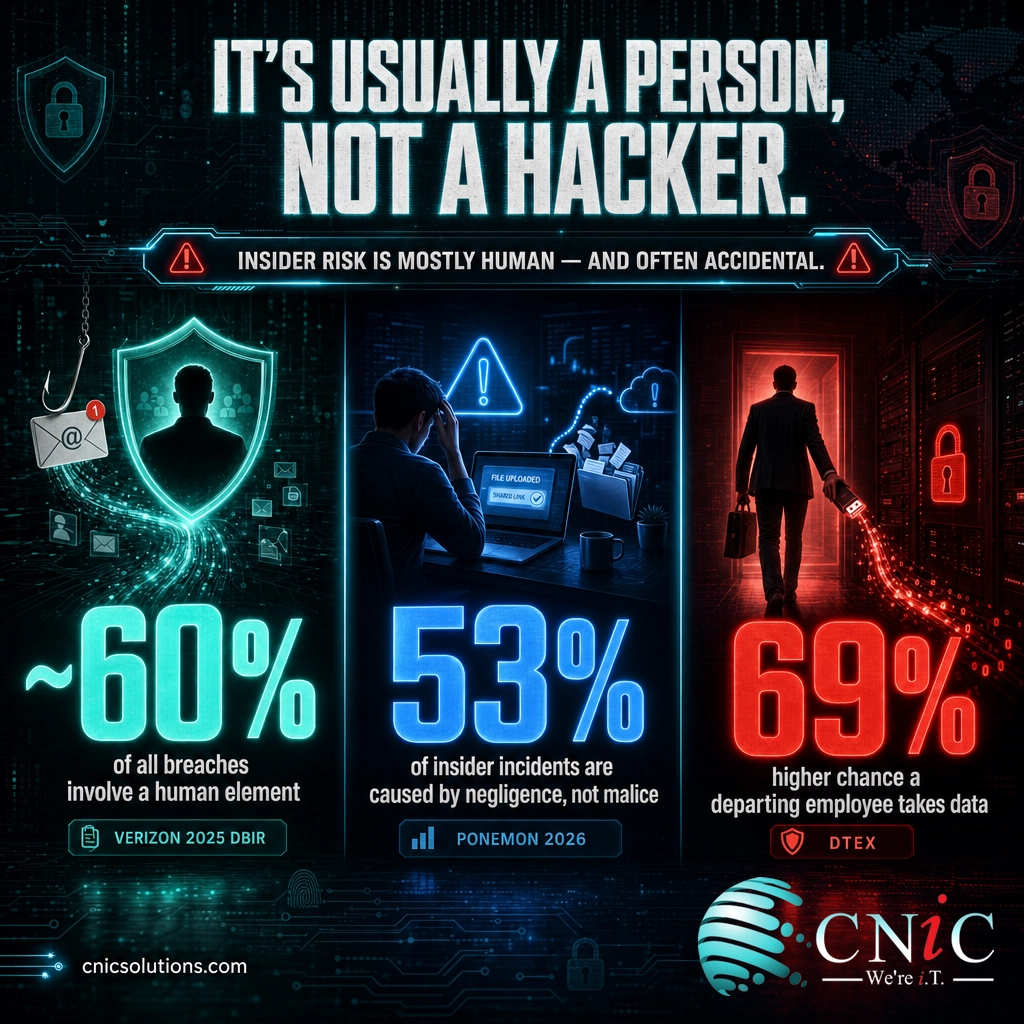
- The human element factors into about 60% of all breaches, and internal actors drive most privilege misuse and error-based breaches (Verizon DBIR).
- Departing employees are roughly 69% more likely to take data, making offboarding a measurable risk window (DTEX).
What’s in This Report
- How Common Insider Threats Are in 2026
- The Cost of Insider Threats
- Negligent, Malicious, and Stolen Credentials
- The Human Element Behind Most Breaches
- Detection and the 67-Day Containment Problem
- Who Gets Hit Hardest, by Industry and Size
- What Actually Reduces Insider Risk
- Summary Table: Every Stat in One Place
- Frequently Asked Questions
How Common Insider Threats Are in 2026
Insider threats have moved from the edge of the risk register to the center of it. In the Cybersecurity Insiders 2024 Insider Threat Report, a survey of more than 400 security practitioners, 83% of organizations reported at least one insider attack in the prior 12 months. Nearly half said the problem is accelerating.
Volume is climbing too. The share of organizations dealing with 11 to 20 insider attacks in a single year grew fivefold compared with 2023. Most respondents point to the same cause: environments got more complex, with remote work, cloud sprawl, contractors, and now AI tools widening the number of people and pathways that touch sensitive data.
It helps to be precise about what an insider is. In these studies an insider is anyone with legitimate, trusted access to systems or data: full-time employees, of course, but also contractors, vendors, temporary staff, and even the automated service accounts that run in the background. That definition is why the numbers are so large. A modern business grants trusted access to far more people and processes than its own headcount, and every one of those grants is a potential insider event if it is misused, mishandled, or hijacked.
| Prevalence Signal | Figure | Source |
|---|---|---|
| Organizations reporting at least one insider attack | 83% | Cybersecurity Insiders 2024 |
| Organizations that lack tools to confidently handle insider threats | 52% | Cybersecurity Insiders 2024 |
| Organizations citing cost or technical hurdles as the main obstacle | 70% | Cybersecurity Insiders 2024 |
| Organizations that say attacks grew more frequent | 48% | Cybersecurity Insiders 2024 |
The takeaway from the prevalence data is not that everyone has a rogue employee. It is that insider risk is now a near-universal operating condition, and roughly half of organizations admit they cannot handle it with the tools they have. That gap between exposure and readiness is where the losses accumulate. For a closer look at the social-engineering side of insider risk, where an outsider tricks a trusted employee into handing over access, see our related breakdown of the latest phishing statistics for 2026.
Source: Cybersecurity Insiders 2024 Insider Threat Report | Gurucul 2024 Insider Threat Report
The Cost of Insider Threats
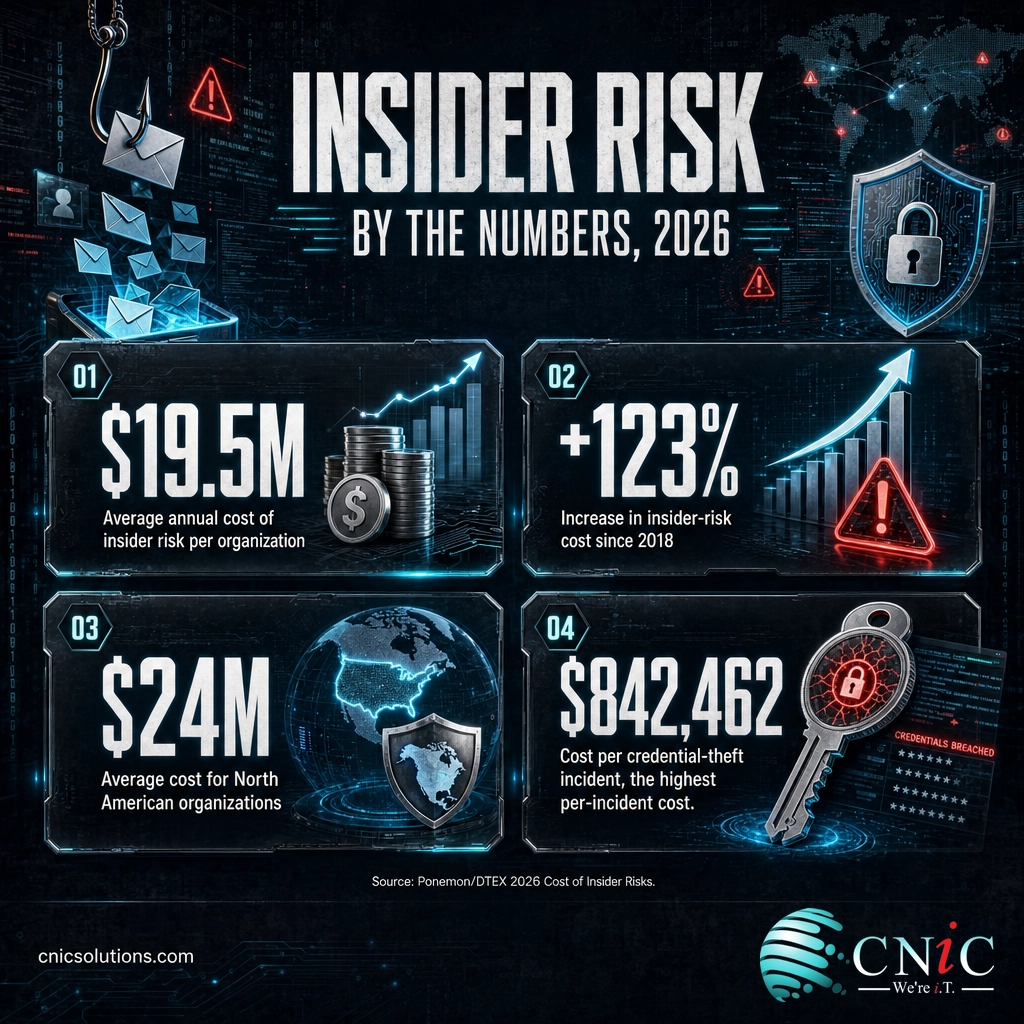
The headline figure comes from the 2026 Ponemon Cost of Insider Risks Global Report, sponsored by DTEX, which is built on interviews with 8,750 IT and security practitioners across 354 organizations worldwide. It puts the average annualized cost of insider risk at $19.5 million per organization. North American organizations carry the heaviest load at about $24 million, with Europe at $18.6 million.
That number is not a spike. It is the top of a steady, decade-long climb. Ponemon has tracked the same benchmark since 2018, when the average sat at $8.76 million. The 123% increase since then reflects both more incidents and higher per-incident costs, as attackers weaponize stolen credentials and employees move data through more channels than ever.
Average Annual Cost of Insider Risk, 2018 to 2026 (Ponemon/DTEX)
CNiC Solutions Analysis: The Gap Between an Incident and a Breach
Two Tier 1 datasets, read together, show why insider events are so financially dangerous once they escalate. Ponemon prices a contained malicious-insider incident at $742,125. IBM prices a full malicious-insider data breach at $4.92 million.
Formula: $4,920,000 (IBM malicious-insider breach) ÷ $742,125 (Ponemon malicious-insider incident) = roughly 6.6×.
A malicious-insider event that crosses the line into a reportable data breach costs about 6.6 times a malicious-insider incident that is caught and contained internally. The lesson is that early detection is not a soft benefit, it is the difference between a six-figure problem and a multimillion-dollar one. Calculation and interpretation original to CNiC Solutions, using figures from Ponemon/DTEX 2026 and IBM 2025.
Money spent on insider risk competes directly with everything else a business wants to fund. Understanding where those dollars go is the first step toward shrinking them, which is exactly what a structured cybersecurity program is designed to do.
See how managed cybersecurity reduces insider risk
Source: Ponemon/DTEX 2026 Cost of Insider Risks Global Report | IBM Cost of a Data Breach 2025
Negligent, Malicious, and Stolen Credentials
The single most useful thing to understand about insider threats is that they are not one thing. Ponemon splits them into three categories, and the split matters because each demands a different response.
Negligent employees are the largest category by far, responsible for 53% of insider incidents. These are the missent emails, the misconfigured cloud buckets, the ignored security policies, and now the sensitive data pasted into unsanctioned AI tools. Malicious insiders who steal, sabotage, or leak on purpose account for 27%. Credential theft, where an external attacker logs in as a legitimate insider, makes up the remaining 20% and costs the most per incident.
Shadow AI has quickly become one of the fastest-growing forms of negligence, and it fits the pattern exactly. An employee pastes a customer list or a block of source code into a public chatbot to get work done faster. There is no malice and often no awareness that a policy was broken, yet sensitive data has now left the organization’s control through a channel that looks entirely ordinary. It is the classic negligent-insider profile updated for 2026, and it is a large part of why the negligence category keeps growing.
The reason credential theft counts as an insider problem, even though the attacker is an outsider, is that the activity is indistinguishable from a real employee’s. The intruder is not breaking down a door; they are walking in with a valid key. That is what makes stolen credentials the most expensive category per incident and one of the hardest to catch quickly.
| Insider Incident Type | Share of Incidents | Avg. Incidents / Org / Year | Cost Per Incident |
|---|---|---|---|
| Negligent employee | 53% | 13.8 | $747,107 |
| Malicious insider | 27% | 6.3 | $742,125 |
| Credential theft (outsider using insider access) | 20% | 5.3 | $842,462 |
Notice that negligence is not only the most common category, it is also expensive: at 13.8 incidents a year and $747,107 each, negligence alone accounts for roughly $10.3 million of the average organization’s annual insider-risk bill. Malicious activity accounts for about $4.7 million. That distribution is why awareness training and guardrails on data movement tend to return more than any single detection tool. This pattern mirrors what shows up in broader data breach research and cost data across the industry.
Source: Ponemon/DTEX 2026 Cost of Insider Risks Global Report | DTEX Cost of Insider Risks Analysis
The Human Element Behind Most Breaches
Zoom out from insider-specific studies to the broadest breach dataset available, and the same theme repeats. The Verizon 2025 Data Breach Investigations Report, which analyzed more than 22,000 security incidents and 12,195 confirmed breaches, found that roughly 60% of all breaches involve a human element, whether that is an error, a click on a phishing lure, or deliberate misuse.
Verizon is careful to separate outsiders from insiders. When the report looks at its Privilege Misuse and Miscellaneous Errors patterns, internal actors are the primary drivers. Those two patterns are, almost by definition, insider problems: an employee abusing legitimate access, or an employee simply making a mistake. Where breaches trace to an internal actor varies sharply by region, from 29% in EMEA down to 5% in North America and 1% in APAC.
Share of Breaches From Internal Actors, by Region (Verizon 2025 DBIR)
Myth: Insider Threats Are Mostly Rogue Employees Out to Get You
This is the most expensive misconception in the category. The data is consistent across every major source: the majority of insider incidents are accidental. Ponemon attributes 53% to negligence and only 27% to malice. Treating insider risk as a hunt for bad actors leads organizations to buy surveillance tools while ignoring the misconfigurations, weak offboarding, and untrained staff that cause most of the damage. The productive framing is risk reduction across the whole workforce, not suspicion of a few.
Source: Verizon 2025 Data Breach Investigations Report
Detection and the 67-Day Containment Problem
Insider threats are hard to catch because the activity looks legitimate. There is no malware signature when an employee downloads a customer list they are authorized to see. That is why containment drags on. Ponemon found the average insider incident now takes 67 days to contain, an improvement from 81 days in 2024, but only 13% of incidents are shut down within 30 days.
The slower it gets, the more it costs. Ponemon shows incidents contained in under 30 days cost an average of $14.2 million annualized, while those dragging past 90 days cost $21.9 million. When an insider event becomes a full breach, the clock stretches further: IBM measured 260 combined days to identify and contain a malicious-insider breach, among the slowest of any breach type.
The core difficulty is that traditional security tools are built to spot outsiders. A firewall, an antivirus engine, and an intrusion-detection system all look for something that does not belong. Insider activity, by contrast, belongs by definition. The employee is authorized to open the file, the contractor is authorized to reach the server, the service account is supposed to move that data. Detection therefore has to shift from asking whether access is allowed to asking whether the pattern of access is normal, which is precisely what user behavior analytics is designed to measure.
Annualized Insider-Risk Cost by Containment Speed (Ponemon/DTEX)
Two windows deserve special attention. The first is offboarding: with leavers roughly 69% more likely to take data, the weeks around a resignation are a measurable risk period that most organizations manage with a checklist rather than monitoring. The second is recovery. Because containment is slow, the ability to restore clean data quickly is what limits the damage, which is where tested backup and disaster recovery earns its keep.
Protect your data with tested backup and recovery
Source: Ponemon/DTEX 2026 Cost of Insider Risks Global Report | IBM Cost of a Data Breach 2025
Who Gets Hit Hardest, by Industry and Size
Insider risk is not distributed evenly. Regulated, data-rich industries pay the most, because a single mishandled record can trigger compliance penalties on top of remediation costs. Ponemon’s 2026 data shows health and pharmaceutical organizations at the top, averaging $28.8 million a year, followed by technology and software at $24.2 million, both well above the $19.5 million all-industry average.
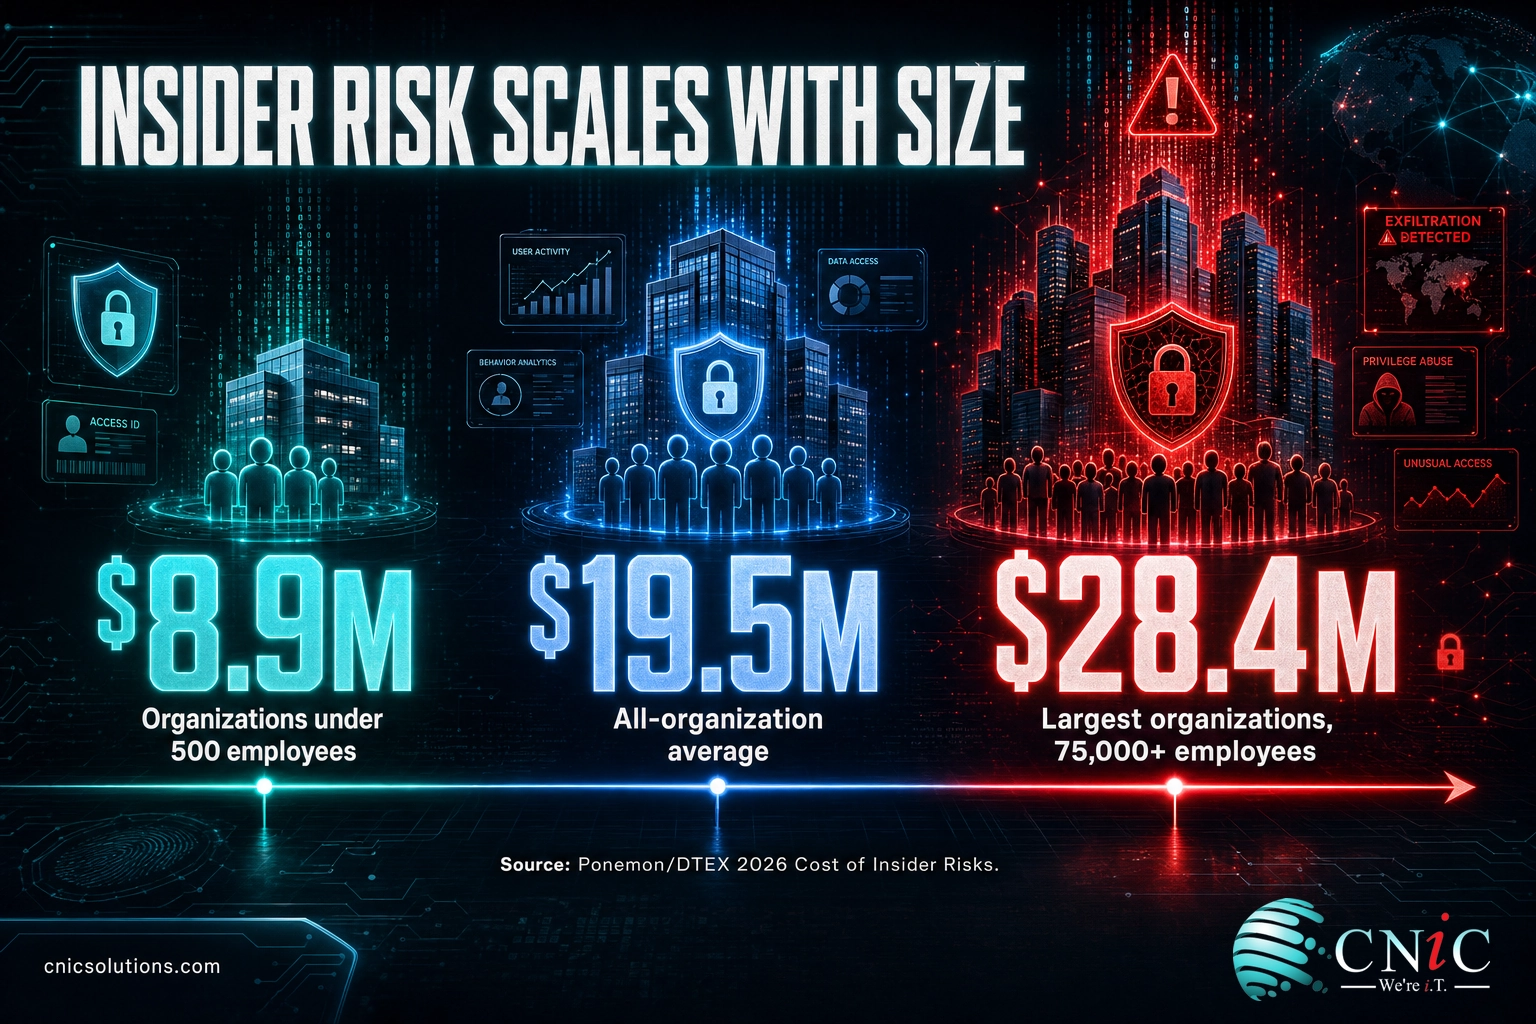
Size compounds the effect. The largest organizations, those with 75,000 or more employees, average $28.4 million, simply because more people means more access, more endpoints, and more chances for something to go wrong. Smaller organizations under 500 employees average $8.9 million, lower in absolute terms but often far more painful relative to revenue.
Average Annual Insider-Risk Cost by Industry (Ponemon/DTEX 2026)
For regulated sectors, insider risk and compliance risk are the same conversation. A single mishandled record in healthcare or finance can turn one careless insider event into a reportable breach, the same dynamic documented in our breakdown of the average cost of a data breach. The pattern holds across industries: the more sensitive the data, the higher the price of an insider slip.
Source: Ponemon/DTEX 2026 Cost of Insider Risks Global Report
What Actually Reduces Insider Risk
The good news buried in the Ponemon data is that specific controls produce measurable savings, and they are not exotic. Organizations using Privileged Access Management saved an average of $6.1 million, and those using User Behavior Analytics saved $5.1 million. Both work by shrinking the two things that make insider incidents expensive: excess access and slow detection.
The gap is capacity, not awareness. More than half of organizations, 52%, say they lack the tools to confidently handle insider threats, and 70% point to cost or technical complexity as the reason. For most small and midsize businesses, that is precisely the case for outsourcing the function to a partner who already operates the tooling and the analysts.
Average Savings by Insider-Risk Control (Ponemon/DTEX 2026)
A Practical Insider-Risk Checklist for SMBs
- Enforce least privilege. Give people access to what their role needs and nothing more, then review it quarterly.
- Watch behavior, not just logins. User behavior analytics flags the download spike or the after-hours export that a password check never will.
- Treat offboarding as a security event. Revoke access on the last day, not the following week, and monitor the notice period.
- Put guardrails on data movement, including sanctioned AI tools, so sensitive data cannot leave through an approved-looking channel.
- Train for the common case. Since 53% of incidents are negligence, awareness training targets the majority of your risk.
- Test your recovery. Fast, clean restoration is what caps the cost when detection is slow.
Many organizations get the fastest return by putting these controls under a single accountable owner. A Virtual CIO can set the access policy, choose the tooling, and own the offboarding process without the cost of a full-time security executive.
Get a Virtual CIO to own your insider-risk strategy
Source: Ponemon/DTEX 2026 Cost of Insider Risks Global Report | Cybersecurity Insiders 2024 Insider Threat Report
Summary Table: Every Stat in One Place
| Statistic | Figure | Source | Year |
|---|---|---|---|
| Average annual cost of insider risk per organization | $19.5M | Ponemon/DTEX | 2026 |
| North America average insider-risk cost | $24M | Ponemon/DTEX | 2026 |
| Europe average insider-risk cost | $18.6M | Ponemon/DTEX | 2026 |
| Rise in insider-risk cost since 2018 | +123% | Ponemon/DTEX | 2018-2026 |
| Cost per negligent-insider incident | $747,107 | Ponemon/DTEX | 2026 |
| Cost per malicious-insider incident | $742,125 | Ponemon/DTEX | 2026 |
| Cost per credential-theft incident (highest) | $842,462 | Ponemon/DTEX | 2026 |
| Share of incidents from negligence | 53% | Ponemon/DTEX | 2026 |
| Share of incidents from malicious insiders | 27% | Ponemon/DTEX | 2026 |
| Share of incidents from credential theft | 20% | Ponemon/DTEX | 2026 |
| Average time to contain an insider incident | 67 days | Ponemon/DTEX | 2026 |
| Incidents contained within 30 days | 13% | Ponemon/DTEX | 2026 |
| Average cost of a malicious-insider data breach | $4.92M | IBM | 2025 |
| Time to identify and contain a malicious-insider breach | 260 days | IBM | 2025 |
| Breaches involving a human element | ~60% | Verizon DBIR | 2025 |
| Breaches from internal actors (EMEA) | 29% | Verizon DBIR | 2025 |
| Organizations reporting at least one insider attack | 83% | Cybersecurity Insiders | 2024 |
| Organizations lacking tools to handle insider threats | 52% | Cybersecurity Insiders | 2024 |
| Savings with Privileged Access Management | $6.1M | Ponemon/DTEX | 2026 |
| Departing employees more likely to take data | 69% | DTEX | 2026 |
Frequently Asked Questions
How much do insider threats cost in 2026?
Are most insider threats malicious or accidental?
How common are insider threats?
How long does it take to detect and contain an insider threat?
What is the most expensive type of insider threat?
Methodology & Sources
Every figure in this report traces to a Tier 1 primary source. No statistic is derived from blog-to-blog citation. Figures are current as of the most recent published edition of each report at the time of writing.
- Ponemon Institute / DTEX Systems, 2026 Cost of Insider Risks Global Report. Based on interviews with 8,750 IT and security practitioners across 354 organizations. Source of annual cost, per-incident cost, incident-type distribution, containment times, industry and company-size breakdowns, and control savings.
- IBM, Cost of a Data Breach Report 2025. Source of the malicious-insider breach cost ($4.92M) and the 260-day identify-and-contain figure.
- Verizon, 2025 Data Breach Investigations Report (DBIR). Based on more than 22,000 incidents and 12,195 confirmed breaches. Source of the human-element share and internal-actor regional breakdown.
- Cybersecurity Insiders / Gurucul, 2024 Insider Threat Report. Based on a survey of more than 400 security practitioners. Source of prevalence, frequency, and readiness-gap figures.
For journalists and researchers: The statistics in this report may be cited with attribution to CNiC Solutions and a link to this page. The CNiC Solutions Analysis box (the incident-to-breach cost multiple) is original derived analysis and should be attributed to CNiC Solutions alongside the underlying Ponemon and IBM sources.
Talk to CNiC Solutions about managing insider risk


related posts
IT OKRs vs. KPIs: How to Measure What Matters
September 17, 2026Most IT reporting drowns leaders in numbers that never answer the only question that matters: is…
IT Cost Reduction Strategies: How Businesses Can Cut Tech Spend
September 17, 2026The most effective IT cost reduction strategies start with eliminating waste you are already paying for,…
IoT Security Statistics: Attacks, Vulnerabilities, and Device Growth
September 16, 2026There were 21.1 billion active IoT devices online at the end of 2025, and attackers treat…
Human Error in Cybersecurity: Statistics Every Business Should Know
September 15, 2026Most breaches do not start with a genius hacker breaking through a firewall. They start with…