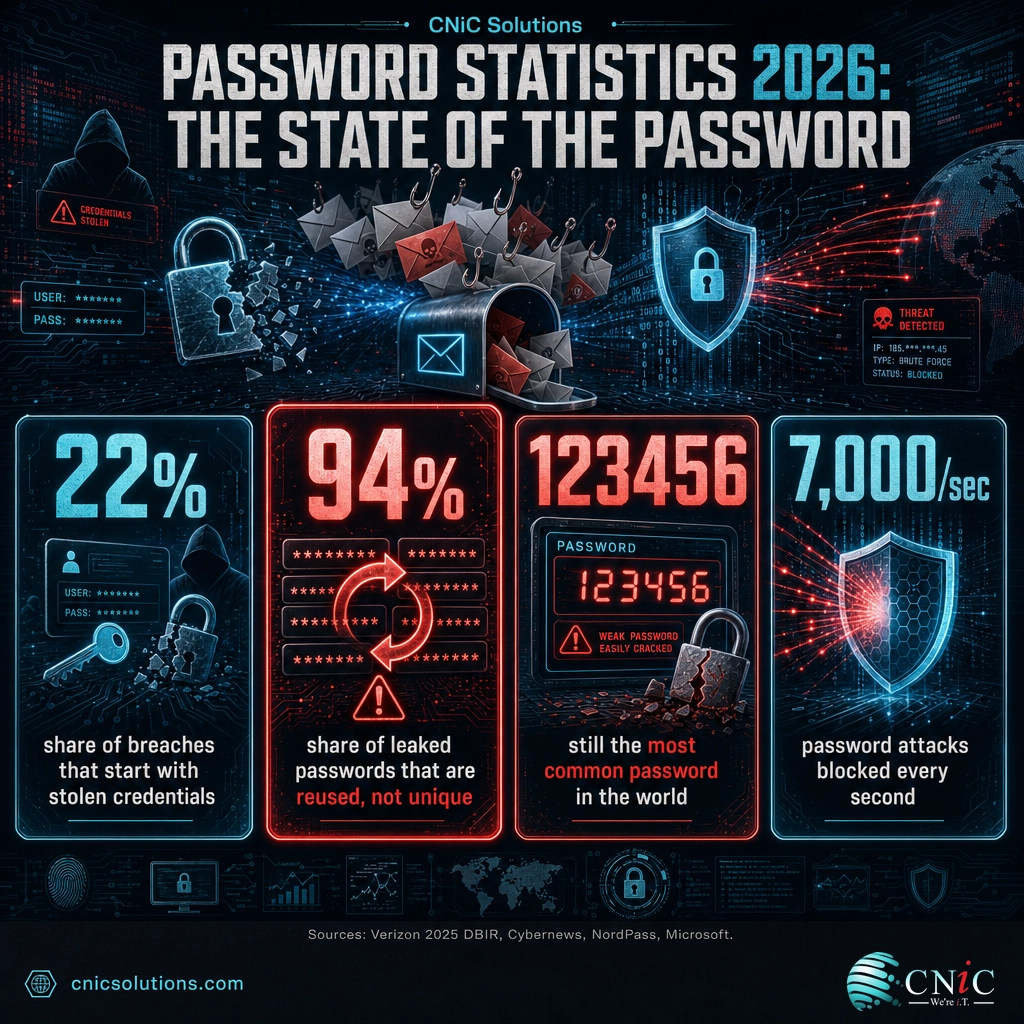
Weak and stolen passwords are still the number one way attackers get in. In 2025, stolen credentials opened 22% of all breaches, 94% of leaked passwords were reused, and “123456” was again the most common password on earth. These are the password statistics that define the risk heading into 2026.
- Passwords are the front door: stolen credentials were the initial access vector in 22% of breaches, the most common of any category for the second year running. (Verizon 2025 DBIR)
- Reuse is near-universal: only 6% of 19 billion leaked passwords were unique, so 94% were reused or duplicated. (Cybernews)
- The classics never die: “123456” was the world’s most common password for the sixth time in seven years and appeared 338 million times in leaked data. (NordPass, Cybernews)
- Most passwords fall fast: 78% of the most common passwords crack in under a second, and 98.5% of malware-stolen passwords are weak. (NordPass, Specops)
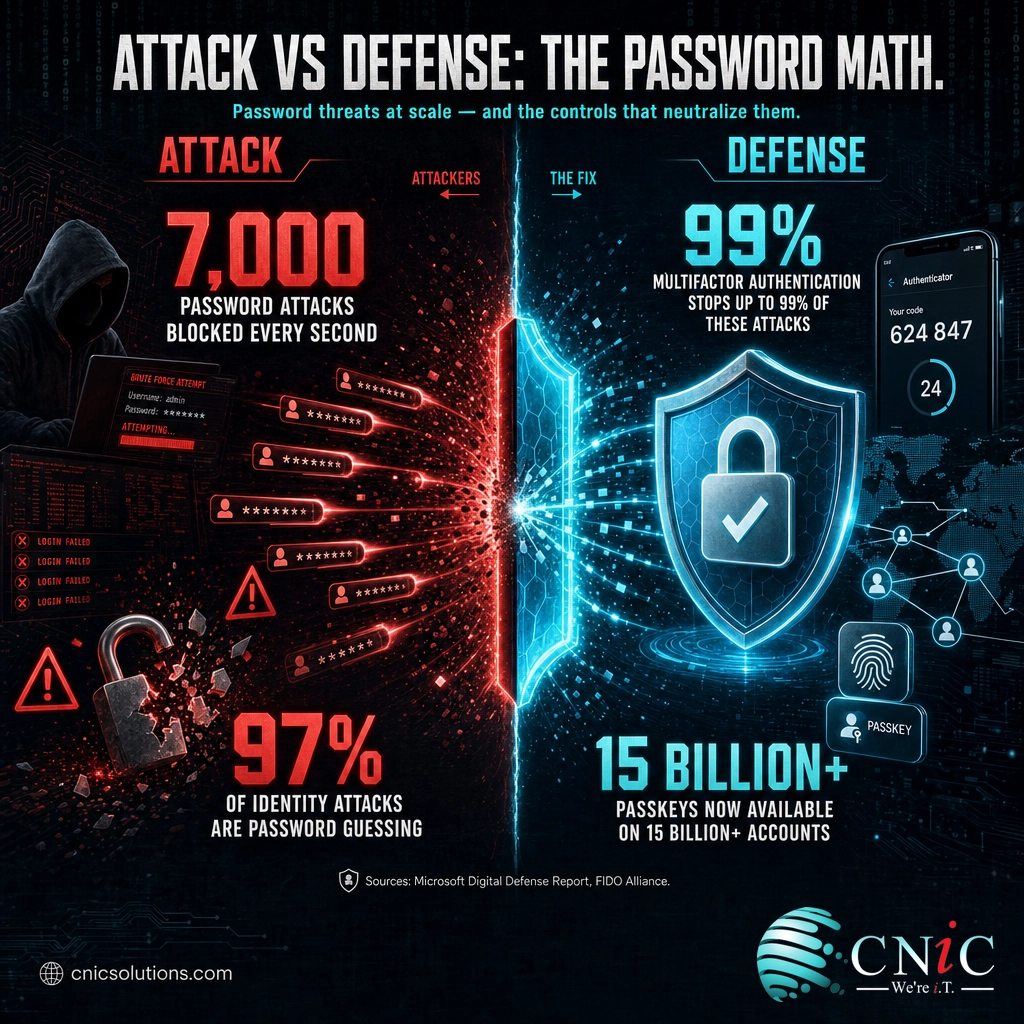
- Attacks run at machine speed: Microsoft blocks more than 7,000 password attacks per second, and 97% of identity attacks are password spray or brute force. (Microsoft Digital Defense Report)
- Length beats complexity: an 8-character complex password cracks in about 37 minutes; a 16-character one would take trillions of years. (Hive Systems)
- The fix is arriving: MFA stops up to 99% of these attacks, and passkeys are now available on 15 billion-plus accounts and 48% of the top 100 sites. (Microsoft, FIDO Alliance)
What’s in This Report
1 Passwords Are the #1 Way Into a Breach
Before looking at what makes a password weak, it helps to see why it matters. In the 2025 Verizon Data Breach Investigations Report, which analyzed more than 22,000 security incidents and 12,000 confirmed breaches, stolen credentials were the leading way attackers first got in. Passwords are not one risk among many. They are the front door.
| Credential risk metric | Figure | What it means |
|---|---|---|
| Breaches starting with stolen credentials | 22% | Top initial access vector, 2 years running |
| Web application attacks using stolen credentials | 88% | Leaked passwords are the primary weapon |
| Corporate devices in infostealer logs holding company credentials | 30% | Work passwords are actively harvested |
| Unmanaged devices in infostealer logs holding company credentials | 46% | Personal devices leak work logins faster |
The pattern is clear across every cut of the data: attackers rarely need to break down a wall when they can walk in with a working key. Infostealer malware quietly collects those keys from both company laptops and the personal devices employees use for work, which is why password hygiene and identity protection sit at the center of any serious business cybersecurity program. Our companion breakdown of human error in cybersecurity covers the mistakes that put those credentials in play.
Get a free security audit of your credential exposure
Source: Verizon 2025 Data Breach Investigations Report
2 The World’s Most Common Passwords
Year after year, the most common passwords are the ones an attacker would guess first. NordPass, working with NordStellar, studied breach and dark-web data from 44 countries gathered between September 2024 and September 2025. The results are grimly familiar.
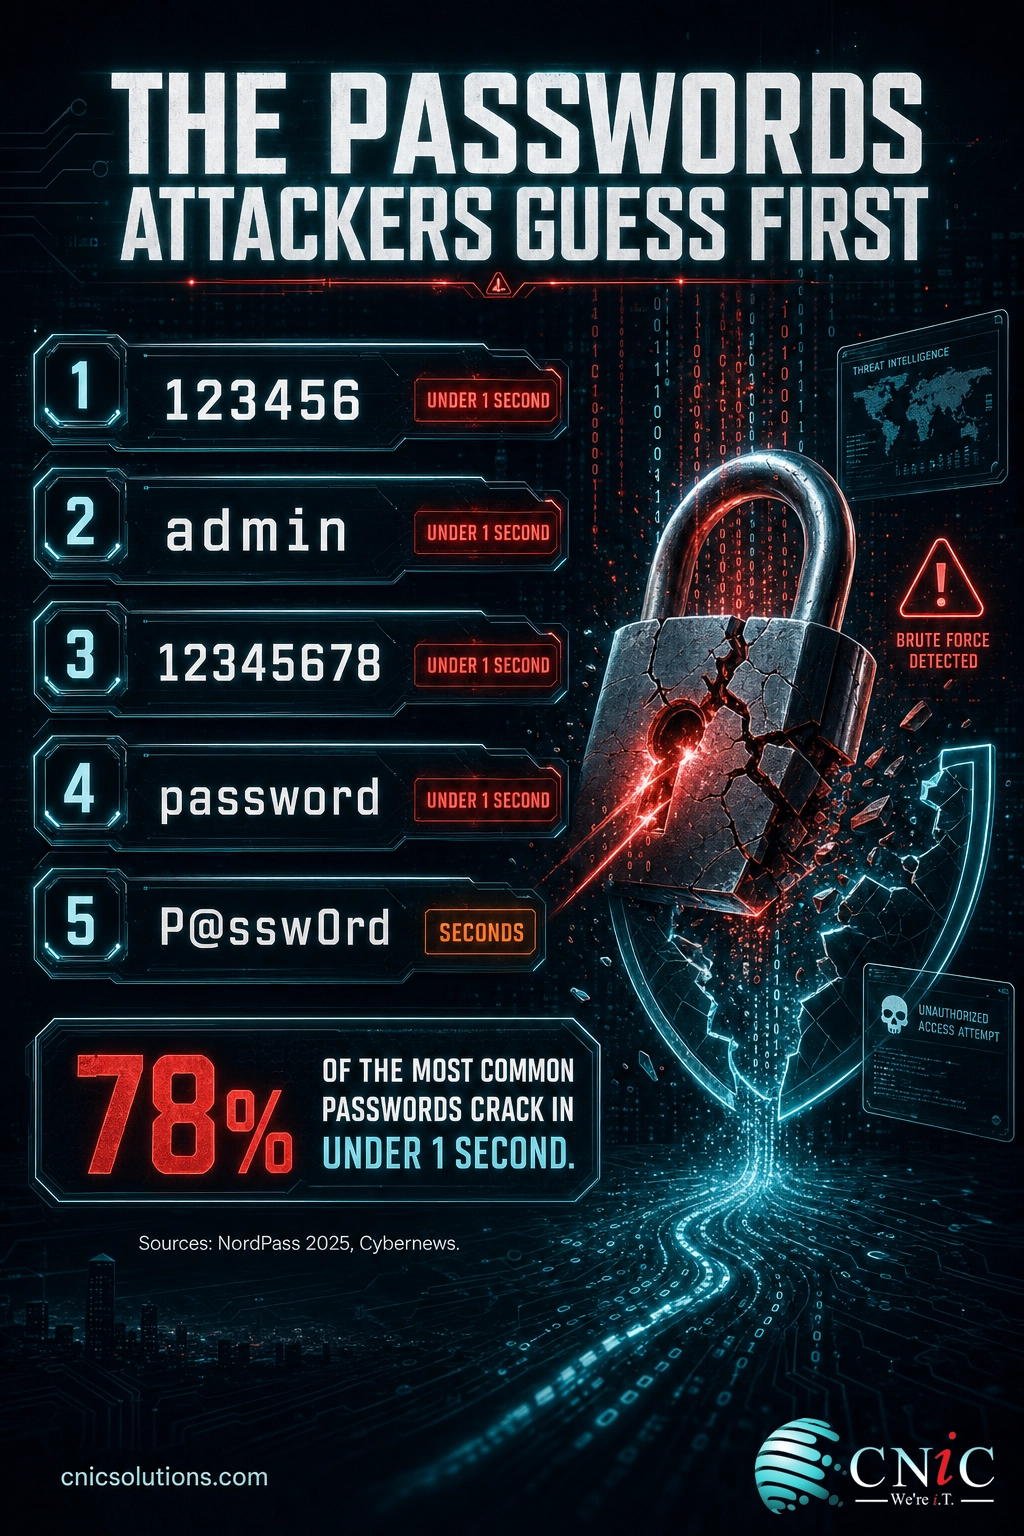
| Rank | Most common password | Note |
|---|---|---|
| 1 | 123456 | #1 globally; cracked in under a second |
| 2 | admin | #1 password in the United States |
| 3 | 12345678 | Length without complexity is still weak |
| 4 | password | A dictionary word, instantly guessed |
| 5 | Password | Capitalizing one letter does not help |
| Other | Pass@123 / P@ssw0rd / Welcome@123 | “Complex-looking” patterns are on every cracking list |
The lesson is that predictability, not just length, is the enemy. A password like “P@ssw0rd” looks like it satisfies every rule, yet it sits near the top of the lists attackers try first because millions of people reached for the same “clever” substitution. Real strength comes from length and randomness, not from swapping an “a” for an “@”. Specops confirms the scale of the problem: its top five malware-stolen passwords in 2025 were “123456,” “admin,” “12345678,” “password,” and “Password.”
Source: NordPass Top 200 Most Common Passwords | Cybernews Password Leak Study | Specops 2026 Breached Password Report
3 Password Reuse: One Leak, Many Doors
A weak password is dangerous. A weak password used in ten places is a catastrophe. Reuse is what turns a single breach at one forgotten website into a break-in at your email, your bank, and your company network, because attackers just replay the same credentials everywhere. This technique, credential stuffing, works precisely because reuse is so common.
Password Reuse by Generation
Reuse is highest among the youngest, most digitally active users. Sources: Bitwarden World Password Day Survey 2025 (Gen Z, Boomers); NordPass password-reuse survey, April 2025 (US adults).
The people juggling the most online accounts are, paradoxically, the ones most likely to protect them with the fewest passwords. That combination is exactly what credential-stuffing tools are built to exploit.
CNiC Solutions Analysis: The Blast Radius of One Reused Password. Combine three Tier 1 findings and the danger of reuse becomes concrete. Cybernews shows 94% of leaked passwords are reused. A NordPass survey finds the typical reuser leans on just three core passwords to guard about five separate accounts. Microsoft found that 85% of usernames targeted in password-spray attacks already appear in breach logs, on average across three separate breaches. Put together: a reused password is not a hypothetical risk. It is typically already leaked around three times and, once cracked, hands an attacker tested credentials to try across roughly five of that person’s accounts. Formula: 1 reused password × ~5 linked accounts (NordPass) × already exposed ~3× (Microsoft) = the blast radius of a single weak choice. Calculation and interpretation original to CNiC Solutions.
Stopping reuse is the highest-return password habit a business can enforce, and it is far easier with a password manager and a clear policy than by asking people to remember dozens of unique strings. That policy work is a core deliverable of outsourced IT leadership.
Build a password policy that actually holds
Source: Cybernews Password Leak Study | NordPass password-reuse survey | Bitwarden World Password Day Survey | Microsoft Digital Defense Report
4 How Fast a Password Actually Cracks
Most people assume a password with a capital letter and a number is “strong enough.” The cracking data says otherwise. What protects a password is length and randomness, because every extra character multiplies the number of guesses a computer must make, while every dictionary word or common pattern cuts that number to almost nothing.
| Password (all four character types) | Time to crack on modern GPU hardware |
|---|---|
| 8 characters, lowercase only | Instantly |
| 8 characters, mixed case + numbers + symbols | ~37 minutes |
| 12 characters, mixed case + numbers + symbols | Centuries |
| 16 characters, mixed case + numbers + symbols | Trillions of years |
The table shows why length wins. Moving from 8 to 16 characters, with the same mix of character types, is the difference between 37 minutes and effectively forever. That is the reasoning behind modern guidance from NIST, which now favors long passphrases over short strings loaded with forced symbols. Specops confirms attackers are harvesting passwords at every common length: more than 4.4 billion of the passwords they analyzed were between 8 and 12 characters, the exact zone most corporate policies still allow.
Myth: “Adding a symbol makes my password strong.” Swapping letters for symbols in a familiar word, turning “password” into “P@ssw0rd,” does almost nothing. Those substitutions are the first thing cracking software tries, which is why “P@ssw0rd” appears on breached-password lists. Real strength comes from length and unpredictability. A random 16-character passphrase beats a short, clever-looking string every time, and a password manager makes generating one effortless.
Put password hygiene on autopilot with managed IT
Source: Specops Breached Password Analysis | Cybernews Password Leak Study | Hive Systems Password Table
5 Credential Attacks at Machine Scale
Attackers do not guess passwords by hand. They run automated tools that test millions of stolen or common credentials against login pages every hour, all day. Microsoft, which sees a large share of global sign-in traffic through its identity platform, measures the onslaught directly.
| Attack-scale metric | Figure | Source |
|---|---|---|
| Password attacks blocked per second | 7,000+ | Microsoft DDR 2024 |
| Identity attacks tracked per day | 600 million | Microsoft DDR 2024 |
| Identity attacks that are password-based | 97% | Microsoft DDR 2025 |
| Rise in identity attacks, first half of 2025 | +32% | Microsoft DDR 2025 |
| Spray-targeted usernames already found in leaks | 85% | Microsoft, 2025 |
The takeaway for a small or midsize business is that no human team can watch 7,000 attempts a second. Defense at that scale has to be automated: rate-limiting, lockout policies, breached-password screening, and monitoring that flags an impossible login before it becomes a breach. When those controls fail, fast recovery is what keeps a compromised account from becoming a company-wide outage.
Build recovery for when a credential is compromised
Source: Microsoft Digital Defense Report 2024 | Microsoft Digital Defense Report 2025
6 What Works: MFA and the Passkey Shift
The password statistics paint a bleak picture, but the defense statistics are genuinely encouraging. Two controls change the math almost completely: multifactor authentication, which adds a second proof of identity, and passkeys, which replace the password with a cryptographic key stored on your device and never typed or reused.
Top 100 Websites Supporting Passkeys
Passkey support among the top 100 sites has more than doubled since 2022. Source: FIDO Alliance 2025.
The momentum is real: Google reports more than 800 million accounts using passkeys, and Amazon has passed 175 million customers with passkeys enabled. For a business, the near-term move is simpler and just as powerful: turn on phishing-resistant MFA everywhere it is available, because that one step stops the overwhelming majority of the password attacks documented above. If you are weighing the switch, our guide to how passkeys and passwordless login work explains the mechanics in plain terms.
Roll out MFA and passkeys across your cloud apps
Source: FIDO Alliance Passkey Index | Microsoft Security Blog
7 Every Password Statistic in One Table
A single reference view of every figure in this report, with its primary source and year. Journalists and analysts are welcome to cite these with attribution.
| Statistic | Figure | Source | Year |
|---|---|---|---|
| Breaches starting with stolen credentials | 22% | Verizon DBIR | 2025 |
| Web application attacks using stolen credentials | 88% | Verizon DBIR | 2025 |
| Breaches involving a human element | 60% | Verizon DBIR | 2025 |
| Corporate devices in infostealer logs with company credentials | 30% | Verizon DBIR | 2025 |
| Unmanaged devices in infostealer logs with company credentials | 46% | Verizon DBIR | 2025 |
| Most common password in the world | 123456 | NordPass | 2025 |
| Appearances of “123456” in leaked data | 338 million | Cybernews | 2025 |
| Most common passwords crackable in under 1 second | 78% | NordPass (6th ed.) | 2024 |
| Leaked passwords that were reused or duplicated | 94% | Cybernews | 2025 |
| Leaked passwords that were unique | 6% | Cybernews | 2025 |
| Americans who often or always reuse passwords | 62% | NordPass survey | 2025 |
| Password reuse, Gen Z vs Boomers | 72% vs 42% | Bitwarden | 2025 |
| Malware-stolen passwords rated weak | 98.5% | Specops / Outpost24 | 2025 |
| Leaked passwords that were 8 to 10 characters | 42% | Cybernews | 2025 |
| Leaked passwords using only lowercase + digits | 27% | Cybernews | 2025 |
| Crack time, 8-char complex password | ~37 minutes | Hive Systems | 2024 |
| Crack time, 16-char complex password | Trillions of years | Hive Systems | 2024 |
| Password attacks blocked per second | 7,000+ | Microsoft DDR | 2024 |
| Identity attacks that are password-based | 97% | Microsoft DDR | 2025 |
| Rise in identity attacks, H1 2025 | +32% | Microsoft DDR | 2025 |
| Attacks MFA can prevent | Up to 99% | Microsoft | 2025 |
| Online accounts that can use passkeys | 15 billion+ | FIDO Alliance | 2025 |
| People who have activated a passkey | 1 billion+ | FIDO Alliance | 2025 |
| Top 100 websites supporting passkeys | 48% | FIDO Alliance | 2025 |
| Google accounts using passkeys | 800 million+ | FIDO Alliance / Google | 2025 |
8 Frequently Asked Questions
What is the most common password in 2026?
How many passwords are reused?
How fast can a password be cracked in 2026?
What percentage of data breaches are caused by weak or stolen passwords?
Do passkeys and multifactor authentication actually stop password attacks?
9 Methodology and Sources
How this report was compiled
Every figure in this article is drawn from a Tier 1 primary source: annual industry breach reports, major vendor and analyst research with disclosed methodology, and standards bodies. No statistic is sourced from a blog citing another blog, and no figure is invented or estimated except the clearly labeled CNiC Solutions Analysis, which shows its formula and contributing sources. Where a figure describes 2024 rather than 2025, that year is stated alongside it.
Primary sources
- Verizon 2025 Data Breach Investigations Report (DBIR): credentials as initial access vector, web application attack data, human element, infostealer figures.
- NordPass Top 200 Most Common Passwords (2025, 7th edition, with NordStellar): most common passwords worldwide and the US “admin” result. The share of common passwords cracked in under one second (78%, up from 70%) is from the 2024 sixth edition of this research.
- NordPass password-reuse survey (April 2025, 1,727 adults including 619 Americans): 62% of Americans often or always reuse a password; the median reuser relies on about three core passwords across roughly five accounts.
- Cybernews Password Leak Study (19 billion passwords, April 2024 to April 2025): reuse rate, uniqueness, length and composition, “123456” frequency.
- Specops 2026 Breached Password Report (with Outpost24): malware-stolen password weakness and length distribution.
- Bitwarden World Password Day Survey 2025: self-reported password reuse by generation (72% of Gen Z versus 42% of Boomers).
- Hive Systems Password Table (2024): GPU crack-time benchmarks by length and complexity.
- Microsoft Digital Defense Report (2024 and 2025 editions): attack volume, share of password-based identity attacks, MFA effectiveness.
- FIDO Alliance Passkey Index (2025): passkey availability, activation, and site support.
Press and citation use. Journalists, analysts, and researchers are welcome to cite the statistics in this report with attribution to CNiC Solutions and a link to this page, alongside the original primary source noted for each figure. The CNiC Solutions Analysis box may be cited as original analysis.


related posts
What Is IT Asset Management (ITAM)? A Guide for Businesses
October 22, 2026IT asset management (ITAM) is the practice of tracking and managing an organization's hardware, software, and…
What Is ISO 27001? A Guide to the Information Security Standard
October 22, 2026ISO 27001 is the world's best-known standard for managing information security, and increasingly the certification customers…
What Is Infrastructure as Code (IaC)? A Guide for Businesses
October 21, 2026Infrastructure as Code (IaC) is the practice of managing and provisioning IT infrastructure, such as servers,…
What Is Infrastructure Security? A Guide for Businesses
October 21, 2026Infrastructure security is the practice of protecting the core technology systems a business runs on: its…