Zero-day vulnerability, defined: A zero-day vulnerability is a software or hardware flaw that the vendor does not yet know about, so no patch exists to fix it. Whoever discovers it first can exploit it immediately, before defenders have any warning. The name means developers have had zero days to prepare a fix.
Every security tool you own is built to recognize a known threat. A zero-day vulnerability is the opposite: a flaw nobody has cataloged, patched, or written a detection rule for yet. That gap is exactly why attackers prize them, and why the number of zero-days hitting business software keeps climbing. This guide explains what a zero-day is, how these attacks unfold step by step, and the practical defenses that limit the damage even when no patch is available.
- A zero-day vulnerability is a flaw with no patch, because the vendor does not yet know it exists.
- Google’s Threat Intelligence Group tracked 75 zero-days exploited in the wild in 2024, and 44% of them targeted enterprise technology like security appliances and VPNs.
- “Vulnerability” (the flaw), “exploit” (the attack code), and “attack” (the exploit in use) are three different stages that people constantly confuse.
- Vulnerability exploitation as a way into a breach jumped 34% year over year in Verizon’s 2025 Data Breach Investigations Report.
- You cannot patch a flaw nobody knows about, so layered defense (EDR, network segmentation, tested backups, and fast patching once a fix ships) is how businesses stay resilient.
What’s in This Guide
How a Zero-Day Attack Works
A zero-day attack follows a predictable life cycle, even though its timing catches defenders off guard. Think of it like a burglar who finds an unlocked window the builder never knew was faulty. The builder cannot warn homeowners about a defect they have not discovered, and the burglar has free entry until someone spots the problem and fixes it.
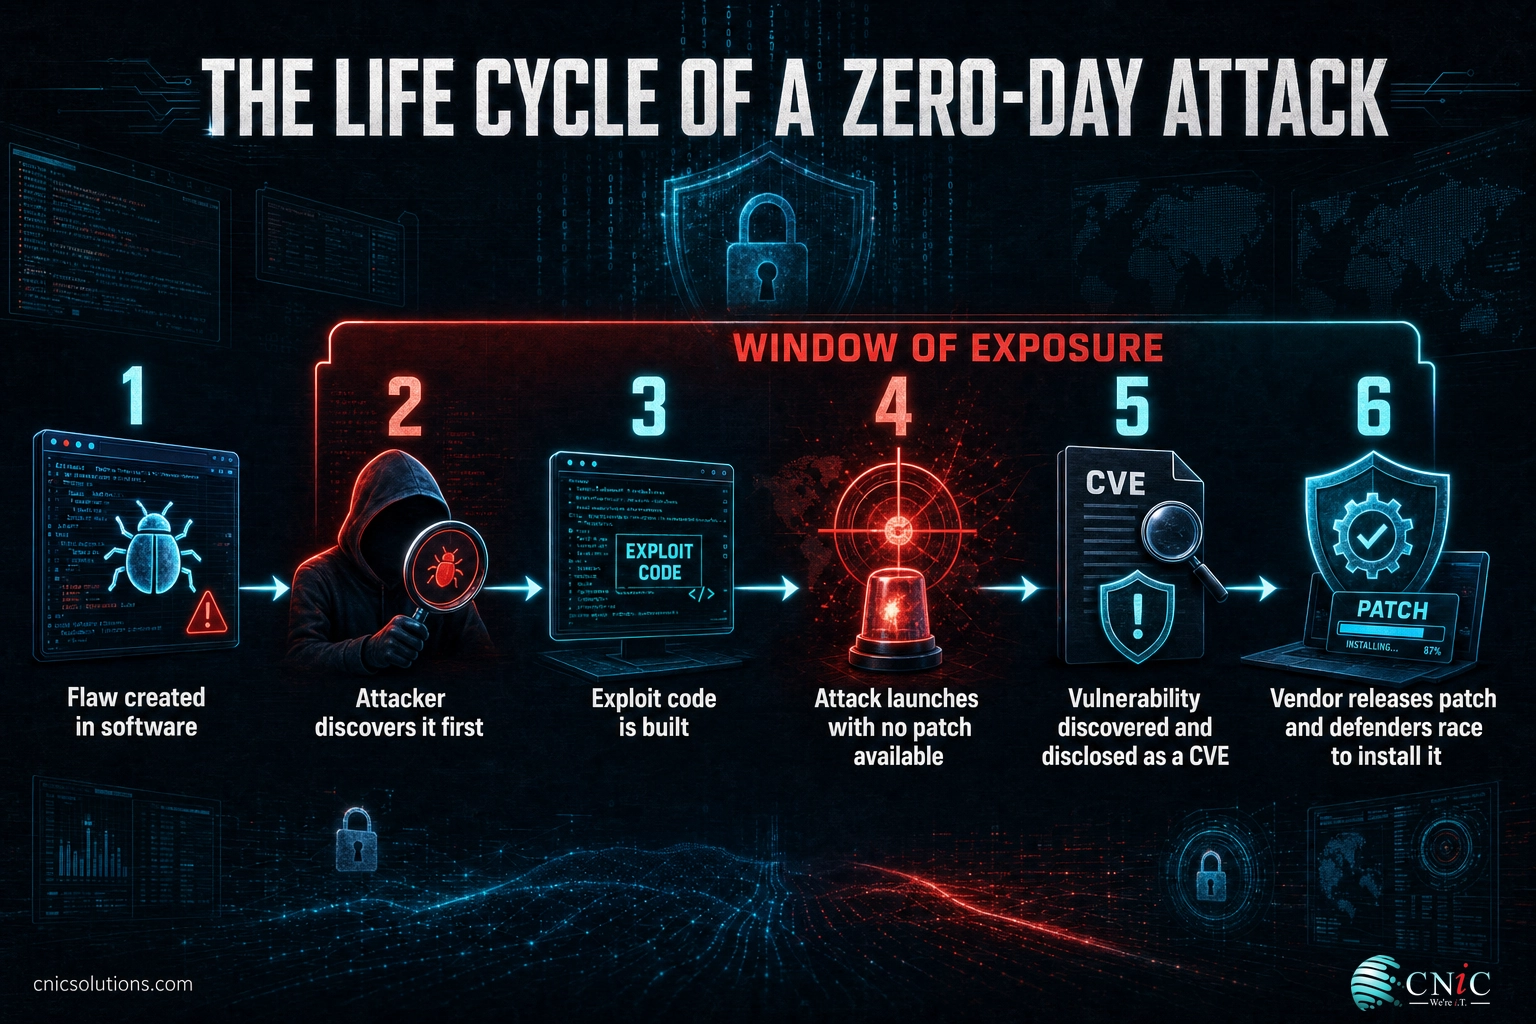
Here is how that plays out with software, step by step:
- A flaw is created. A developer ships code with an unintended weakness, a coding mistake, a logic error, or an insecure default that no one catches in testing.
- An attacker finds it first. A threat actor, researcher, or broker discovers the flaw before the vendor does. From this moment, the clock on a “zero-day” starts, because the vendor has had zero days to respond.
- An exploit is built. The attacker writes code, called an exploit, that reliably abuses the flaw to run commands, steal data, or gain control.
- The attack launches. The exploit is used against real targets. Because there is no patch and often no detection signature, the activity can go unnoticed.
- Discovery and disclosure. Eventually the vendor, a researcher, or an incident responder identifies the vulnerability. It gets a public identifier (a CVE number) and, once patched, is added to catalogs like CISA’s Known Exploited Vulnerabilities Catalog.
- The patch race. The vendor releases a fix. Now every organization running that software has to install the patch before attackers exploit the (now public) flaw on machines that are still unpatched.
The dangerous stretch is between steps two and six, sometimes called the “window of exposure.” For a true zero-day, that window is open before anyone but the attacker knows it exists. The U.S. National Institute of Standards and Technology captures this in its official definition of a zero-day attack: an attack that exploits a previously unknown vulnerability, giving developers zero days to create a fix.
Source: NIST Computer Security Resource Center | CISA Known Exploited Vulnerabilities Catalog
Zero-Day Vulnerability vs. Exploit vs. Attack
These three terms get used interchangeably, and that confusion trips up even technical teams. They describe three distinct stages of the same problem. Getting them straight helps you understand exactly where your defenses can intervene.
| Term | What it is | Plain-English example |
|---|---|---|
| Zero-day vulnerability | The unknown flaw itself, still unpatched because the vendor is unaware of it. | An unnoticed weakness in file-transfer software that lets a crafted request read the database. |
| Zero-day exploit | The code or technique an attacker writes to abuse that flaw. | The malicious request specifically built to trigger that weakness on demand. |
| Zero-day attack | The exploit actually used against a live target to cause harm. | Criminals running that exploit across thousands of servers to steal customer data. |
A helpful shorthand: the vulnerability is the unlocked door, the exploit is the key cut to fit it, and the attack is the burglar walking through. A vulnerability that is never weaponized causes no direct harm, which is why responsible researchers report flaws privately so vendors can patch before criminals build an exploit.
Source: NIST Computer Security Resource Center
Why Zero-Day Attacks Matter for Your Business
Zero-days are not just a problem for governments and tech giants. The data shows exploitation of software flaws becoming a mainstream way into ordinary business networks, and the warning time defenders get is shrinking fast.
The counts move year to year, but the trend beneath them is what matters. Attackers are pointing zero-days at the exact tools businesses rely on for protection, and they are moving faster than ever. Google’s Mandiant team has tracked the median “time-to-exploit,” the gap between a flaw becoming public and the first attacks, collapsing from months a few years ago toward days, with many vulnerabilities now hit as zero-days before any patch exists at all.
Zero-Day Vulnerabilities Exploited in the Wild, by Year
Source: Google Threat Intelligence Group, 2024 Zero-Day Exploitation Analysis.
Myth: “We’re too small to be hit by a zero-day, and our software is fully patched anyway.” Both halves are wrong. A zero-day has no patch by definition, so being current on updates does not protect you from one. And you rarely need to be the target: when attackers exploit a zero-day in widely used business software, everyone running it is exposed at the same moment. Size does not grant immunity when the whole customer base is the attack surface.
The business impact is concrete: data theft, ransomware deployment, regulatory penalties, and downtime. For a fuller picture of how exploited flaws feed real incidents, our team keeps a running breakdown in the latest vulnerability exploitation data, which tracks exploited CVEs and time-to-exploit trends.
Source: Google Threat Intelligence Group | Verizon 2025 Data Breach Investigations Report | Mandiant time-to-exploit analysis
Real-World Zero-Day Examples
Abstract definitions land better with real cases. Two of the most instructive zero-day attacks bookend the modern era, one a nation-state weapon, the other a criminal data heist that swept up thousands of everyday organizations.
Stuxnet (2010): the zero-day as a weapon
Stuxnet is the most famous zero-day attack in history. The worm chained together four separate previously unknown Windows vulnerabilities, including a Windows shortcut flaw and a print spooler bug, to spread silently and sabotage industrial equipment. Using four zero-days in a single operation was unheard of and signaled that vulnerabilities had become strategic weapons. The U.S. Cybersecurity and Infrastructure Security Agency documented the malware and its mitigations in a dedicated CISA industrial control systems advisory.
MOVEit (2023): one flaw, thousands of victims
The MOVEit breach shows why small and midsize businesses cannot dismiss zero-days as someone else’s problem. In May 2023, the Cl0p ransomware group exploited a previously unknown SQL injection flaw (CVE-2023-34362) in MOVEit Transfer, a popular file-transfer product, before its maker knew the bug existed. Because so many organizations and their vendors used the software, a single zero-day cascaded into data theft affecting thousands of organizations worldwide. CISA and the FBI published joint guidance on the Cl0p MOVEit exploitation as the campaign unfolded. Many victims were breached not because they were targeted, but because a tool in their supply chain was.
The pattern connecting both cases is the same one behind modern ransomware: attackers get in through an unpatched or unknown flaw, then escalate. If you want to see how that entry point turns into a full incident locally, review our breakdown of ransomware attack patterns affecting Texas businesses.
Source: CISA ICS Advisory (Stuxnet) | CISA Advisory AA23-158A (MOVEit / Cl0p)
Where Zero-Day Flaws Hide
Zero-days are not limited to one kind of product. They surface anywhere code runs, but attackers concentrate on software that is widely deployed or sits in a privileged position. The most commonly exploited categories include:
- Operating systems and browsers. Windows, macOS, Chrome, and Safari are high-value because a single flaw can reach millions of endpoints.
- Security and network appliances. VPNs, firewalls, and gateways are increasingly targeted precisely because they are trusted and internet-facing. Google found a growing share of 2024 zero-days aimed here.
- Business and file-transfer applications. Tools like MOVEit that handle sensitive data at scale offer attackers a large payoff from one flaw.
- Firmware and IoT devices. Cameras, routers, and connected hardware often run rarely updated code, so a flaw can linger for years.
This is why “just patch faster” is necessary but not sufficient. The riskiest zero-days often live in the very systems meant to keep attackers out, which means your defense cannot depend on any single product being flawless.
Source: Google Threat Intelligence Group
How to Protect Your Business From Zero-Day Attacks
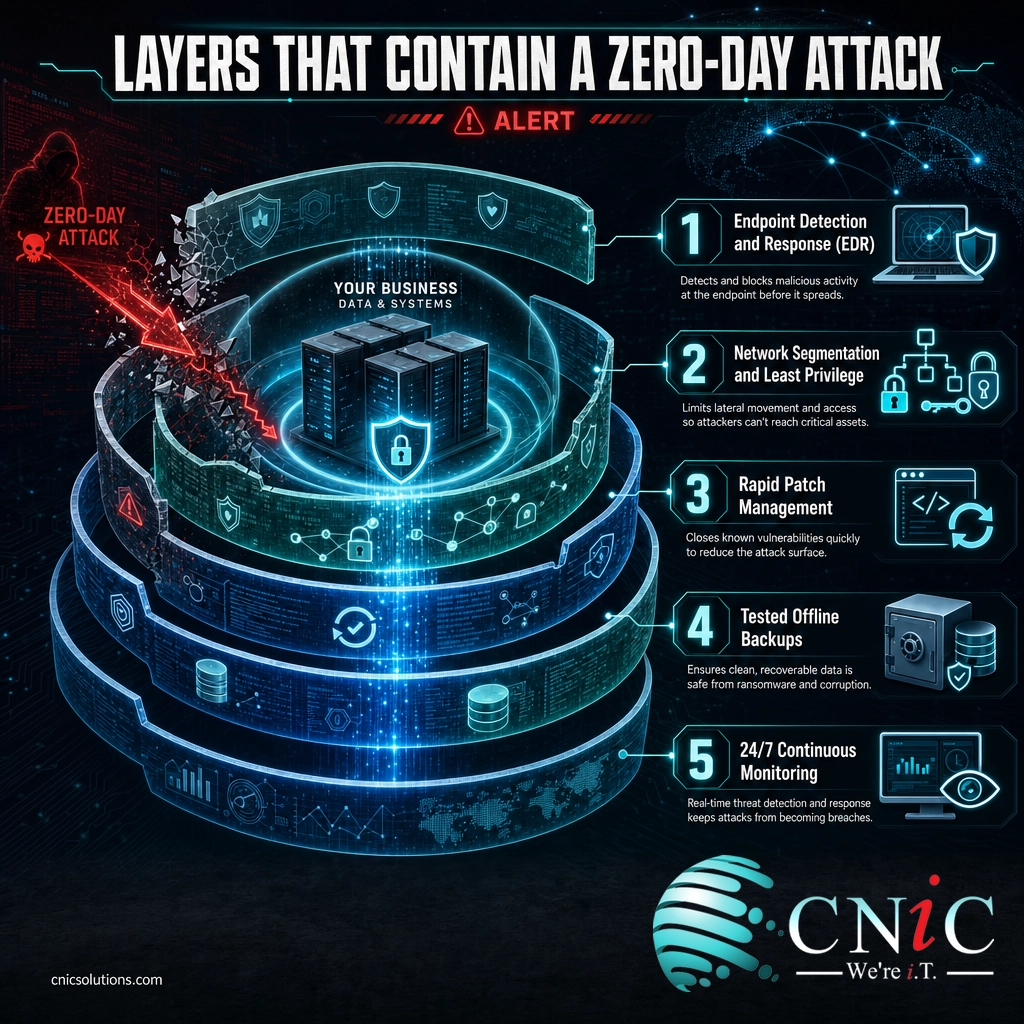
You cannot patch a vulnerability nobody knows about. That reality frustrates business owners, but it points straight to the answer: defense in depth. When you assume any one control can fail, you build layers so an attacker who slips past the first still runs into the next. The goal is to detect and contain a zero-day exploit even before a patch exists.
The layers that matter most for small and midsize businesses:
- Behavior-based endpoint detection (EDR). Signature antivirus looks for known threats and misses zero-days. EDR watches for suspicious behavior (a document spawning a command shell, unusual data movement) and can flag an exploit it has never seen. See our guide to endpoint detection and response tools for smaller teams.
- Network segmentation and least privilege. If an attacker exploits one machine, segmentation and tight permissions stop them from reaching everything else, which is what turned zero-day footholds like MOVEit into full breaches.
- Rapid patch management. The moment a fix ships, a zero-day becomes a race. A disciplined patch process closes the window before attackers reach your still-vulnerable systems.
- Tested, offline backups. If a zero-day leads to ransomware, clean and recent backups are what let you recover without paying.
- Continuous monitoring. Round-the-clock detection shortens the time an intruder goes unnoticed, which is often the difference between a contained incident and a headline.
For most businesses, assembling and running these layers in-house is impractical. That is where a managed security partner earns its keep, providing the monitoring, EDR, and patch discipline that catch and contain threats no signature can predict.
Explore Managed IT & Security Services
Recovery matters as much as prevention. When an exploit does land, the businesses that bounce back fastest are the ones with tested backups and a rehearsed recovery plan already in place.
See Backup & Disaster Recovery
Not sure where your gaps are? A structured review pinpoints which systems are exposed and which layers you are missing. Start with a cybersecurity risk assessment, or bring in outside leadership to prioritize the roadmap.
Source: CISA Known Exploited Vulnerabilities Catalog | Verizon 2025 Data Breach Investigations Report
Common Questions About Zero-Day Vulnerabilities
What does “zero-day” actually mean?
What is the difference between a zero-day vulnerability and a zero-day exploit?
Can antivirus stop a zero-day attack?
How long does a zero-day stay dangerous?
Are small businesses really targeted by zero-days?
Related Security Terms
- Exploit: The code or technique that turns a vulnerability into a working attack.
- CVE (Common Vulnerabilities and Exposures): The public catalog ID assigned to a disclosed vulnerability once it is known.
- Patch: The vendor’s fix that closes a vulnerability; installing it fast is what ends a zero-day’s danger.
- Endpoint security: Protection for the laptops, servers, and devices attackers reach first, and a primary layer for catching zero-day activity. See what endpoint security is and how it works.
- Ransomware: Malware that encrypts your data for extortion, frequently delivered through an exploited vulnerability.
- Phishing: Deceptive messages that trick users into handing over access, often the delivery method for an exploit. Learn how to spot a phishing email.
- Defense in depth: Layering multiple independent controls so one failure does not become a breach.
Sources & Methodology
All statistics in this article come from primary, Tier-1 sources and reflect the most recent figures available at publication. Vulnerability counts and exploitation trends are from published threat-intelligence and breach research, not secondary aggregation. Real-world examples are documented in official government advisories.
- Google Threat Intelligence Group, “A 2024 Zero-Day Exploitation Analysis” (2024 zero-day counts, enterprise-targeting share, attribution).
- Verizon 2025 Data Breach Investigations Report (vulnerability exploitation as an initial access vector).
- Mandiant / Google Cloud time-to-exploit analysis (shrinking time-to-exploit).
- NIST Computer Security Resource Center glossary (zero-day attack definition).
- CISA Known Exploited Vulnerabilities Catalog.
- CISA ICS Advisory ICSA-10-272-01 (Stuxnet) and Advisory AA23-158A (MOVEit / Cl0p).


related posts
What Is ZTNA (Zero Trust Network Access)?
November 3, 2026Zero Trust Network Access (ZTNA) is a security service that grants a verified user access to…
Zero Trust Statistics for 2026: Adoption, Maturity, and Breach Impact
November 3, 2026Zero trust has become the default security strategy on paper, but not yet in practice. Okta's…
What Is XDR (Extended Detection and Response) and How Does It Protect…
November 2, 2026Extended detection and response (XDR) is a security platform that collects and correlates threat data from…
What Is Zero Trust Security? A Guide for Small Businesses
November 2, 2026Zero Trust security is a cybersecurity model built on one rule: never trust, always verify. Instead…