Zero Trust Network Access (ZTNA) is a security service that grants a verified user access to one specific application, never the entire network, after checking identity, device, and context on every request. It follows a default-deny, least-privilege model and keeps applications hidden from the public internet.
For twenty years, remote access meant a VPN: prove who you are once, and the network opens up to you. That model was built for a world where the important systems sat inside an office and a few people dialed in from outside. Today the apps live in the cloud, the workforce is everywhere, and attackers have learned that a single stolen VPN login is a skeleton key to the whole building. ZTNA is the answer to that problem. Instead of trusting anyone who gets through the front door, it verifies every request and hands out access one application at a time.
- ZTNA grants access to apps, not networks. A verified user reaches only the specific application a policy allows, so a breach cannot spread sideways across the network.
- It defaults to deny. Nothing is reachable until a policy explicitly permits it, and applications stay invisible to the open internet until access is granted.
- It is the modern replacement for the VPN. Gartner forecast that by 2025 at least 70% of new remote access deployments would rely on ZTNA rather than VPN services, up from less than 10% at the end of 2021.
- VPNs have become a target. In the Verizon 2025 DBIR, edge devices and VPNs made up 22% of the vulnerabilities attackers exploited, nearly eight times the 3% seen a year earlier.
- ZTNA is one piece of Zero Trust, not all of it. It applies Zero Trust principles to access, and works alongside identity policy, segmentation, and monitoring.
What’s in This Guide
How ZTNA Works
The whole idea of ZTNA rests on a phrase from the Zero Trust model: never trust, always verify. A traditional network assumes that once you are “inside,” you are trustworthy. ZTNA throws that assumption out. It treats every access request as if it came from an open, hostile network, even when it starts from a corporate laptop, and it re-checks the request each time rather than trusting a one-time login.
Think of it like a hotel keycard instead of a master key. A VPN hands a guest the master key to the entire building. ZTNA gives them a keycard that opens only their own room, only for the length of their stay, and only after the front desk has confirmed who they are. If that card is copied, the thief still cannot open anyone else’s door.
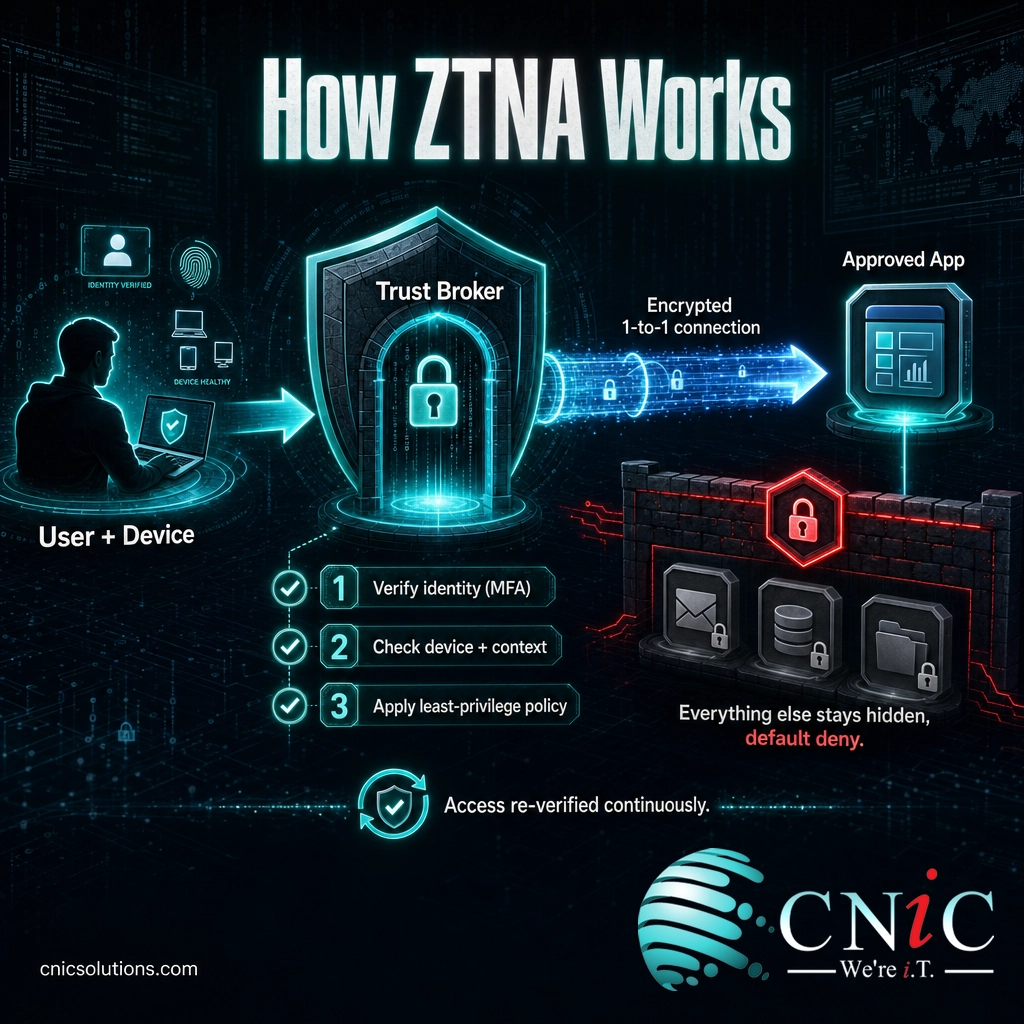
Under the hood, a component called a trust broker (sometimes a controller or policy engine) sits between users and applications and runs the same sequence on every connection:
- A request arrives. A user and their device ask to reach a specific application, not the network at large.
- Identity is verified. The broker confirms the user through your identity provider, typically with multifactor authentication, so a password alone is never enough.
- Context is checked. It weighs signals such as device health and patch level, location, time, and real-time risk before making any decision.
- Least-privilege access is granted. If the policy allows it, the broker opens an encrypted, one-to-one connection to that single application. Everything else stays dark, and the app is never exposed to the public internet.
- Trust is continuously re-checked. The session is monitored, and if the context changes (a device falls out of compliance, risk spikes), access can be challenged again or cut off.
The critical difference from older tools is in that fourth step. ZTNA never places the user “on the network.” It connects them to an application through the broker, which is why a compromised account or device cannot roam laterally to reach servers, file shares, or systems it was never authorized to touch. This principle, verify explicitly and enforce least privilege, comes straight from the federal Zero Trust standard.
Source: NIST Special Publication 800-207, Zero Trust Architecture | CISA Zero Trust Maturity Model
ZTNA vs. VPN
This is the comparison that matters most, because ZTNA is usually bought to solve the problems a VPN creates. Both give remote users a secure connection to company resources, but they take opposite approaches to trust. A VPN authenticates you once and then extends the network to your device, so you are treated as an insider with broad reach. ZTNA authenticates every request and connects you to one application at a time, so you are treated as an outsider who has to earn each door.
That difference is not academic. When an attacker steals VPN credentials or exploits an unpatched VPN appliance, they inherit that broad insider access, which is exactly why VPN gateways have become such a popular target. ZTNA shrinks the blast radius: a stolen identity reaches only the handful of apps that identity was allowed to use, and there is no public gateway sitting on the internet waiting to be exploited.
| Attribute | Traditional VPN | ZTNA |
|---|---|---|
| Trust model | Authenticate once, then trust the user on the network | Verify identity, device, and context on every request |
| What you reach | The whole network segment the VPN connects to | Only the specific applications policy allows |
| Default posture | Allow, then restrict | Deny, then explicitly permit |
| Internet exposure | A public gateway that attackers can find and probe | Apps are hidden; nothing is published to the internet |
| Blast radius if breached | Broad lateral movement across the network | Contained to the few apps the identity was granted |
| Best suited for | Legacy full-network access for a trusted few | Cloud apps, hybrid work, contractors, least privilege |
None of this means a VPN is worthless overnight. Plenty of businesses still run one for specific legacy needs while they move the rest of their access to ZTNA. But the direction of travel is clear, and it is being driven by the security math rather than by marketing. If your remote access still rests entirely on a VPN, it is worth understanding how a Zero Trust approach changes your exposure, much as conditional access policies changed the math on stolen passwords.
Source: Gartner glossary, Zero Trust Network Access (ZTNA) | Verizon 2025 Data Breach Investigations Report
Why ZTNA Matters for Your Business
The case for ZTNA is not built on hype. It is built on how breaches actually happen. Attackers rarely smash through a wall; they log in with a stolen credential or slip through an exposed edge device. Both of those are the doors a VPN leaves open and a ZTNA model closes.
Start with credentials. In the Verizon 2025 Data Breach Investigations Report, the use of compromised credentials was the single most common way attackers gained their first foothold, appearing in 22% of breaches. A VPN treats a valid credential as a passport to the whole network. ZTNA treats it as one signal among several, and pairs it with device and context checks before granting anything.
Then there is the equipment itself. The same report found that exploiting software vulnerabilities as an initial foothold grew 34% year over year, and the share of that exploitation aimed at edge devices and VPNs jumped from 3% to 22%, close to an eight-fold increase. The very appliances meant to secure remote access have become one of the fastest-growing targets on the internet.
Edge devices and VPNs grew from 3% to 22% of exploited vulnerabilities in one year. Source: Verizon 2025 DBIR.
ZTNA removes that exposure by design. Because applications sit behind a broker and are never published to the internet, there is no public VPN gateway for an attacker to scan for and exploit. Access is invisible until it is verified, which shrinks both the attack surface and the damage a successful login can do. That is the same logic behind reducing what a business exposes in the first place, the goal of attack surface management.
Myth: “We have a VPN, so remote access is handled.” A VPN secures the tunnel, but it still trusts whoever is inside it and still exposes a gateway to the internet. Those are the two weaknesses attackers now lean on hardest: stolen logins that inherit full network access, and unpatched VPN appliances exploited within days of a flaw being disclosed. A VPN encrypts the connection. It does not limit what a compromised user can reach, and that is the gap ZTNA is built to close.
There is a productivity dividend too. Because ZTNA connects users directly to the apps they need, it often feels faster than backhauling all traffic through a central VPN concentrator, and it scales more gracefully as a workforce grows or spreads across locations.
Source: Verizon 2025 Data Breach Investigations Report | Verizon 2025 DBIR newsroom summary
Types of ZTNA
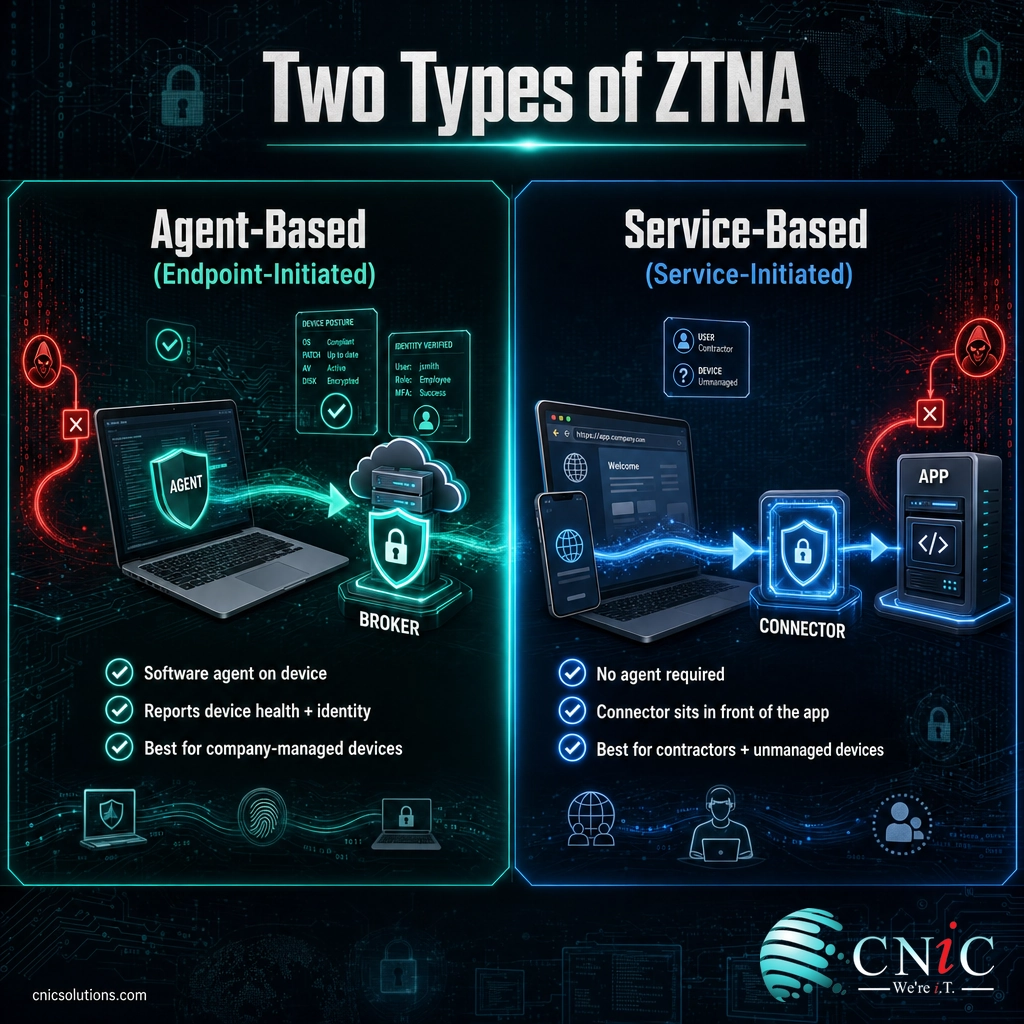
ZTNA is not one single product. It comes in two main architectures, and it can be bought either on its own or as part of a larger platform. Knowing the difference helps you match the model to how your business actually works.
Agent-based (endpoint-initiated) ZTNA
A lightweight software agent runs on each device. It reports the user’s identity and the device’s health (patch status, disk encryption, security tooling) to the broker, which factors all of that into the access decision. This model gives the richest context and the tightest control, which makes it a strong fit for company-managed laptops and phones. The tradeoff is that something has to be installed and maintained on every endpoint.
Service-based (service-initiated) ZTNA
Here a connector sits in front of the applications and reaches out to the broker, so no agent is required on the user’s device. Access happens through the browser or a light client. Because there is nothing to install, this model shines for contractors, partners, and personal or unmanaged devices where you cannot dictate what runs on the endpoint. The tradeoff is less visibility into device posture than the agent-based approach.
On top of that split, ZTNA is delivered in two ways. Standalone ZTNA is a dedicated product you deploy for secure access. ZTNA as part of SASE (Secure Access Service Edge) bundles it with other network and security services in one cloud-delivered platform. Smaller teams often start with standalone ZTNA for a single painful use case, then fold it into a broader platform as their needs grow. Getting that architecture right is exactly the kind of decision a virtual CIO helps businesses make without guesswork.
Source: Gartner glossary, Zero Trust Network Access (ZTNA) | NIST SP 800-207, Zero Trust Architecture
How to Get Started with ZTNA
Moving to ZTNA is a phased project, not a switch you flip. The goal is to shift access off the VPN gradually, starting where the risk is highest, without disrupting the people who need to get work done. A sound rollout usually follows this path:
- Inventory your applications and users. List what people actually need to reach remotely and who needs each thing. ZTNA is built on least privilege, so you cannot write good policies without knowing who should reach what.
- Connect your identity provider. ZTNA leans on strong identity. Tie it into your existing identity system and enforce multifactor authentication so every request starts from a verified user.
- Start with one high-value application. Pick a single sensitive app (a finance system, an admin console) and put it behind ZTNA first. This proves the model and delivers real protection quickly.
- Write least-privilege policies. Grant each group access to only the apps they need, and add device and context conditions. Default to deny and open doors deliberately.
- Expand and retire the VPN. Move applications over in waves, watch the logs, and shrink VPN access as you go until the legacy gateway can be turned off.
None of this requires ripping everything out at once, but it does reward planning and a steady hand on the policies. For many small and midsize businesses, the practical route is to have a security partner design and run ZTNA as part of ongoing managed security services, paired with the around-the-clock monitoring that catches the sign-ins policy alone cannot. ZTNA also works best alongside internal controls like network segmentation, so a single model governs access from every direction.
Source: CISA Zero Trust Maturity Model | NIST SP 800-207, Zero Trust Architecture
Build Your Zero Trust Roadmap With a vCIO
Common Questions About ZTNA
What is ZTNA (Zero Trust Network Access)?
What is the difference between ZTNA and a VPN?
Is ZTNA the same as Zero Trust?
What are the two types of ZTNA?
Does ZTNA replace a VPN?
Related Terms
- Zero Trust: the security model that grants no implicit trust based on network location and verifies every request explicitly. ZTNA is the technology that applies Zero Trust to access.
- VPN (Virtual Private Network): the legacy remote-access approach that authenticates once and extends the network to the user’s device, which is the broad trust ZTNA is designed to replace.
- SASE (Secure Access Service Edge): a cloud-delivered platform that bundles ZTNA with networking and other security services in one place.
- Least privilege: the principle of granting each user only the access they genuinely need. ZTNA enforces it on every application request.
- Conditional access: identity-driven policy that decides what a verified user must prove before access is granted. See how conditional access protects accounts.
- Network segmentation: dividing a network into isolated zones so a breach cannot spread. Learn how VLANs separate business network traffic.
- Managed detection and response (MDR): around-the-clock monitoring that spots and stops threats. See what MDR covers.
- Attack surface management: finding and reducing every exposed way into your systems, including the internet-facing gateways ZTNA removes. See how attack surface management works.
About This Guide
The definition and access model of ZTNA follow the Zero Trust principles set out in NIST Special Publication 800-207 (Zero Trust Architecture) and the CISA Zero Trust Maturity Model, along with Gartner’s definition of Zero Trust Network Access, the analyst firm that coined the term. The forecast that at least 70% of new remote access deployments would use ZTNA rather than VPNs by 2025 (up from under 10% at the end of 2021) is Gartner’s. Breach statistics, including compromised credentials as the leading initial access vector (22% of breaches), the 34% year-over-year rise in vulnerability exploitation, and the growth of edge devices and VPNs from 3% to 22% of exploited vulnerabilities, are drawn from the Verizon 2025 Data Breach Investigations Report. Figures are cited to their original sources and used to explain how ZTNA reduces risk, not as a guarantee of any specific outcome.
Sources: NIST SP 800-207, Zero Trust Architecture | CISA Zero Trust Maturity Model | Gartner glossary, ZTNA | Verizon 2025 DBIR
Get a Free Security Audit From CNiC Solutions
Explore Secure Networking Services


related posts
Zero Trust Statistics for 2026: Adoption, Maturity, and Breach Impact
November 3, 2026Zero trust has become the default security strategy on paper, but not yet in practice. Okta's…
What Is XDR (Extended Detection and Response) and How Does It Protect…
November 2, 2026Extended detection and response (XDR) is a security platform that collects and correlates threat data from…
What Is Zero Trust Security? A Guide for Small Businesses
November 2, 2026Zero Trust security is a cybersecurity model built on one rule: never trust, always verify. Instead…
What Is the Cyber Kill Chain? The 7 Stages Explained
November 1, 2026The cyber kill chain is a model that breaks a cyberattack into seven sequential stages, from…