Attack surface management (ASM) is the continuous process of discovering, inventorying, and monitoring every internet-facing asset an attacker could target, then prioritizing and fixing the exposures that matter most. It gives a business an outside-in view of everything it exposes online, including the assets it forgot it owned.
You cannot protect what you do not know you have. Every cloud account, subdomain, remote laptop, connected device, and third-party tool your business uses adds another possible way in for an attacker, and most companies underestimate how many of those doors they have left open. Attack surface management is the discipline of finding all of them first, from the outside in, then fixing the ones that put you most at risk before someone else finds them.
- ASM is discovery-first. Unlike a scan of assets you already track, ASM begins by finding the assets you did not know existed, then prioritizes and monitors them.
- The problem is exposure, not just bugs. IBM put the average breach at $4.88 million in 2024, and 35% of breaches involved shadow data sitting in sources no one was managing.
- Attackers move faster than defenders patch. Verizon found attackers begin mass-exploiting new vulnerabilities in a median of 5 days, while organizations take about 55 days to fix half of the critical ones.
- ASM is not vulnerability management. Vulnerability management asks what is wrong with a known asset. ASM asks what do we even expose, and answers it continuously.
- It is a program, not a product. Discovery, classification, prioritization, remediation, and monitoring run as an ongoing loop, which is why many businesses run it through a managed security provider.
What’s in This Guide
- What Is an Attack Surface, and What Is ASM?
- How Attack Surface Management Works
- ASM vs Vulnerability Management: The Key Difference
- Why Attack Surface Management Matters for Your Business
- The Types of Attack Surface Management
- How to Get Started with Attack Surface Management
- Common Questions About Attack Surface Management
- Related Terms
What Is an Attack Surface, and What Is ASM?
Before you can understand attack surface management, it helps to define the thing it manages. NIST defines an attack surface as the set of points on the boundary of a system where an attacker can try to enter, cause an effect, or extract data. In plain terms, it is every possible way in. That includes your website and its subdomains, cloud storage buckets, email servers, remote access portals, employee laptops, connected cameras and sensors, exposed databases, and the software supply chain behind all of it.
The trouble is that this surface has exploded in size. A decade ago, a business perimeter was mostly a single office network behind one firewall. Today the same company might run dozens of cloud services, let staff work from home on personal devices, and connect to a web of third-party vendors. Every one of those additions creates new exposure, and much of it gets created faster than anyone documents it. A marketing team spins up a landing page, a developer opens a test server, an acquired company brings its own unpatched systems. These become part of your attack surface whether or not IT knows they exist.
Attack surface management is the answer to that sprawl. It is a continuous, outside-in process that maps everything your organization exposes to the internet the way an attacker would see it, keeps that map current as things change, and drives action to close the exposures that carry the most risk. The critical word is continuous. ASM is not a report you run once. It is an ongoing program of discovery and monitoring, because the surface it watches never stops moving.
Source: NIST Computer Security Resource Center glossary
How Attack Surface Management Works
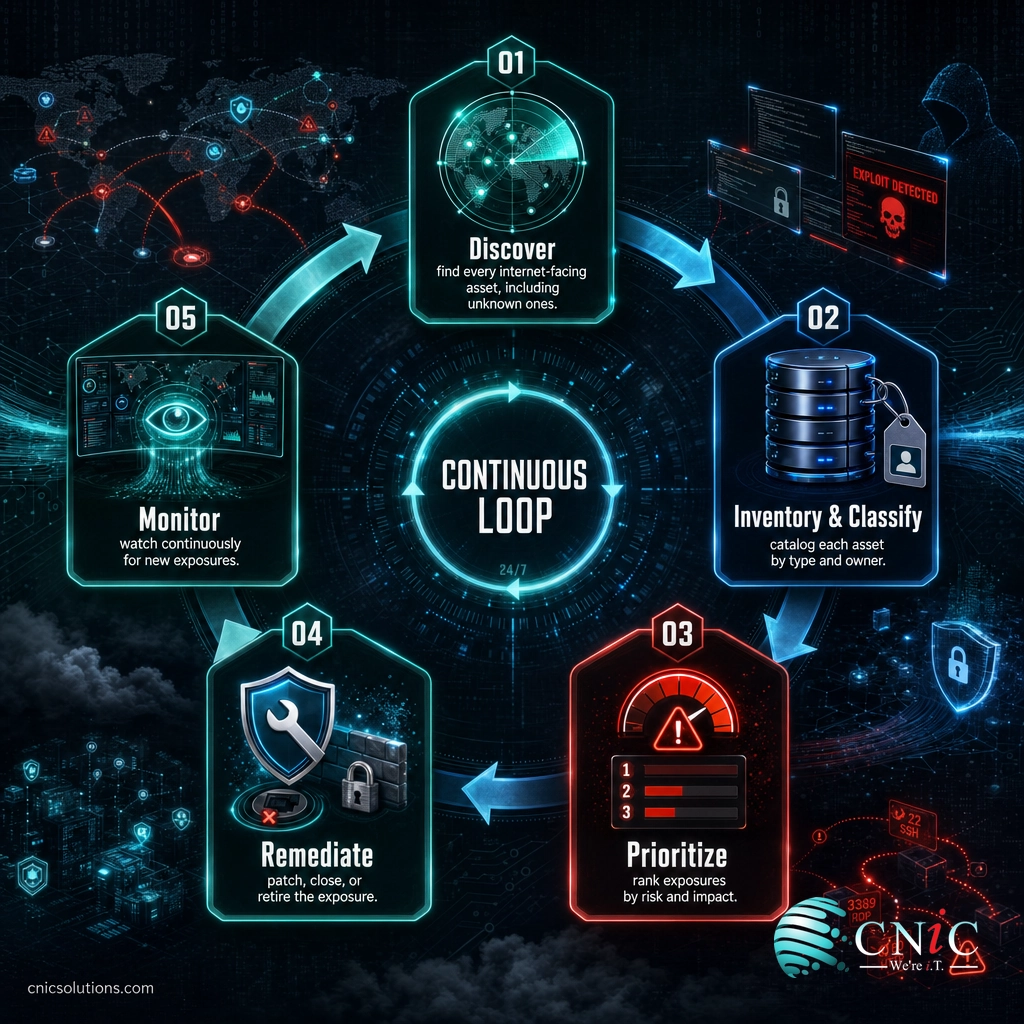
ASM runs as a repeating loop, not a straight line. Each cycle feeds the next, so the picture stays current. Most programs follow five stages.
- Discovery. The tool searches the public internet for anything tied to your organization: domains, subdomains, IP ranges, cloud services, certificates, and exposed applications. The goal is to find assets you never inventoried, including forgotten and rogue ones.
- Inventory and classification. Every discovered asset is cataloged and labeled by type, owner, technology, and business function, so you know what each thing is and who is responsible for it.
- Risk scoring and prioritization. Not every exposure matters equally. Assets are ranked by how exploitable they are and how much damage a compromise would cause, so the most dangerous issues rise to the top.
- Remediation. The high-priority exposures are fixed, whether that means patching, closing a port, retiring a stale asset, or tightening a misconfiguration.
- Continuous monitoring. The cycle repeats around the clock. New assets, new services, and new weaknesses are caught as they appear, not months later during an annual review.
A useful way to picture it: think of your attack surface as every door, window, loading dock, and air vent on a sprawling building complex. Discovery is the security team walking the entire perimeter to map every entry point, including the side door facilities forgot was there. Classification records what each opening leads to. Prioritization decides which unlocked doors to secure first based on what is behind them. Remediation locks them. And monitoring means someone keeps walking the perimeter, because tenants keep cutting new doors into the walls.
The single biggest reason ASM exists is that first stage. A traditional security scan is pointed at a list of assets you hand it. If an asset is not on the list, it is invisible. ASM flips that around: it finds the list first, from the attacker’s vantage point outside your network, which is exactly how a real intruder looks for a way in.
ASM vs Vulnerability Management: The Key Difference
The most common point of confusion is the line between attack surface management and vulnerability management. They are related and often work together, but they answer different questions. Vulnerability management scans assets you already know about and reports the known flaws on them. Attack surface management starts a step earlier, discovering the assets themselves, especially the ones no one is tracking. In short, vulnerability management asks “what is wrong with this asset?” while ASM asks “what do we even expose?” and keeps asking as the surface changes.
| Dimension | Attack Surface Management | Vulnerability Management |
|---|---|---|
| Core question | What do we expose to the internet? | What weaknesses exist on known assets? |
| Starting point | Discovers unknown and unmanaged assets | Works from a known asset inventory |
| Point of view | Outside-in, the attacker’s perspective | Inside-out, the defender’s perspective |
| Scope | Whole exposed footprint, including shadow IT | Assets already enrolled in the scanner |
| Cadence | Continuous discovery and monitoring | Scheduled scans, then reporting |
These two disciplines are strongest together. ASM finds and prioritizes the assets, then vulnerability management does the deep inspection of the ones that matter. Without ASM, your vulnerability scanner is only ever as complete as the list someone remembered to give it, which is why a business can pass every scan and still get breached through a server no one knew was online. If you want to see how quickly those gaps get exploited in practice, our breakdown of how fast attackers weaponize new vulnerabilities shows why the discovery gap is so dangerous.
Why Attack Surface Management Matters for Your Business
Attack surface management is not a niche concern for large enterprises. It has become a baseline need for any organization with an internet presence, and the reason is simple: the money and the timing are both moving in the attacker’s favor.
Start with the cost of getting this wrong. IBM’s Cost of a Data Breach Report 2024 put the global average cost of a data breach at $4.88 million, the highest figure on record and a 10% increase in a single year.
Much of that risk traces directly back to assets no one is watching. The same IBM report found that 35% of breaches involved shadow data, information held in unmanaged or unknown sources, and that those breaches took longer to identify and contain and cost more than average. Shadow data is the attack surface problem in a single statistic: you cannot defend what you never mapped.
Then there is timing. Verizon’s 2024 Data Breach Investigations Report found that the exploitation of vulnerabilities as the initial way into a breach grew by 180% over the prior year, nearly tripling. Worse, the report showed how lopsided the race has become: the median time for attackers to begin mass-exploiting a newly known vulnerability was about 5 days, while organizations took roughly 55 days to remediate half of their critical vulnerabilities.
The Exposure Window: Attacker Speed vs Defender Speed (Verizon 2024 DBIR)
Attackers weaponize new vulnerabilities in a median of 5 days; defenders take about 55 days to remediate half of the critical ones. Source: Verizon 2024 DBIR.
That gap between 5 days and 55 days is the exposure window, and it is exactly the window ASM is designed to shrink. If a vulnerable, internet-facing asset appears and you do not even know it exists, your remediation clock never starts. Continuous discovery closes that blind spot so the countdown begins the moment something new is exposed, not after an attacker finds it for you.
Myth: an annual vulnerability scan or penetration test covers your attack surface. A scheduled scan only checks the assets it was told about, at the moment it runs. It cannot see the cloud instance a team spun up last week, the subdomain pointed at a decommissioned server, or the vendor tool quietly holding your data. Because the surface changes daily, point-in-time testing leaves most of the risk untracked between checks. ASM is continuous by design for exactly this reason.
The connective tissue here is that a growing digital footprint from cloud adoption, remote work, and third-party software is now the norm for businesses of every size, which is precisely why the surface keeps expanding faster than teams can track it. Pairing continuous discovery with active defenses such as endpoint detection and response and managed detection and response turns a sprawling, unknown surface into something a security team can actually see and defend.
Source: IBM Cost of a Data Breach Report 2024 | Verizon 2024 Data Breach Investigations Report
The Types of Attack Surface Management
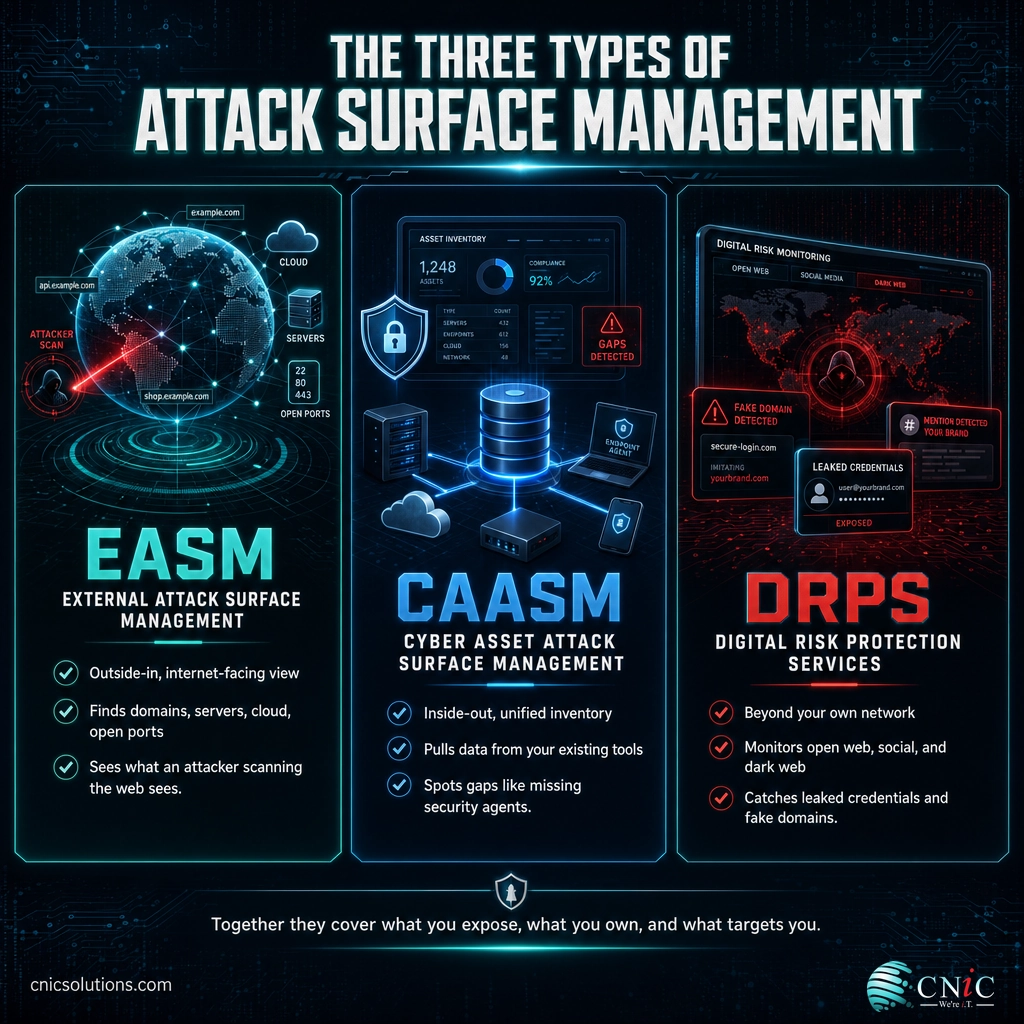
ASM is an umbrella term. The analyst firm Gartner, which shaped much of the modern vocabulary here, breaks it into a few distinct categories, each covering a different slice of your exposure. Understanding the three main ones helps you match a tool or service to what you actually need to protect.
1External Attack Surface Management (EASM)
EASM focuses on everything you expose to the public internet from the outside looking in. It continuously discovers internet-facing assets, such as domains, servers, cloud services, and applications, and flags exposures like open ports, expired certificates, and misconfigurations. This is the category most people mean when they say ASM, because it directly mirrors what an attacker scanning the internet would find.
2Cyber Asset Attack Surface Management (CAASM)
CAASM works from the inside. Instead of scanning the internet, it connects to the tools you already run, such as your endpoint software, cloud consoles, and identity systems, and pulls them into one unified asset inventory. The value is a single, deduplicated view of every asset and the gaps between systems, so you can spot the laptop with no security agent or the server missing from your monitoring. It complements EASM rather than replacing it. One area where an accurate internal inventory pays off immediately is network security monitoring, which depends on knowing what is actually connected.
3Digital Risk Protection Services (DRPS)
DRPS looks beyond your own network entirely. It monitors the open web, social platforms, and the dark web for threats that target your organization from the outside, such as leaked employee credentials, lookalike domains set up for phishing, and stolen data offered for sale. It also extends to third-party and supply chain risk, an area our data on how attacks spread through trusted vendors shows is growing fast.
Newer frameworks pull these threads together under continuous threat exposure management (CTEM), a broader program that combines discovery, prioritization, validation, and mobilization into one ongoing cycle. For most businesses, the practical takeaway is simpler: you need an outside-in view of what you expose, an accurate inside-out inventory of what you own, and awareness of threats aimed at you from beyond your walls.
Source: Gartner information technology glossary
How to Get Started with Attack Surface Management
You do not need an enterprise security budget to bring your attack surface under control. The path is the same regardless of company size, only the scale changes.
- Start with honest discovery. Assume your real footprint is larger than your records show. The first ASM pass almost always surfaces assets, domains, or cloud accounts that no current employee remembers creating.
- Establish a single inventory. Consolidate what discovery finds into one living list, with an owner assigned to each asset. An asset with no owner is an asset no one will patch.
- Prioritize by real risk. Rank exposures by exploitability and business impact rather than trying to fix everything at once. Retire what you do not need, because the safest asset is one you decommission.
- Make it continuous. A one-time cleanup decays quickly. Build monitoring that alerts you when something new appears or an old asset changes.
- Tie it to a broader program. ASM feeds vulnerability management, a formal cybersecurity risk assessment, and your incident response plan. It is the map the rest of your security work relies on.
For most small and midsize businesses, the honest constraint is staffing. Running continuous discovery, triage, and remediation in-house takes people and tooling that most teams do not have to spare. That is why many companies deliver ASM through a managed security services provider (MSSP), which supplies the platform, the monitoring, and the expertise as one service. Whether you build it or buy it, the objective is the same: see your whole attack surface the way an attacker does, and close the gaps before they do.
Get a Free Security Assessment of Your Attack Surface
Explore Managed IT and Security Services
Common Questions About Attack Surface Management
What is attack surface management (ASM)?
What is the difference between attack surface management and vulnerability management?
What are the main types of attack surface management?
Do small businesses need attack surface management?
How often should attack surface management run?
Related Terms
- Attack surface: the full set of points where an attacker could try to enter your systems, cause harm, or extract data, from public websites to employee devices.
- External attack surface management (EASM): the outside-in discipline of finding and monitoring everything your organization exposes to the public internet.
- Cyber asset attack surface management (CAASM): the inside-out practice of unifying data from your existing tools into one accurate asset inventory.
- Vulnerability management: the process of scanning known assets for weaknesses and remediating them, shown in our latest exploited-vulnerability data.
- Shadow IT: the systems, cloud services, and devices used inside a business without the IT team’s knowledge, a leading source of unmanaged attack surface.
- Managed detection and response (MDR): a service that continuously monitors for and responds to threats, explained in our guide to managed detection and response.
- MSSP: a managed security services provider that delivers programs like ASM, monitoring, and response as an outsourced service.
- Continuous threat exposure management (CTEM): a broader framework that combines discovery, prioritization, validation, and remediation into one ongoing cycle.
About This Guide
Breach cost and shadow data figures are drawn from IBM’s Cost of a Data Breach Report 2024. Vulnerability exploitation growth and the attacker-versus-defender timing figures are from Verizon’s 2024 Data Breach Investigations Report. The definition of an attack surface follows the NIST Computer Security Resource Center glossary, and the ASM category framework (EASM, CAASM, DRPS) follows terminology defined by Gartner. Figures are cited to their original sources and used to illustrate the scale and economics of digital exposure, not as guaranteed outcomes for any specific business.
Sources: IBM Cost of a Data Breach Report 2024 | Verizon 2024 DBIR | NIST CSRC glossary | Gartner IT glossary | CISA Known Exploited Vulnerabilities Catalog
Map and Secure Your Attack Surface with CNiC


related posts
What Is a Hypervisor? Types and How They Work
October 7, 2026A hypervisor is software that lets a single physical computer run many separate virtual machines at…
What Is a Load Balancer? How It Keeps Applications Fast and Reliable
October 7, 2026A load balancer is a device or piece of software that sits in front of your…
What Is a Human Firewall? Turning Employees Into Your Best Defense
October 6, 2026A human firewall is the group of employees who, through security awareness and good habits, act…
What Is a Firmware Update and Why It Matters for Security
October 6, 2026A firmware update is a manufacturer-issued revision to the low-level software built into a device, such…