The short answer: SOC 1 is about money, and SOC 2 is about data. A SOC 1 report examines the controls at your company that could affect your customers’ financial statements, while a SOC 2 report examines the controls that protect the security and privacy of the data you handle. Both are independent audit reports from a CPA firm, both come in a Type 1 and a Type 2 version, and neither one outranks the other. Picking the wrong report is not a minor paperwork error either: it can stall an enterprise deal, force a re-audit, or leave a genuine risk unexamined. Here is exactly what separates the two and how to know which one your business needs.
- SOC 1 = financial controls, SOC 2 = data and security controls. SOC 1 covers your effect on customers’ financial reporting; SOC 2 covers how you protect their information.
- The numbers are not tiers. SOC 2 is not a higher or better version of SOC 1. They answer different questions for different readers, and you do not need a SOC 1 before pursuing a SOC 2.
- Both come in Type 1 and Type 2. Type 1 tests whether controls are designed well at a point in time; Type 2 tests whether they operated effectively over a period, typically three to twelve months.
- SOC 2 is built on five Trust Services Criteria. Security is required in every SOC 2; Availability, Processing Integrity, Confidentiality, and Privacy are added based on what your service does.
- Rising breach costs are driving demand. With the global average data breach reaching a record USD 4.88 million in 2024, customers now vet vendors harder than ever, and a SOC report is often the price of entry.
Two reports, two very different jobs. Use this quick split before reading the full breakdown below.
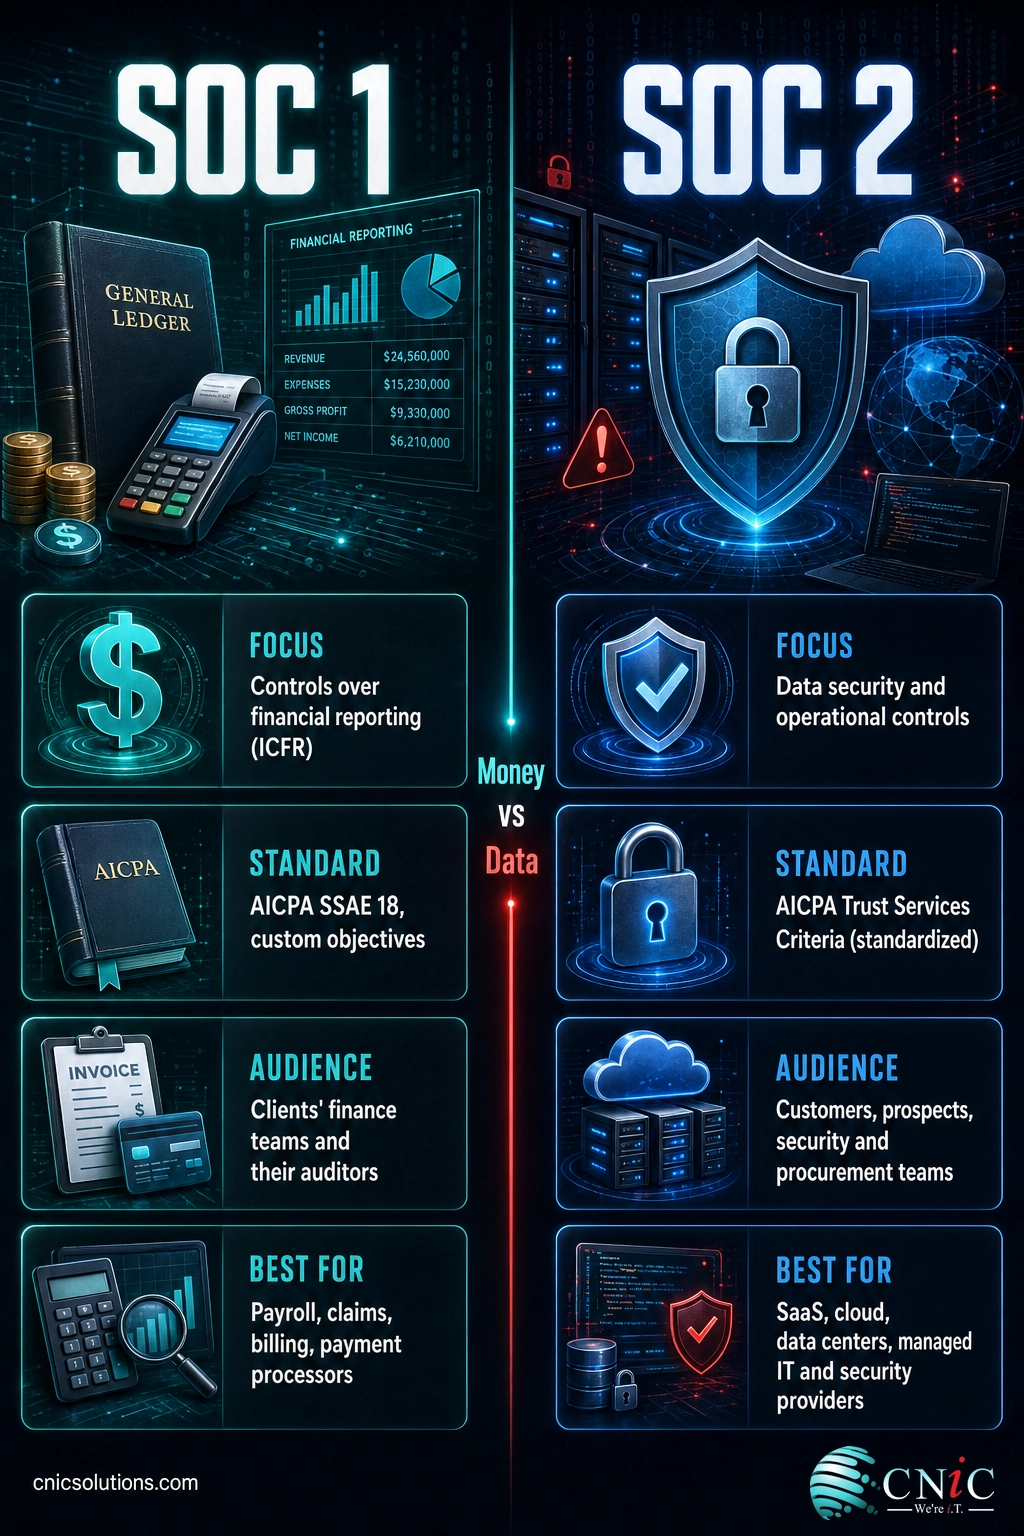
- SOC 1 covers: controls over financial reporting (ICFR) | built on the AICPA’s SSAE 18 standard | control objectives custom to your financial processes | read by clients’ finance teams and their financial-statement auditors | best for payroll, claims, billing, and payment processors.
- SOC 2 covers: data security and operational controls | built on the AICPA’s Trust Services Criteria | a standardized framework every SOC 2 is measured against | read by customers, prospects, and procurement and security teams | best for SaaS, cloud, data centers, and managed IT providers.
What’s in This Guide
- What SOC 1, SOC 2, and SOC 3 Actually Are
- Understanding SOC 1: Financial Reporting Controls
- Understanding SOC 2: Data Security and the Trust Services Criteria
- SOC 1 vs SOC 2: The Core Differences
- Type 1 vs Type 2 (It Applies to Both)
- Why Customers Are Demanding These Reports
- When You Need a SOC 1 Report
- When You Need a SOC 2 Report
- Do You Need Both? And What About SOC 3?
- How to Decide Which Report You Need
- Frequently Asked Questions
What SOC 1, SOC 2, and SOC 3 Actually Are
SOC stands for System and Organization Controls. It is a suite of independent audit reports created and governed by the American Institute of Certified Public Accountants (AICPA). When your company outsources a function to a service provider, that provider’s controls become part of your risk. A SOC report is how an independent CPA firm gives your customers assurance about those controls without every customer having to audit you individually.
There are three reports in the family, and they are often confused:
- SOC 1 reports on controls at a service organization that are relevant to its clients’ internal control over financial reporting. In plain terms: could what you do move a number on your customer’s financial statements?
- SOC 2 reports on controls relevant to data security and privacy, measured against a standardized set of criteria. In plain terms: can customers trust you to protect the systems and information they hand you?
- SOC 3 is a short, general-use summary of a SOC 2. It contains the auditor’s opinion but strips out the detailed control testing, so it can be shared publicly on a website or in marketing.
SOC 1 and SOC 2 are the two most businesses have to choose between, and they are restricted-use reports, meaning they are meant for you, your customers, and their auditors, not the general public. That is where SOC 3 fits: it is the public-facing version. Everything that follows focuses on the SOC 1 versus SOC 2 decision, because that is the fork most companies actually face.
Source: AICPA and CIMA, SOC Suite of Services
Understanding SOC 1: Financial Reporting Controls
A SOC 1 report exists for one reason: some companies, through the service they provide, can directly affect their customers’ financial statements. If you run payroll for other businesses, process their insurance claims, or handle their payment transactions, an error or control failure on your side can flow straight into their books. A SOC 1 report gives those customers, and the auditors who sign off on their financials, assurance that the controls governing those processes are sound.
How it works
SOC 1 is performed under the AICPA’s attestation standard known as SSAE 18, which took effect in 2017 and replaced the older SSAE 16. What makes SOC 1 distinctive is that the control objectives are custom. You define them around your own financial-transaction processes, and the auditor evaluates your controls against those objectives. There is no universal checklist, because a payroll processor and a mortgage servicer control very different risks.
Who it is for
The audience for a SOC 1 report is narrow and specific: your customers’ finance and accounting teams, and above all their external financial-statement auditors. Those auditors often cannot complete their own audit of your customer without understanding the controls at your organization. A SOC 1 report lets them do that. If no one is auditing your customers’ financial statements and your service does not touch financial reporting, you almost certainly do not need a SOC 1.
Genuine strengths and limits
The strength of SOC 1 is precision. Because the objectives are tailored to your financial processes, the report speaks directly to the exact risks that matter to a customer’s books. The limit is that it says very little about cybersecurity, data privacy, or system availability. A clean SOC 1 tells a customer your financial-transaction controls are solid; it does not tell them whether their sensitive data is protected from a breach. For that, you need SOC 2.
Source: AICPA and CIMA, SOC Suite of Services
Understanding SOC 2: Data Security and the Trust Services Criteria
A SOC 2 report answers the question every modern customer asks before handing you their data: can we trust your security? Instead of custom financial objectives, SOC 2 measures your controls against a standardized framework called the Trust Services Criteria, published by the AICPA. That standardization is the point. Because every SOC 2 is evaluated against the same criteria, a customer can compare vendors on a common basis.
The five Trust Services Criteria
SOC 2 is built on five criteria, but they are not all mandatory. Security is required in every SOC 2 report; the other four are included only when they are relevant to the service you provide. This is why two SOC 2 reports can look quite different in scope.
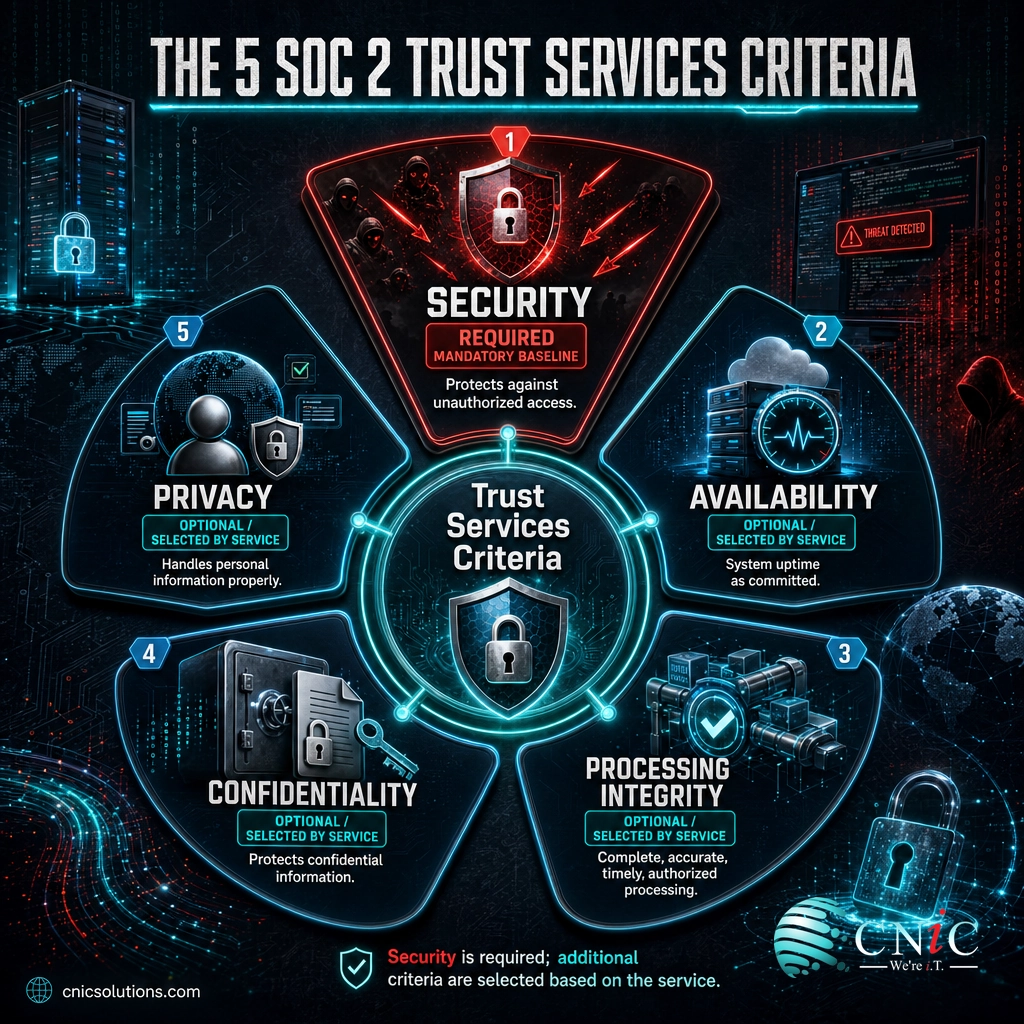
- Security (required): protection of systems and data against unauthorized access, disclosure, and damage. This is the common baseline every SOC 2 must include.
- Availability: whether the system is available for operation and use as committed, relevant when you promise uptime or performance.
- Processing Integrity: whether system processing is complete, valid, accurate, timely, and authorized, relevant for transaction or data-processing services.
- Confidentiality: protection of information designated as confidential, relevant when you handle sensitive business data under agreements.
- Privacy: how personal information is collected, used, retained, and disposed of, relevant when you handle consumer personal data.
Who it is for
SOC 2 has a much broader audience than SOC 1. It is read by your customers, your prospects, and the procurement and security teams that evaluate you before signing. For software companies, cloud providers, data centers, and managed IT and security firms, a SOC 2 report has become a standard requirement in enterprise sales. It is frequently the document a security questionnaire is trying to replace.
Source: AICPA and CIMA, SOC Suite of Services and Trust Services Criteria
SOC 1 vs SOC 2: The Core Differences
With both reports understood on their own, the contrast becomes clear. The difference is not depth or seniority; it is subject matter. SOC 1 looks at financial-reporting risk. SOC 2 looks at data-protection risk. Everything else, the standard behind it, the audience, and how the objectives are set, follows from that split.
| Attribute | SOC 1 | SOC 2 |
|---|---|---|
| Primary focus | Controls over financial reporting (ICFR) | Data security and operational controls |
| Core question | Could you affect our financial statements? | Can we trust you to protect our data? |
| Framework | Custom control objectives (SSAE 18) | Standardized Trust Services Criteria |
| What is measured | Objectives you define around financial processes | The same five criteria applied to your service |
| Primary audience | Clients’ finance teams and their auditors | Customers, prospects, procurement, security teams |
| Best fit | Payroll, claims, billing, payment processors | SaaS, cloud, data centers, MSPs and MSSPs |
| Report use | Restricted-use | Restricted-use (SOC 3 for public sharing) |
| Type 1 and Type 2 | Both available | Both available |
Myth: SOC 2 is the “higher” or “better” report. This is the single most common misunderstanding. The 1 and 2 are not levels, grades, or a sequence you climb. You do not need a SOC 1 before you can get a SOC 2. A company that only affects data needs a SOC 2 and would gain nothing from a SOC 1, while a payroll bureau that touches clients’ books may need a SOC 1 regardless of how strong its cybersecurity is. Choose by subject matter, not by number.
Type 1 vs Type 2 (It Applies to Both)
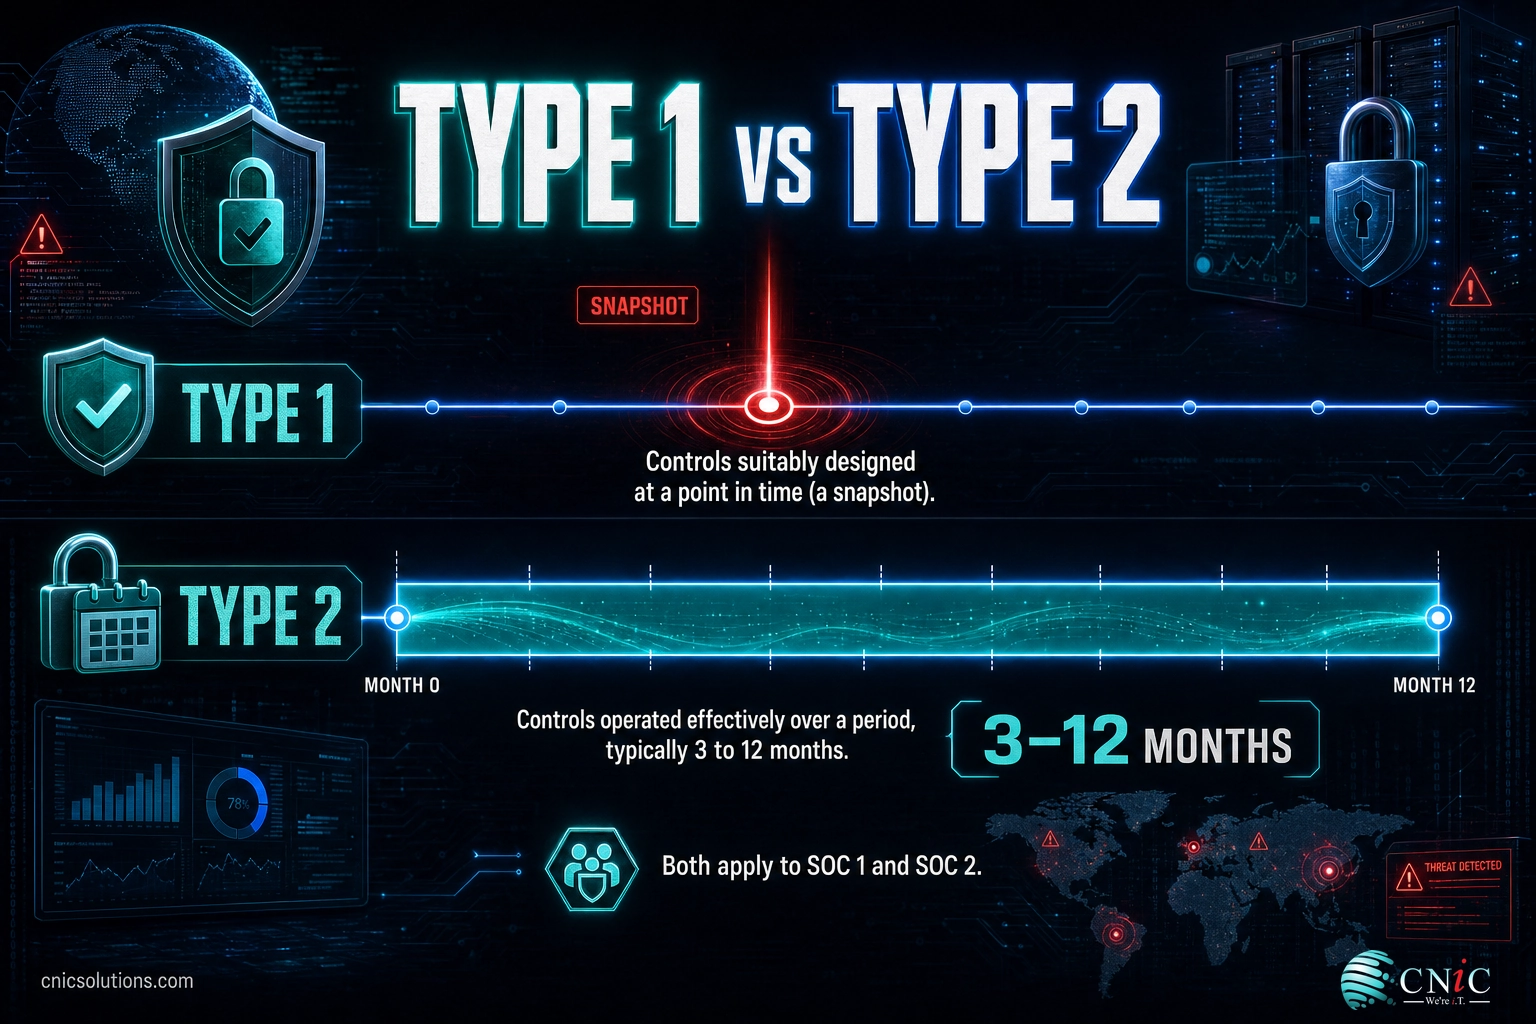
Here is a distinction that trips people up: Type 1 and Type 2 are not a third and fourth report. They are variations that apply to both SOC 1 and SOC 2. So you might get a SOC 1 Type 2, or a SOC 2 Type 1, and so on. The difference is about time.
- Type 1 evaluates whether your controls are suitably designed at a single point in time, essentially a snapshot on a specific date. It confirms the right controls exist and are set up correctly.
- Type 2 goes further and tests whether those controls actually operated effectively across a period, typically three to twelve months. It confirms the controls did not just exist on paper but worked in practice, day after day.
Type 2 carries far more weight with customers because operating effectiveness over time is much harder to fake than a well-designed control on one good day. Many organizations begin with a Type 1 to establish a baseline quickly, then move to a Type 2 to cover the following observation period. A Type 1 is a reasonable first step, but for most enterprise buyers, the Type 2 is what they ultimately want to see.
Source: AICPA and CIMA, SOC Suite of Services
Why Customers Are Demanding These Reports
A decade ago, SOC reports were a niche concern for banks and their vendors. Today they are routine in enterprise procurement across nearly every industry, and the reason is straightforward: the cost of a third-party failure has climbed sharply. When a vendor is breached, the customer pays too, in downtime, notification costs, regulatory fines, and lost trust.
The trend is easiest to see in the price of a breach. According to IBM’s Cost of a Data Breach research, produced with the Ponemon Institute, the global average cost of a data breach has risen every year and reached a record high in 2024.
Global Average Cost of a Data Breach, 2021 to 2024 (IBM / Ponemon)
Global average total cost of a data breach. The 2024 figure was a record high, up about 10% year over year. Source: IBM Cost of a Data Breach Report 2024.
With numbers like these, enterprises can no longer take a vendor’s security on faith. A SOC 2 report is how a buyer transfers that risk question to an independent auditor, and a SOC 1 does the same for financial-reporting risk. Increasingly, no report means no deal. That is why a growing number of small and midsize providers pursue a SOC 2 not because a regulator requires it, but because their biggest prospects do. Understanding where these reports fit alongside frameworks like HIPAA, PCI DSS, and CMMC is part of building a complete IT compliance program for a small or midsize business.
Source: IBM Cost of a Data Breach Report 2024
When You Need a SOC 1 Report
You most likely need a SOC 1 report if your service can influence your customers’ financial statements. The test is not whether you handle money in general; it is whether a control failure at your organization could produce an error in someone else’s financial reporting. Consider a SOC 1 if your business fits one of these profiles:
- You process financial transactions for clients: payment processors, billing platforms, and lockbox services whose accuracy flows into client ledgers.
- You run payroll or benefits administration: a mistake in your processing shows up directly in your clients’ books and filings.
- You handle insurance claims or loan servicing: the amounts you calculate and disburse feed customers’ financial statements.
- Your customers’ auditors ask for it: the clearest signal of all. If financial-statement auditors are requesting assurance about your controls, that is a SOC 1 request.
- You are a fund administrator or trust service: your records and reconciliations become inputs to your clients’ reported financial position.
If none of these describe you, and your service is really about storing, processing, or protecting data rather than affecting the books, a SOC 1 is probably the wrong report and a SOC 2 is the one to pursue.
When You Need a SOC 2 Report
You most likely need a SOC 2 report if customers trust you with their data or rely on your systems to stay secure and available. This covers a much larger share of modern businesses than SOC 1 does. Consider a SOC 2 if your business fits one of these profiles:
- You are a SaaS or software company: customers store their data in your product and expect proof it is protected.
- You provide cloud hosting or data center services: availability and security of the underlying infrastructure are your customers’ risk too.
- You are a managed IT or managed security provider: clients hand you privileged access to their environment, so your controls directly shape their exposure. This is exactly why a rigorous cybersecurity risk assessment underpins any credible SOC 2 program.
- You handle sensitive or regulated data: health, financial, or personal information that customers are obligated to protect.
- Enterprise prospects send you security questionnaires: a SOC 2 report often satisfies those questionnaires in one document and shortens the sales cycle.
For most technology and IT service businesses, SOC 2 is the report that opens doors. It is the credential enterprise buyers look for, and the absence of one is increasingly a reason deals stall. If you are weighing whether to build that program internally or lean on outside expertise, a virtual CISO can lead the security strategy behind a SOC 2 without the cost of a full-time executive hire.
Get Managed IT That Supports Your Compliance Program
Do You Need Both? And What About SOC 3?
Some companies genuinely need both reports, and that is not a sign of overkill. A payroll platform is the classic example: it affects clients’ financial statements, which points to a SOC 1, and it stores sensitive employee and payment data, which points to a SOC 2. The two reports overlap on general IT controls like access management and change control, but each also covers ground the other does not. If your service sits in both worlds, maintaining both reports is the honest answer to two different customer questions.
SOC 3 deserves a brief word too. It is essentially a public-friendly summary of a SOC 2. Because a SOC 2 is restricted-use and detailed, you cannot just post it on your website. A SOC 3 gives you a shareable version with the auditor’s opinion but without the sensitive control details, which makes it useful as a marketing and trust signal. You earn a SOC 3 on the back of a SOC 2 engagement; it is not a separate path.
A simple way to combine them: if you affect the books and hold the data, plan for a SOC 1 and a SOC 2. If you only hold the data, a SOC 2 (optionally paired with a SOC 3 for public sharing) is the fit. If you only affect the books and touch no sensitive data, SOC 1 alone may be enough. The reports are complementary, not competing.
How to Decide Which Report You Need
Cut through the acronyms with three questions about what your service actually does for customers:
- Could a control failure at your company change a number on your customer’s financial statements? If yes, you are in SOC 1 territory.
- Do customers rely on you to keep their data secure, available, or private? If yes, you are in SOC 2 territory.
- Did the request come from a financial-statement auditor or from a security and procurement team? Auditors asking points to SOC 1; security teams and enterprise buyers asking points to SOC 2.
Once you know which report, the harder work is the controls behind it. A report is only as valuable as the security and governance it attests to, and readiness, closing gaps before the audit window opens, is where most of the effort lives. Many small and midsize businesses do not have the internal security leadership to run that program alone, which is where an experienced IT and security partner earns its keep. CNiC Solutions helps regulated and growth-stage businesses across Texas and nationally build the security, monitoring, and governance controls that stand up to a SOC 2 or SOC 1 examination, and supports HIPAA, PCI DSS, and SOC 2 requirements as part of a single managed program.
Get a Free Security and Compliance Consultation
Talk to a Virtual CIO About Your Compliance Roadmap
Frequently Asked Questions
Is SOC 2 better than SOC 1?
Can a company have both a SOC 1 and a SOC 2 report?
What is the difference between SOC 2 Type 1 and Type 2?
How long does it take to get a SOC 2 report?
Who can perform a SOC audit?
Do I still need a SOC 2 report if I already comply with HIPAA or PCI DSS?
About This Guide
Definitions of SOC 1, SOC 2, and SOC 3, the Trust Services Criteria, the SSAE 18 attestation standard, and the distinction between Type 1 and Type 2 reports are drawn from the AICPA and CIMA, which create and govern the SOC framework. Data breach cost figures are from the IBM Cost of a Data Breach Report, produced with the Ponemon Institute. Figures are cited to their original sources and used to explain how these reports work and why customers request them, not as legal advice or a guarantee of any specific audit outcome. Confirm your reporting obligations with a licensed CPA firm.
Sources: AICPA and CIMA, SOC Suite of Services | IBM Cost of a Data Breach Report 2024


related posts
OKRs vs. KPIs: What’s the Difference?
September 22, 2026An OKR (Objective and Key Results) is a goal-setting framework that pairs an ambitious objective with…
Password Statistics for 2026: Reuse, Cracks, and the Passkey Shift
September 22, 2026Weak and stolen passwords are still the number one way attackers get in. In 2025, stolen…
15 Microsoft Teams Tips and Tricks to Boost Team Productivity
September 21, 2026Microsoft Teams is where most of the workday now happens: it passed 320 million monthly active…
Mobile Security Software for Business: A Buyer’s Guide
September 21, 2026Choosing mobile security software for business comes down to two decisions: how you will manage the…