A security operations center (SOC) is a centralized team and facility that monitors an organization’s IT environment around the clock to prevent, detect, investigate, and respond to cyber threats. It combines skilled analysts, defined processes, and security technology into one coordinated defense, so attacks are caught and contained early rather than discovered months later.
Every business now runs on systems that never sleep, and neither do the people trying to break into them. A firewall and antivirus can block the obvious attacks, but they cannot tell you when a determined intruder slips past at 2 a.m. on a holiday weekend, and they certainly cannot stop that intruder on their own. That job belongs to a security operations center: the team, the process, and the technology that watches your environment every hour of every day and acts the moment something is wrong. This guide explains exactly what a SOC is, how one works step by step, who staffs it, how it differs from the terms it gets confused with (the NOC and the unrelated SOC 2 report), why it matters for a business your size, and the three practical ways to get SOC-level protection without necessarily building one yourself.
Key Takeaways
- A SOC is people, process, and technology working as one. It is not a single product you install; it is a coordinated function that monitors, detects, investigates, and responds to threats continuously.
- Its whole purpose is speed. A SOC exists to shrink the window between an attacker getting in and getting caught, which is the single biggest driver of how much a breach ends up costing.
- A SOC is not a NOC, and it is not SOC 2. A NOC fights downtime, a SOC fights attackers, and SOC 2 is an unrelated compliance audit that happens to share the acronym.
- Most businesses rent a SOC rather than build one. With a global shortfall of roughly 4.8 million cybersecurity professionals, staffing a 24/7 team in-house is out of reach for the vast majority of small and midsize companies.
- The stakes are concrete. The average U.S. data breach hit a record $10.22 million in 2025, and organizations still took an average of 241 days to identify and contain one. A SOC is built to close that gap.
What’s in This Guide
What a Security Operations Center Is
A security operations center is the command center for an organization’s cybersecurity. Think of it as the difference between having smoke detectors and having a staffed fire station. Preventive tools are the smoke detectors: useful, essential, but passive. A SOC is the fire station, with trained crews watching for the first sign of trouble and rolling out to put it out before it spreads. Its mission is to detect, analyze, and respond to security incidents in real time, and to keep doing so at every hour, because attacks do not keep business hours.
What makes a SOC a SOC is the combination of three ingredients working together, often summarized as people, process, and technology. The people are security analysts who investigate and decide. The process is the documented playbooks that turn a suspicious signal into a fast, consistent response. The technology is the stack of monitoring and detection tools that feed the analysts a picture of everything happening across the environment. Remove any one of the three and it stops being a SOC: tools with no one watching them are just noise, and analysts with no process are slow and inconsistent when minutes matter.
The scope is deliberately broad. A mature SOC watches identities, endpoints (laptops, servers, and phones), networks, cloud platforms, applications, and databases as one connected whole, because a modern attack rarely stays in one place. This grounding in continuous monitoring and coordinated response maps directly onto the detect-and-respond functions of the NIST Cybersecurity Framework, the standard reference for how organizations are expected to manage cyber risk. A SOC is how that framework becomes a living, staffed reality rather than a document on a shelf.
How a SOC Works, Step by Step
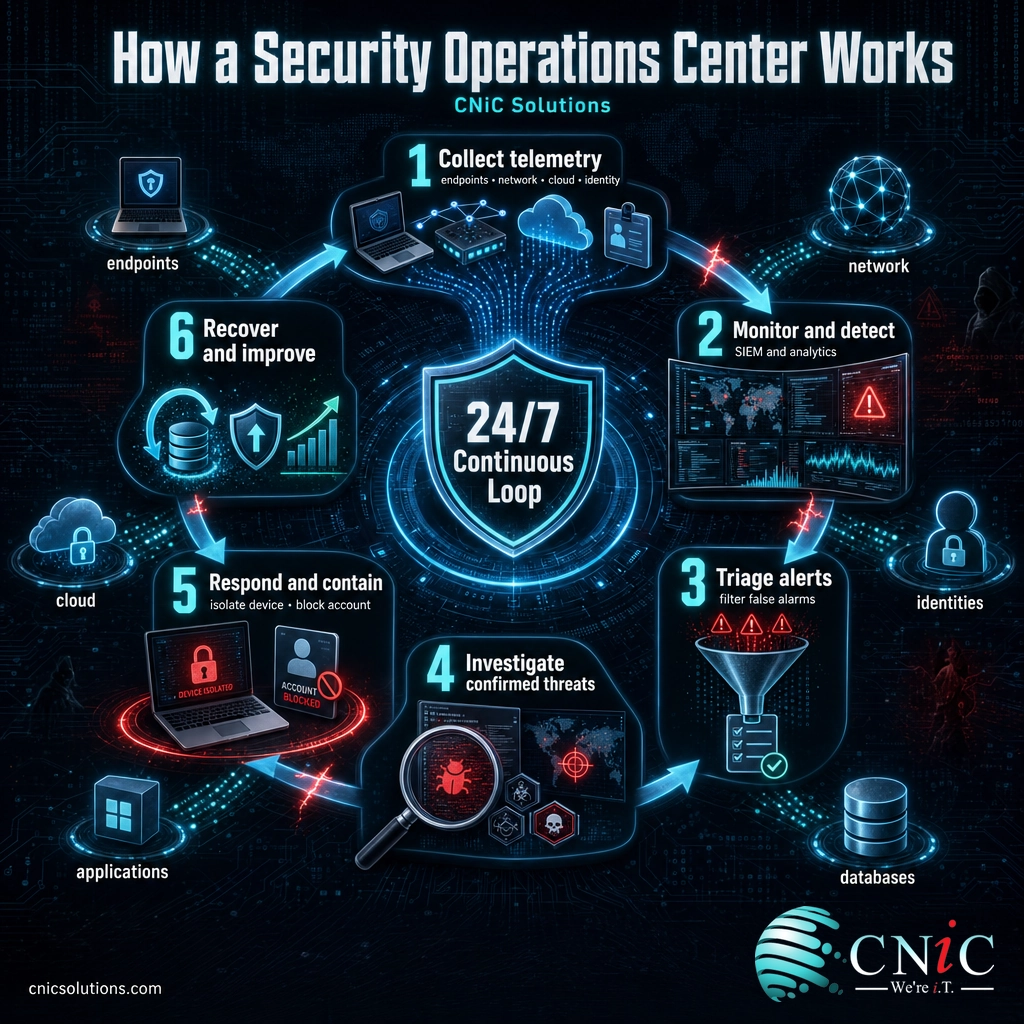
The tools vary from one SOC to the next, but the operating rhythm is remarkably consistent. A working SOC runs the same continuous loop, around the clock, for everything it protects:
- Collect telemetry from everywhere. Sensors and log feeds gather activity from endpoints, the network, cloud services, and identity systems into one place. You cannot defend what you cannot see, so broad visibility is the foundation everything else stands on.
- Monitor and detect continuously. A security information and event management (SIEM) platform and supporting analytics correlate that flood of data, applying detection rules, behavioral models, and current threat intelligence to flag anything abnormal, from an impossible login location to a process behaving like ransomware.
- Triage the alerts. This is where human judgment starts to matter. Analysts sort the genuine threats from the enormous volume of false alarms, so effort goes to what is real instead of drowning in noise.
- Investigate confirmed threats. For anything that looks real, analysts dig in to understand the full story: how the attacker got in, what they touched, which accounts or machines are involved, and how far it has spread.
- Respond and contain. The SOC acts to stop the attack: isolating an infected device from the network, killing a malicious process, or disabling a compromised account before the damage widens. The speed of this step is what limits the blast radius.
- Recover and improve. After the immediate threat is contained, the SOC guides recovery, documents what happened, and tightens defenses so the same weakness cannot be used again. Every incident makes the next detection sharper.
Notice how much of that loop turns on judgment rather than software. Collection and detection can be automated, and increasingly are. But triage, investigation, and the decision to pull a critical server offline in the middle of a workday are human calls made under pressure. That is the real product of a SOC: not a dashboard that tells you something is wrong, but a team that decides what to do and does it.
Who Works in a SOC: The Team Behind the Screens
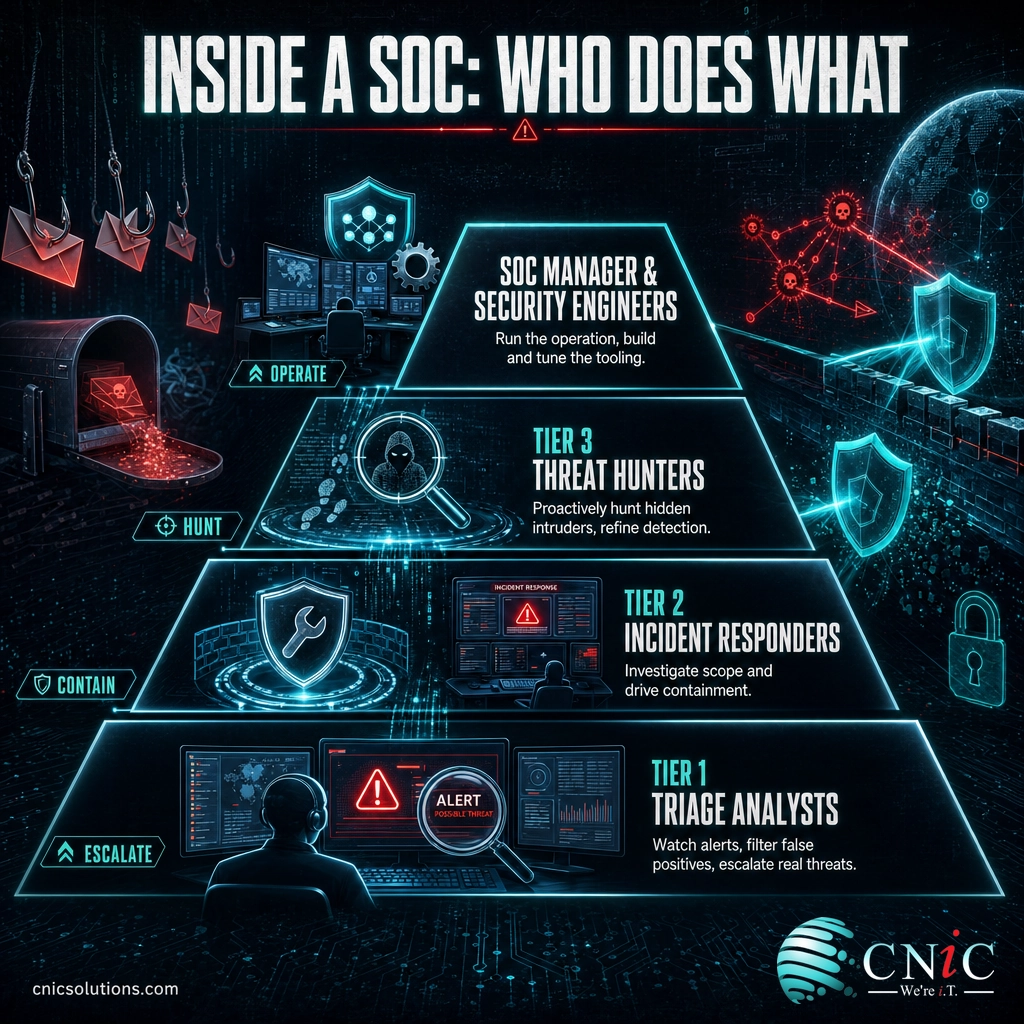
A SOC is only as good as the people running it, and they are usually organized into tiers so that routine alerts and genuine crises are handled by the right level of expertise. Understanding the roles makes it clear why a real SOC is hard to replicate with software alone.
- Tier 1, triage analysts. The front line. They watch incoming alerts, weed out the false positives, and escalate anything that looks like a real threat. Their job is to make sure nothing important gets lost in the noise.
- Tier 2, incident responders. When an alert is confirmed, Tier 2 investigates the full scope and drives the containment: what is affected, how bad it is, and what needs to be shut down now.
- Tier 3, threat hunters. The most experienced analysts, who do not wait for alerts at all. They proactively search the environment for intruders that have slipped past automated detection, and they refine the SOC’s detection rules.
- SOC manager and security engineers. The manager runs the operation, sets priorities, and owns communication during a serious incident. Engineers build and tune the tooling that makes everyone else effective.
That structure is exactly why round-the-clock, in-house SOC staffing is out of reach for most businesses: covering nights, weekends, and holidays with skilled analysts at every tier means hiring and retaining a sizable team in a field where talent is scarce and expensive. It is also why the fastest-growing way to get a SOC is to share one, an idea we come back to below.
SOC vs. NOC vs. SOC 2: Clearing Up the Confusion
Two things get confused with a security operations center constantly, and untangling them makes the SOC’s job much clearer. The first is the NOC. The second is SOC 2, which shares the letters but has nothing to do with a security team at all.
The NOC (network operations center) is the SOC’s operational sibling. Both are staffed monitoring teams, but they watch for opposite problems. A NOC exists to keep systems available and performing well: uptime, network capacity, outages, and slowdowns. A SOC exists to keep systems secure: detecting and stopping malicious activity. In short, a NOC fights downtime while a SOC fights attackers. Many organizations run both, and the two work closely, but their goals, tools, and instincts differ.
| SOC (Security Operations Center) | NOC (Network Operations Center) | |
|---|---|---|
| Primary goal | Protect against cyber threats | Keep systems available and performing |
| Watches for | Attacks, intrusions, suspicious behavior | Outages, latency, capacity, hardware faults |
| The enemy | Human attackers and malware | Downtime and performance issues |
| Typical action | Isolate a device, block an account, contain a breach | Reroute traffic, restart a service, dispatch a fix |
| Success looks like | Threats caught and contained fast | High uptime and smooth performance |
Myth: “SOC” and “SOC 2” are the same thing. They are not, and mixing them up leads to real confusion in vendor conversations. A security operations center is a live team monitoring and defending your systems right now. SOC 2 is a completely separate framework: an audit report, based on standards from the AICPA, that attests how a service provider handles customer data. One is an active defense; the other is a document a company earns to prove its controls. If you are weighing audit reports rather than monitoring, see our breakdown of the difference between SOC 1 and SOC 2 reports, which covers that side of the acronym in full.
Why a SOC Matters for Your Business
The argument for a SOC is not abstract, and it is not about fear. It comes down to three hard realities: breaches are expensive, they hide for a long time before anyone notices, and almost no small or midsize business can staff the continuous detection needed to catch them faster. The numbers below tell that story plainly.
Those figures reinforce one another. A breach is enormously costly, it stays hidden for the better part of a year on average, and the talent needed to find it faster is scarce. A SOC attacks the middle number directly. When someone is watching continuously, the gap between compromise and detection collapses from months to hours, and because cost climbs the longer an intruder lingers, cutting that time is the most direct way to cut what a breach costs you.
The pressure falls hardest on smaller organizations, which attackers single out precisely because they expect thinner defenses. In 2025, ransomware was involved in the overwhelming majority of small-business breaches, at roughly double the rate seen across organizations of every size.
Share of Breaches Involving Ransomware, 2025: Small Business vs. All Organizations
Source: Verizon 2025 Data Breach Investigations Report. Ransomware appeared in 88% of small-business breaches, roughly twice the 44% rate across all organizations.
For a smaller business the case is a single sentence: you are more likely to be hit, less able to absorb the cost, and least equipped to catch the intrusion on your own. A SOC, in one form or another, is how you get the detection-and-response muscle of a large enterprise without the enterprise headcount, working alongside a tested data backup and recovery program so that if an attacker does get through, you can both stop the spread and restore what they touched.
Sources: IBM Cost of a Data Breach Report 2025 | Verizon 2025 Data Breach Investigations Report | ISC2 2024 Cybersecurity Workforce Study
Three Ways to Run a SOC
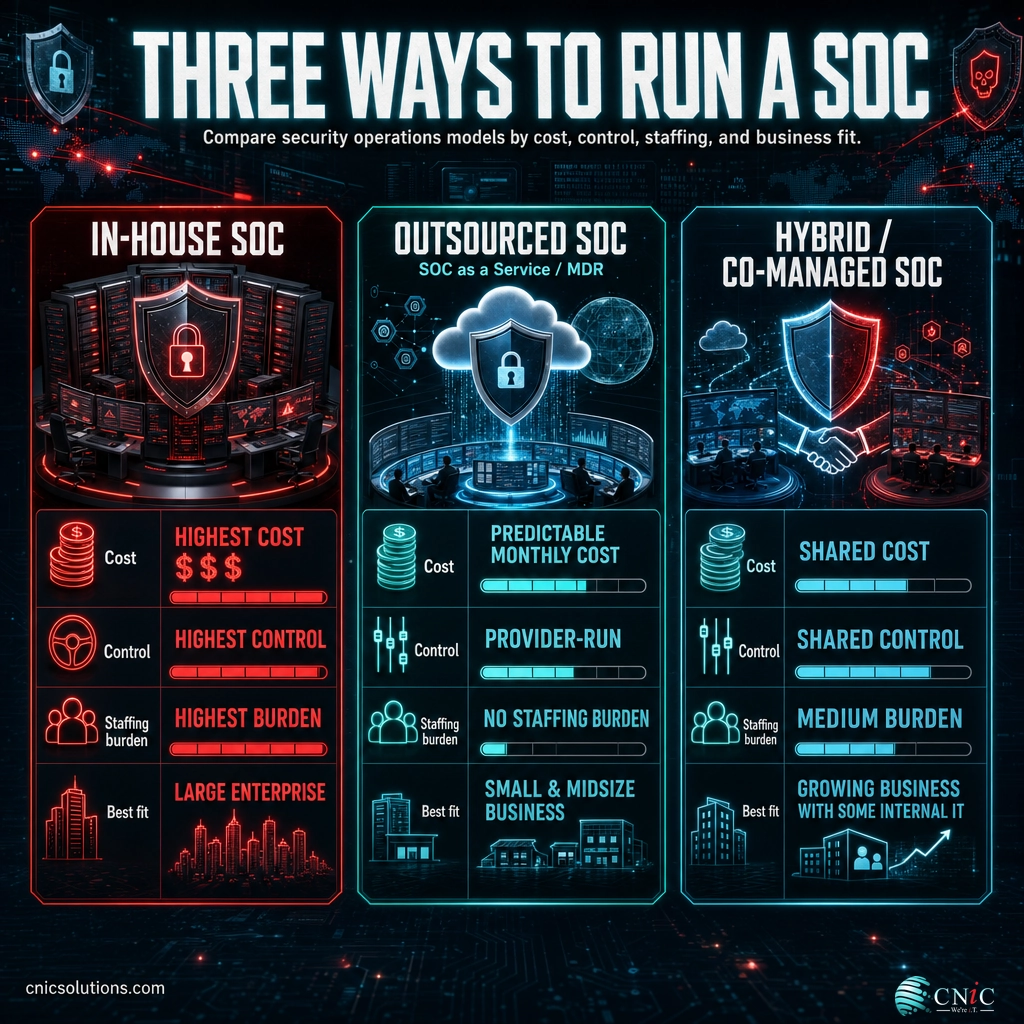
Having a SOC does not have to mean building one from scratch. In practice, there are three models, and the right one depends on your size, your budget, and how much security work you want to own yourself.
- In-house SOC. You hire, train, and run your own security team and tooling. This gives you maximum control and deep knowledge of your environment, but it is the most expensive path by a wide margin, and staffing all three analyst tiers around the clock is realistic only for larger enterprises.
- Outsourced SOC (SOC as a service). A specialist provider delivers the people, process, and technology as a monthly service. This is where managed detection and response (MDR) lives: in effect, a SOC delivered as a service, giving you 24/7 detection and active response without hiring a single analyst. It is the most common answer for small and midsize businesses.
- Hybrid or co-managed SOC. Your internal IT staff handles the daytime and the routine, and an outside provider supplies the after-hours coverage, the specialist skills, and the surge capacity during an incident. You keep control where it matters and rent expertise where it is scarce.
The outsourced and hybrid models exist for one reason: they solve the staffing math that stops most businesses from ever standing up a SOC of their own. Rather than carrying a full security team on the payroll, you share a mature one that already runs day and night. That is also why a SOC rarely comes as a standalone purchase for smaller firms. Detection and response are far more effective when the same partner also keeps your systems patched, configured, and backed up, which is how a broader managed security service typically wraps SOC capability into day-to-day IT.
Does Your Business Need a SOC?
Almost every business today needs SOC-level protection. The honest question is not whether you need continuous detection and response, because the breach numbers settle that, but whether you should build that capability or rent it. For the overwhelming majority of small and midsize companies, the answer is to rent it through an outsourced or co-managed model. A few questions cut straight to whether it is time to act:
- Could you detect an intruder outside business hours? If a compromise at midnight would sit unnoticed until morning, you have exactly the gap a SOC closes.
- Do you hold data attackers want? Customer records, payment details, health or financial information, or access to clients’ systems all raise the stakes and the target on your back.
- Do you face compliance obligations? Regulated industries increasingly expect continuous monitoring and documented incident response, both core SOC functions.
- Could you survive 241 days of undetected access? If that thought is alarming, the value of shrinking the detection window is already clear.
The practical first step is not to buy a SOC, but to understand your exposure. A short cybersecurity risk assessment shows where your real weaknesses are, so any monitoring you put in place is pointed at genuine risks rather than switched on blind. From there, most businesses fold SOC-level detection and response into a managed relationship, so the same partner that watches for threats also keeps the rest of your environment healthy. That is how CNiC Solutions approaches it: our cybersecurity services deliver continuous monitoring, expert investigation, and rapid response, folded into the day-to-day managed IT services that keep everything else running.
Get a free security assessment for your business
Frequently Asked Questions
What is a SOC (security operations center)?
What is the difference between a SOC and a NOC?
Is a SOC the same as SOC 2?
Does a small business need its own SOC?
How much does a SOC cost?
Related Terms
- MDR (managed detection and response): a SOC delivered as a service, pairing detection technology with 24/7 analysts who respond on your behalf. See our full guide to how managed detection and response works.
- SIEM (security information and event management): the platform that aggregates and correlates log data across the environment, feeding the alerts a SOC investigates.
- SOAR (security orchestration, automation, and response): tooling that automates repetitive response steps so SOC analysts can act faster.
- NOC (network operations center): the SOC’s operational sibling, focused on uptime and performance rather than security.
- EDR (endpoint detection and response): a primary sensor a SOC relies on; see our roundup of EDR solutions built for smaller businesses.
- MSSP (managed security services provider): a provider that manages your security tools; strong ones layer managed security services and SOC capability together.
- Network security monitoring: the continuous watching of network traffic for signs of intrusion, a core SOC activity explained in our guide to network security monitoring.
- vCISO (virtual chief information security officer): outsourced security leadership that sets strategy and can direct how a SOC is used. See what a virtual CISO does.
- Dwell time: how long an attacker stays undetected in an environment. Cutting it is the core reason a SOC exists.
About This Guide and Its Sources
This explainer describes a security operations center as the term is used across the cybersecurity industry and grounded in the continuous monitoring and detect-and-respond functions of the NIST Cybersecurity Framework. All statistics come from named primary sources: breach-cost and breach-lifecycle figures are from the IBM Cost of a Data Breach Report 2025; ransomware and small-business breach figures are from the Verizon 2025 Data Breach Investigations Report; and the cybersecurity workforce shortfall is from the ISC2 2024 Cybersecurity Workforce Study. SOC costs vary widely by model, provider, and organization size, and are described qualitatively rather than with a single estimate.


related posts
What Is ZTNA (Zero Trust Network Access)?
November 3, 2026Zero Trust Network Access (ZTNA) is a security service that grants a verified user access to…
Zero Trust Statistics for 2026: Adoption, Maturity, and Breach Impact
November 3, 2026Zero trust has become the default security strategy on paper, but not yet in practice. Okta's…
What Is XDR (Extended Detection and Response) and How Does It Protect…
November 2, 2026Extended detection and response (XDR) is a security platform that collects and correlates threat data from…
What Is Zero Trust Security? A Guide for Small Businesses
November 2, 2026Zero Trust security is a cybersecurity model built on one rule: never trust, always verify. Instead…