ISO 27001 is the world’s best-known standard for managing information security, and increasingly the certification customers expect their vendors to hold before trusting them with sensitive data. Published by the International Organization for Standardization, it defines how to build an information security management system: the framework of policies, people, and technical controls that keeps information safe. This guide explains, in plain terms, what ISO 27001 is, how the standard is structured, what its 93 controls cover, how it differs from SOC 2, what changed in the 2022 revision, and the practical path a business follows to earn and keep the certification.
ISO 27001 is the leading international standard for information security. It sets the requirements for an information security management system (ISMS): a documented, risk-based framework of policies, processes, and controls that protects the confidentiality, integrity, and availability of an organization’s information. Certification by an accredited body proves those safeguards are real, not just promised.
Key Takeaways
- ISO 27001 certifies a system, not a product. It is about how you manage information security continuously, through an ISMS, rather than any single tool you buy.
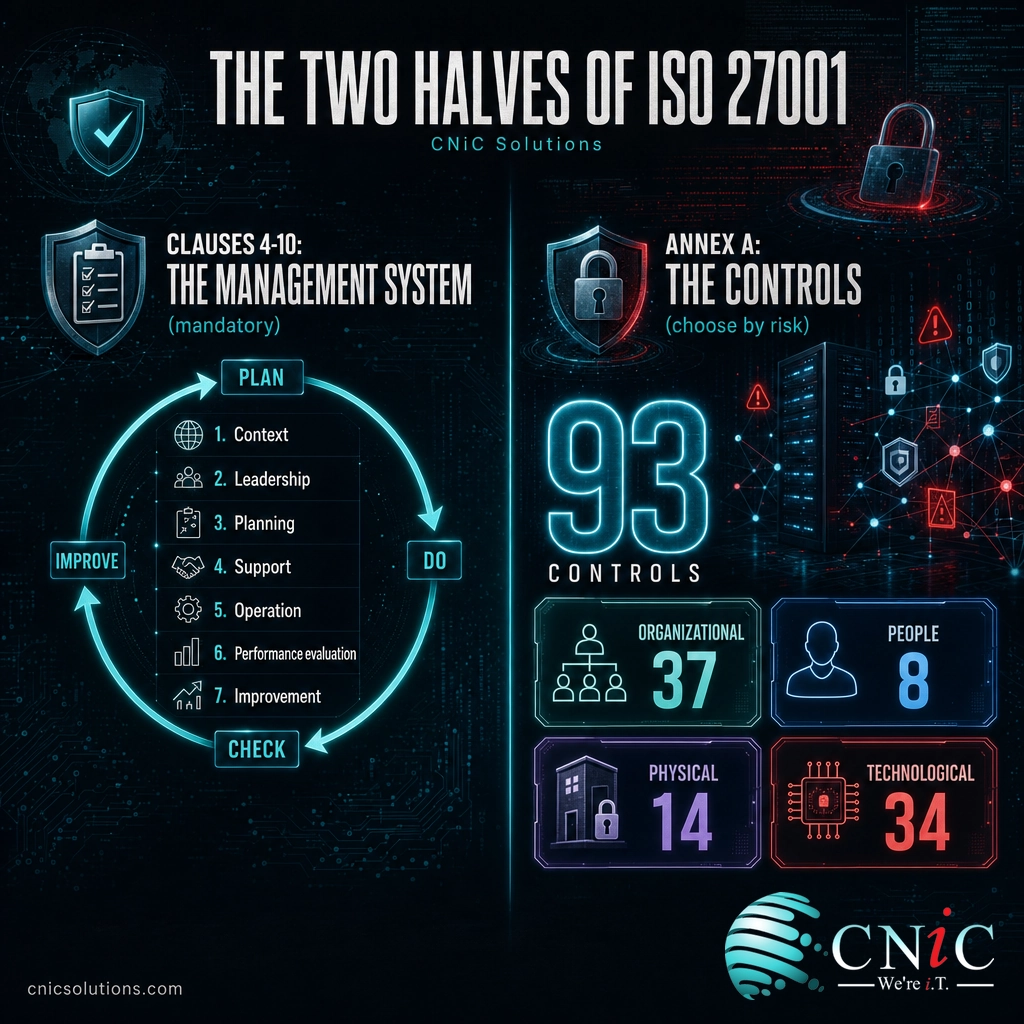
- The standard has two halves. Mandatory management clauses 4 through 10 define the ISMS itself, and Annex A provides a menu of 93 security controls to choose from based on risk.
- It is risk-based, not a fixed checklist. You apply only the controls your risk assessment justifies, and you document those choices in a Statement of Applicability.
- The current version is ISO/IEC 27001:2022. It reorganized Annex A from 114 controls into 93 under four themes and added 11 new controls, including threat intelligence and cloud security.
- Certification is proof for customers. An accredited certificate is independent evidence that your security program works, which is why buyers and partners increasingly require it.
- It is not the same as SOC 2. ISO 27001 is an international certificate; SOC 2 is a US attestation report against different criteria.
- The path is gradual, not instant. Most organizations reach certification in 3 to 12 months, then maintain it with annual surveillance audits over a three-year cycle.
What’s in This Guide
- What ISO 27001 Actually Is
- How ISO 27001 Works: The Two Halves of the Standard
- The 93 Annex A Controls, Grouped Into Four Themes
- ISO 27001 vs. SOC 2: Clearing Up the Confusion
- Why ISO 27001 Matters for Your Business
- What Changed in the ISO 27001:2022 Update
- How to Get Started With ISO 27001
- Common ISO 27001 Mistakes to Avoid
- Related Terms
- Frequently Asked Questions
1What ISO 27001 Actually Is
ISO 27001 is an international standard, published jointly by the International Organization for Standardization and the International Electrotechnical Commission, that specifies the requirements for an information security management system. Its full name is ISO/IEC 27001, and the version in force today is ISO/IEC 27001:2022. Any organization, of any size and in any sector, can be certified against it.
The key word is “system.” ISO 27001 is not a piece of software, a firewall setting, or a one-time audit you pass and forget. It is a way of running security as an ongoing management discipline, the same way an organization manages quality or safety. A useful analogy: a smoke detector is a control, but ISO 27001 is the whole fire-safety program, the policies, responsibilities, drills, inspections, and improvements that make sure the detectors are the right ones, are working, and get better over time.
Everything in the standard serves three goals, often called the CIA triad: keeping information confidential (only the right people can see it), intact (it is accurate and not tampered with), and available (it is there when the business needs it). An ISMS is simply the structured way an organization protects all three, backed by evidence. That discipline is the foundation of broader IT compliance for small business, where ISO 27001 often becomes the backbone the other requirements hang from.
Source: ISO/IEC 27001:2022 official standard page
2How ISO 27001 Works: The Two Halves of the Standard
To understand ISO 27001, it helps to see that the standard is built in two distinct parts, and certification depends on both. Many newcomers focus only on the control list and miss the management system that gives those controls meaning.
The management clauses (Clauses 4 to 10) are mandatory
The main body of ISO 27001 contains seven clauses, numbered 4 through 10, and every one is required for certification. They describe how to establish, operate, and continually improve the ISMS itself. In plain terms, they cover:
- Context (Clause 4): understand your organization, the information you must protect, and who has a stake in it.
- Leadership (Clause 5): top management owns security, sets policy, and assigns responsibility.
- Planning (Clause 6): assess risks, decide how to treat them, and set measurable objectives.
- Support (Clause 7): provide the people, training, awareness, and documented information the ISMS needs.
- Operation (Clause 8): actually carry out the risk treatment and run the controls day to day.
- Performance evaluation (Clause 9): monitor, measure, run internal audits, and hold management reviews.
- Improvement (Clause 10): fix nonconformities and keep making the system better.
Notice the shape: it is a continuous loop of plan, do, check, and improve. That is deliberate. ISO 27001 assumes threats change, so a certified ISMS is never “finished,” it is maintained.
Annex A is the menu of controls
The second half is Annex A, a reference list of 93 security controls covering everything from access management and encryption to physical security and supplier relationships. Crucially, Annex A is a menu, not a mandate. You do not implement all 93. Instead, your risk assessment in Clause 6 determines which controls are relevant, and you record every include-or-exclude decision, with justification, in a document called the Statement of Applicability. This is what makes ISO 27001 risk-based rather than a rigid checklist, and it is why two certified companies can look quite different under the hood. Deciding what to protect first starts with a structured cybersecurity risk assessment, the input that drives the whole Statement of Applicability.
Source: ISO/IEC 27001:2022 official standard page
3The 93 Annex A Controls, Grouped Into Four Themes
In the 2022 version, the 93 Annex A controls are organized into four themes, which makes the once-sprawling list far easier to navigate. Each theme answers a different question about how information is protected.
Annex A controls by theme (ISO/IEC 27001:2022)
Source: ISO/IEC 27001:2022 Annex A and ISO/IEC 27002:2022. Totals: 37 + 34 + 14 + 8 = 93 controls.
| Theme | Controls | What It Covers | Examples |
|---|---|---|---|
| Organizational (A.5) | 37 | Policies, roles, and governance that steer the whole program | Information security policies, supplier relationships, threat intelligence, incident management |
| People (A.6) | 8 | How staff and contractors are managed around security | Screening, security awareness training, disciplinary process, remote working |
| Physical (A.7) | 14 | Protecting the physical spaces and equipment that hold information | Secure areas, clear desk and screen, equipment disposal, cabling security |
| Technological (A.8) | 34 | The technical safeguards on systems, networks, and data | Access control, encryption, logging, malware protection, secure development |
A companion standard, ISO/IEC 27002, exists specifically to explain how to implement each of these controls in depth. You are certified against 27001; you reach for 27002 when you need practical guidance on a given control. Together they let an organization protect the technical, human, and physical sides of security under one coherent framework rather than a patchwork of disconnected tools.
Get the Annex A controls implemented and managed for you
Source: ISO/IEC 27001:2022 official standard page | ISO/IEC 27002:2022 (control implementation guidance)
4ISO 27001 vs. SOC 2: Clearing Up the Confusion
The term most often confused with ISO 27001 is SOC 2. Both are ways to demonstrate that an organization takes information security seriously, and buyers frequently ask for one or the other, so it is worth being precise about how they differ.
The simplest distinction is what you end up holding. ISO 27001 gives you a certificate, issued by an accredited certification body, that says your ISMS meets an international standard. SOC 2 gives you a report, written by a licensed CPA firm, describing how well your controls meet the American Institute of CPAs’ Trust Services Criteria. A certificate is a pass or fail credential; a report is a detailed narrative an auditor hands to your customers to read.
Geography and audience differ too. ISO 27001 is recognized globally and tends to be expected by international customers, while SOC 2 originated in the United States and is most common in North American software and service deals. Many organizations that sell in both markets eventually pursue both, because the underlying security work overlaps heavily. If SOC reports are on your radar, our explainer on SOC 1 vs SOC 2 covers how those two reports differ from each other.
| Aspect | ISO 27001 | SOC 2 |
|---|---|---|
| What you get | A certificate | An attestation report |
| Who issues it | An accredited certification body | A licensed CPA firm |
| Based on | The ISO/IEC 27001 standard and its ISMS requirements | The AICPA Trust Services Criteria |
| Primary market | International | United States and North America |
| Nature | Certifies a management system | Reports on control effectiveness over time |
Neither is inherently “better.” The right choice depends on where your customers are and what they ask for. What both share is the expectation of a real, working security program underneath, which is the part no report or certificate can fake.
Source: ISO/IEC 27001:2022 official standard page | AICPA SOC 2 overview
5Why ISO 27001 Matters for Your Business
ISO 27001 has moved from a nice-to-have badge to a practical business requirement, for two reasons: it opens doors commercially, and it genuinely reduces the risk and cost of a security incident. Both are measurable.
On the commercial side, certification is now a common condition in contracts, security questionnaires, and vendor reviews, especially in regulated industries and any deal involving sensitive data. A certificate lets a prospect check a box instead of running a lengthy audit of your security, which shortens sales cycles and removes objections. Adoption reflects that pull.
On the risk side, the controls ISO 27001 asks you to implement are the same ones that prevent breaches or contain them quickly when they happen, and the financial stakes are substantial.
Myth: “An ISO 27001 certificate means we can’t be breached.”
Certification is not a guarantee of immunity, and treating it that way is dangerous. ISO 27001 proves you have a disciplined, risk-based system for managing security, not that every attack will fail. Its real value is that a certified organization is far better prepared to prevent incidents, spot them faster, and recover in an orderly way, which is exactly what the breach-cost data rewards. The certificate is evidence of good management, not a force field.
Put together, the case is straightforward: certification helps you win business you would otherwise be locked out of, and it strengthens the safeguards that keep a bad day from becoming a catastrophic one. That is why so many companies treat ISO 27001 not as a cost, but as an investment that pays back in both revenue and resilience. Standing up and running that management system is often where a fractional security leader adds the most value.
Build the security controls behind ISO 27001 with expert help
Source: ISO Survey 2023 | IBM Cost of a Data Breach Report 2025
6What Changed in the ISO 27001:2022 Update
If you read older articles about ISO 27001, you will see references to 114 controls across 14 domains. That describes the previous 2013 version. The standard was revised in 2022, and understanding the change matters because the transition period has now closed.
The headline change is Annex A. The 2013 edition’s 114 controls in 14 domains were consolidated and modernized into 93 controls under four themes. This was a reorganization rather than a rollback: many old controls were merged, and 11 brand-new controls were added to reflect how technology and threats had evolved. The additions include controls for threat intelligence, information security for cloud services, data leakage prevention, secure coding, and monitoring activities, gaps that barely existed when the 2013 version was written. The management clauses (4 to 10) saw only minor wording and structural updates.
| Aspect | ISO/IEC 27001:2013 | ISO/IEC 27001:2022 |
|---|---|---|
| Annex A controls | 114 | 93 |
| Structure | 14 domains | 4 themes |
| New controls | Baseline | 11 added (e.g., threat intelligence, cloud security) |
| Status | Retired for certification | The version all valid certificates now use |
The transition deadline has passed. Accreditation bodies set a three-year window to move from the 2013 to the 2022 version, and that window closed on October 31, 2025. Any certificate still referencing the 2013 standard is now considered invalid, so every organization that holds a current, valid ISO 27001 certificate is certified against the 2022 version. If you are evaluating a vendor’s certificate, confirm it reads ISO/IEC 27001:2022.
Source: ISO/IEC 27002:2022 (Annex A control set) | ISO/IEC 27001:2022 official standard page
7How to Get Started With ISO 27001
Certification can look daunting, but the path is well-worn and predictable. It is a sequence, and each step makes the next one easier. The biggest mistakes come from jumping ahead, so the order below is the order that works.
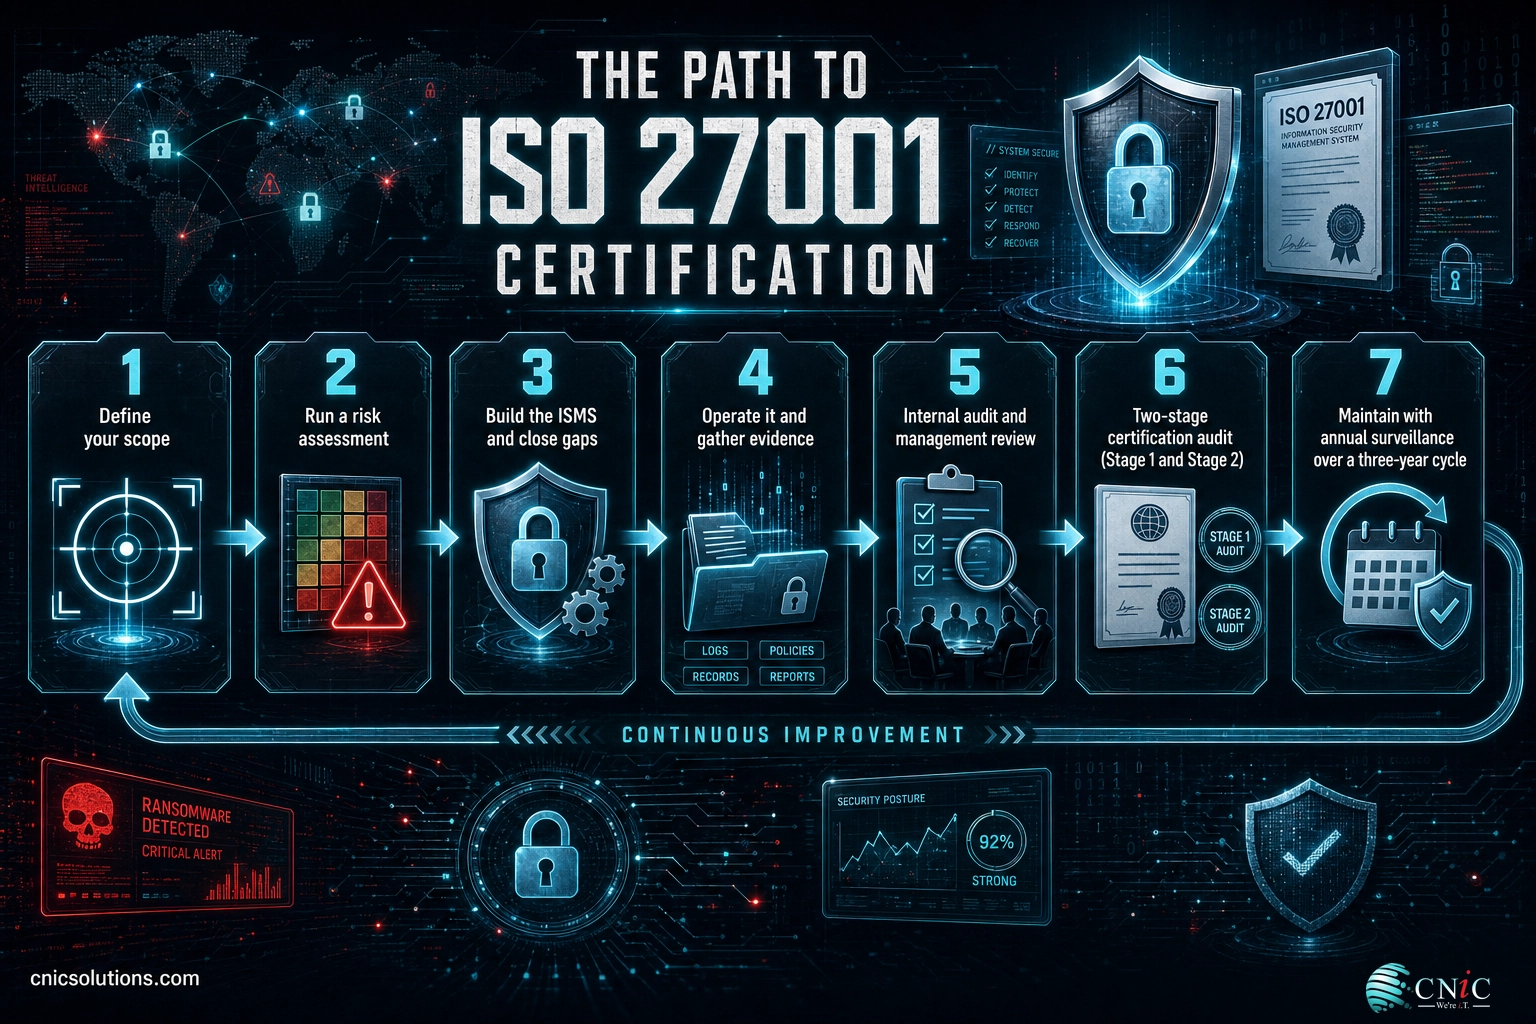
- Define your scope. Decide which parts of the business, systems, and information the ISMS will cover. A tight, well-chosen scope keeps the project manageable and the audit focused.
- Run a risk assessment. Identify what could go wrong for the information in scope, then rank those risks. This drives every control decision that follows and produces your Statement of Applicability.
- Build the ISMS and close the gaps. Write the required policies, assign responsibilities, and implement the Annex A controls your risk assessment selected, from access control and encryption to training and supplier management.
- Operate it and gather evidence. Run the system for a period so it produces real records: logs, audit trails, training completions, and incident handling. In an audit, undocumented work effectively did not happen.
- Conduct an internal audit and management review. Check your own ISMS against the standard, fix what you find, and have leadership formally review it. Both are required before an external auditor arrives.
- Pass the two-stage certification audit. An accredited certification body runs Stage 1 (a documentation and readiness review) and Stage 2 (a deeper audit of whether your controls actually work). Clear both and you are certified.
- Maintain it. The certificate is valid for three years, with annual surveillance audits to confirm the ISMS is still running, followed by a full recertification audit to renew.
Most organizations reach certification in roughly 3 to 12 months, depending on size, scope, and how mature their security already is. The slowest parts are almost always closing control gaps and building the evidence trail, which is exactly the continuous work a managed IT and security partner handles day to day. The strategic side, owning the program, interpreting the standard, and steering the risk decisions, is the role a virtual CISO fills without the cost of a full-time security executive.
Get a security leader to own your ISO 27001 program
Source: ISO/IEC 27001:2022 official standard page
8Common ISO 27001 Mistakes to Avoid
The same missteps trip organizations up again and again. Knowing them in advance turns a stressful scramble into a manageable project.
Treating it as an IT-only project. ISO 27001 requires leadership ownership and reaches into HR, facilities, legal, and operations. Handing the whole thing to the IT team guarantees gaps in the people and organizational controls.
Scoping too broadly on the first attempt. Trying to certify the entire enterprise at once makes the project slower and more expensive than it needs to be. A focused initial scope certifies faster and can expand later.
Buying tools instead of building the system. Security products are useful, but a control only counts when it is configured, enforced, and documented. Software alone does not certify you.
Neglecting the evidence. Doing the right things but keeping no records is the classic reason a Stage 2 audit stalls. Auditors assess what you can prove, not what you say you do.
Letting it lapse after certification. ISO 27001 is a three-year cycle with annual surveillance audits, not a one-time event. Organizations that stop maintaining the ISMS the day after the certificate arrives risk failing the very next audit.
The common thread: nearly every ISO 27001 failure comes from treating it as a one-time technical project rather than an ongoing, business-wide management system. The organizations that succeed assign clear ownership, keep evidence as they go, and start with a realistic scope. If ISO 27001 sits alongside other frameworks you must meet, our guide to IT compliance for small business shows how they fit together, and our overview of CMMC compliance covers a related standard for defense contractors.
Related Terms
- ISMS (Information Security Management System): The risk-based framework of policies, processes, and controls that ISO 27001 requires you to build and run.
- Annex A: The reference list of 93 security controls in ISO 27001:2022, applied selectively based on your risk assessment.
- Statement of Applicability (SoA): The document that records which Annex A controls you apply, which you exclude, and why.
- ISO/IEC 27002: The companion standard that explains, in detail, how to implement each Annex A control. You certify against 27001, not 27002.
- SOC 2: A US attestation report against the AICPA Trust Services Criteria; our SOC 1 vs SOC 2 guide explains where it fits.
- Virtual CISO (vCISO): A fractional security leader who can own and run an ISO 27001 program; see what a vCISO does.
- Managed Security Services (MSSP): An outsourced model for running the continuous monitoring and response ISO 27001 expects; see what an MSSP does.
Frequently Asked Questions
What is ISO 27001 in simple terms?
How many controls are in ISO 27001:2022?
What is the difference between ISO 27001 and ISO 27002?
Is ISO 27001 mandatory?
What is the difference between ISO 27001 and SOC 2?
How long does ISO 27001 certification take?
How long is an ISO 27001 certificate valid?
Methodology and Sources
This guide describes ISO/IEC 27001 using the official standard and its companion documents, cited inline. The definition, ISMS requirements, and Clause 4 to 10 structure come from the ISO/IEC 27001:2022 standard published by ISO and IEC. The Annex A control set and the four-theme breakdown (37 organizational, 8 people, 14 physical, and 34 technological, totaling 93) come from ISO/IEC 27001:2022 Annex A and its companion ISO/IEC 27002:2022, which also documents the reorganization from the 2013 version’s 114 controls in 14 domains and the 11 newly added controls. Adoption figures are drawn from the ISO Survey 2023, which notes that China’s data was not included that year. Breach-cost and detection-time figures ($4.44M average and 241 days) are from the IBM Cost of a Data Breach Report 2025. The SOC 2 comparison references the AICPA Trust Services Criteria. The October 31, 2025 transition deadline reflects the three-year window set by the accreditation bodies. This guide is educational and does not constitute legal or certification advice; confirm your specific scope and obligations with an accredited certification body or qualified advisor.
Last Updated: August 2026.


related posts
What Is IT Asset Management (ITAM)? A Guide for Businesses
October 22, 2026IT asset management (ITAM) is the practice of tracking and managing an organization's hardware, software, and…
What Is Infrastructure as Code (IaC)? A Guide for Businesses
October 21, 2026Infrastructure as Code (IaC) is the practice of managing and provisioning IT infrastructure, such as servers,…
What Is Infrastructure Security? A Guide for Businesses
October 21, 2026Infrastructure security is the practice of protecting the core technology systems a business runs on: its…
What Is GDPR? A Data Protection Compliance Guide for Businesses
October 20, 2026GDPR (the General Data Protection Regulation) is a European Union law that governs how organizations collect,…