If you build parts, provide services, or supply goods to the U.S. Department of Defense, CMMC compliance is quickly becoming the price of admission to that work. The Cybersecurity Maturity Model Certification is the DoD’s way of verifying that everyone in its supply chain, from a prime contractor down to a small machine shop, actually protects the sensitive information they handle. This guide explains what CMMC compliance is in plain terms, how it relates to NIST SP 800-171, the three certification levels and which one applies to you, and the practical path a contractor or manufacturer follows to get certified and stay that way.
CMMC compliance is meeting and verifying the cybersecurity controls the Department of Defense requires under the Cybersecurity Maturity Model Certification program to protect Federal Contract Information and Controlled Unclassified Information. It matters because the required CMMC level is written into DoD contracts, so certification becomes a condition of being eligible to win and keep defense work.
Key Takeaways
- CMMC verifies protection you were already supposed to have. It confirms, through assessment, that a contractor meets the DoD’s information-security requirements rather than just claiming to.
- There are three levels. Level 1 covers 15 basic requirements for Federal Contract Information, Level 2 covers the 110 requirements of NIST SP 800-171 for Controlled Unclassified Information, and Level 3 adds selected NIST SP 800-172 requirements.
- The rule is in effect. The CMMC Program rule became effective December 16, 2024, and requirements are phasing into contracts over roughly three years.
- It flows down the supply chain. Subcontractors and suppliers, including manufacturers who never contract directly with the DoD, can be required to certify because a prime they serve requires it.
- NIST 800-171 and CMMC are partners, not the same thing. NIST defines the 110 controls; CMMC Level 2 confirms and certifies them.
- Evidence is the deliverable. Assessors want documented proof each control is implemented, not a verbal assurance that it exists.
- Starting early is the advantage. Closing gaps and building an audit-ready evidence package is the slow part, so contractors who begin now protect their eligibility for future awards.
What’s in This Guide
- What CMMC Compliance Really Means
- How CMMC Works: From Contract to Certification
- The Three CMMC Levels Explained
- CMMC vs. NIST SP 800-171: Clearing Up the Confusion
- What CMMC Protects: FCI vs. CUI
- Why CMMC Matters for Contractors and Manufacturers
- How to Get Started With CMMC Compliance
- Common CMMC Mistakes to Avoid
- Related Terms
- Frequently Asked Questions
1What CMMC Compliance Really Means
The Cybersecurity Maturity Model Certification is a Department of Defense program that verifies contractors have implemented the security protections required to safeguard the government’s sensitive information. For years, DoD contracts required contractors to meet cybersecurity standards on the honor system: you attested that you were compliant, and the government largely took your word for it. CMMC replaces that self-attestation model with verification, so a claim of compliance now has to be backed by an assessment.
That shift is the heart of it. CMMC does not, for the most part, invent brand-new security requirements. It takes the requirements the DoD already expected, most importantly the 110 controls in NIST SP 800-171, and adds a mechanism to confirm you actually meet them before you can be awarded the work. The required level is stated in the contract, and if you cannot demonstrate that level, you are not eligible.
For a contractor or manufacturer, that reframes cybersecurity from an internal good practice into a direct business requirement. A missing control is no longer just a risk on a spreadsheet. It can be the reason a bid is disqualified or a supplier relationship ends. This is also why CMMC is best understood as one piece of a broader obligation to protect data and prove it, the same discipline covered in our overview of IT compliance for small business.
Source: Federal Register, CMMC Program final rule (89 FR 83092) | NIST SP 800-171
2How CMMC Works: From Contract to Certification
CMMC can feel abstract until you see it as a sequence tied to winning work. The process is the same whether you are a large prime or a small supplier, and understanding the order makes the requirement far less intimidating.
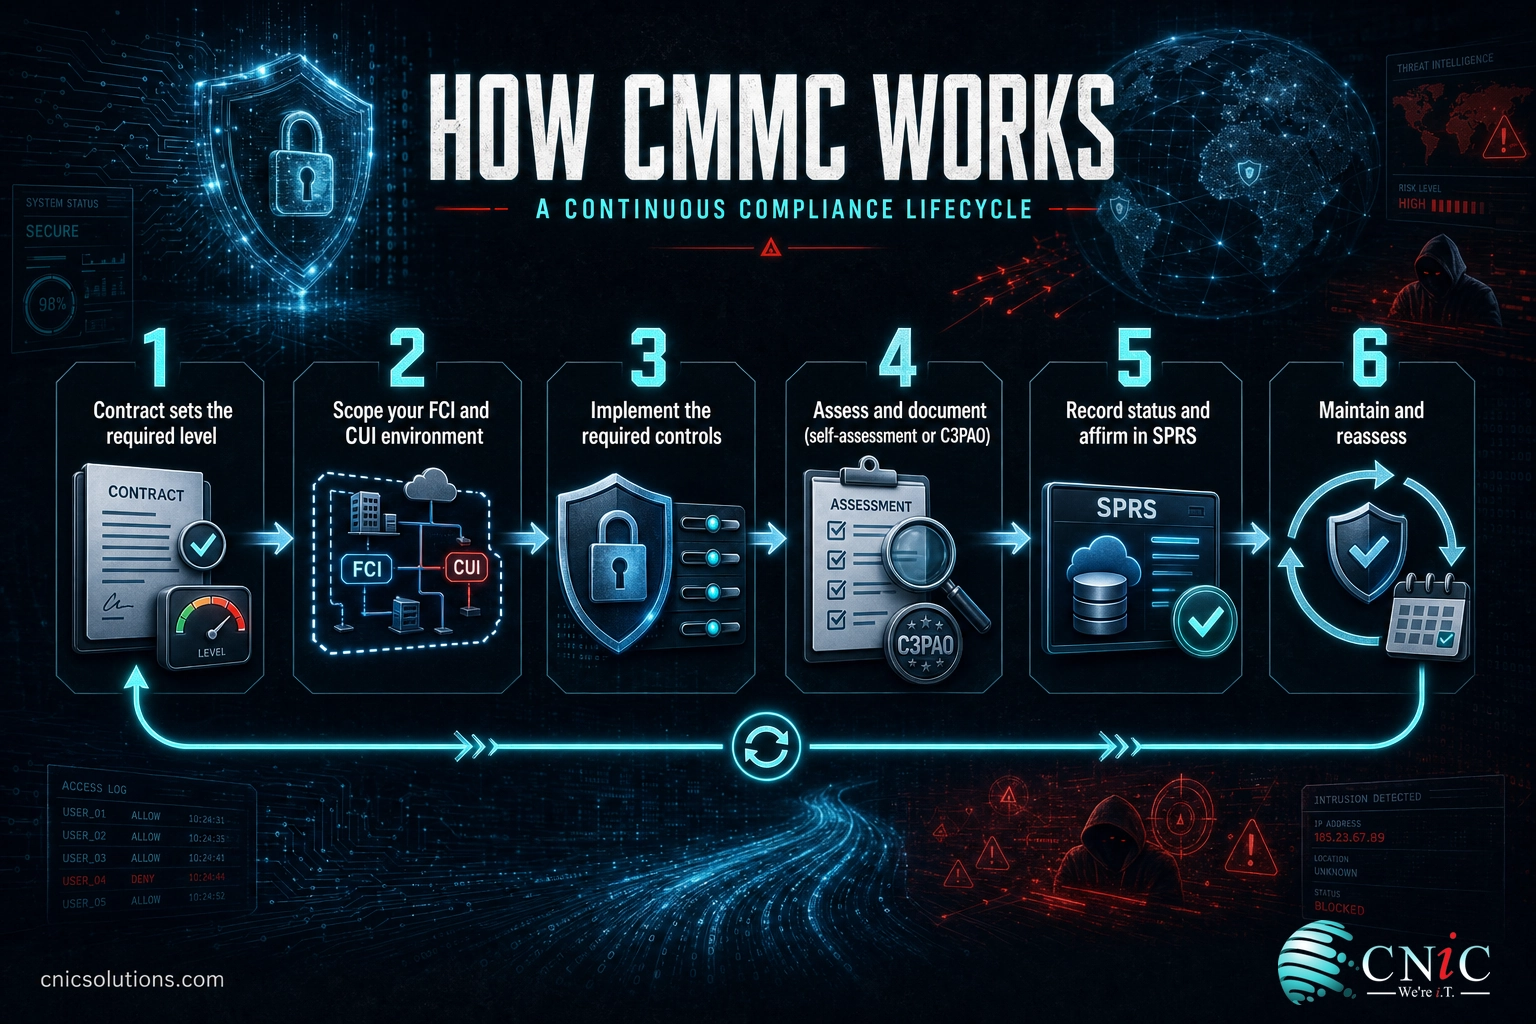
- The contract sets the level. The DoD determines what information a contract involves and specifies the required CMMC level, from Level 1 to Level 3, in the solicitation.
- You scope your environment. You identify exactly where Federal Contract Information and Controlled Unclassified Information live in your systems. That boundary defines what the assessment covers.
- You implement the required controls. You put the safeguards for your level in place, from access control and encryption to logging and training, and configure them so they are enforced everywhere in scope.
- You assess and document. Depending on the level, you complete a self-assessment or bring in a certified third-party assessor, and you gather the evidence that proves each control is working.
- You record and affirm your status. Results and a senior-official affirmation are recorded in the DoD’s Supplier Performance Risk System (SPRS), and your standing is checked as part of eligibility for award.
- You maintain it. Certification is not permanent. You keep controls enforced, re-affirm annually, and reassess on the required cycle to stay eligible over the life of your contracts.
The important insight is that assessment sits near the end, not the beginning. Most of the work, and most of the time, goes into steps two through four: scoping accurately, closing control gaps, and building the documentation that makes an assessment go smoothly. A structured cybersecurity risk assessment is usually the most valuable early move, because it turns a vague sense of exposure into a ranked list of exactly what to fix.
Source: Federal Register, CMMC Program final rule | NIST SP 800-171
3The Three CMMC Levels Explained
CMMC is organized into three levels, and the level you need is driven entirely by the sensitivity of the information your contract involves. More sensitive information means more controls and a more rigorous form of verification. You do not choose your level; the contract does.
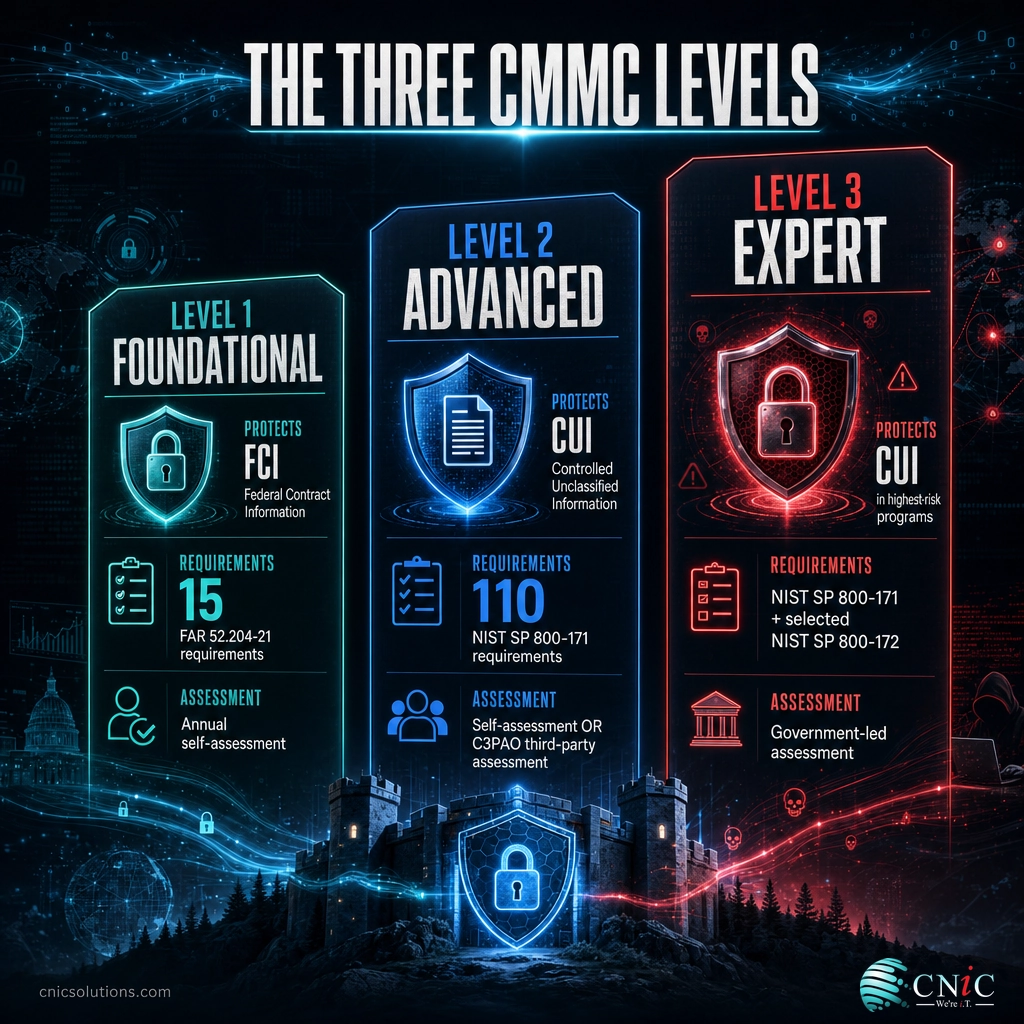
Level 1: Foundational
Level 1 applies to contractors that handle Federal Contract Information but not Controlled Unclassified Information. It covers 15 basic safeguarding requirements drawn from Federal Acquisition Regulation clause 52.204-21, the kind of fundamental hygiene most businesses should already practice, such as limiting who can access systems and protecting the physical workplace. Level 1 is met through an annual self-assessment and an annual affirmation by a company official. There is no third-party assessment.
Level 2: Advanced
Level 2 is where most defense contractors and manufacturers that handle Controlled Unclassified Information land, and it is the level most people mean when they talk about CMMC. It maps directly to the 110 security requirements in NIST SP 800-171. Depending on the type of information and the contract, Level 2 is verified either by a self-assessment or, more commonly for sensitive CUI, by a certified third-party assessment organization known as a C3PAO, on a recurring cycle. The C3PAO route is the meaningful change from the old model, because an independent assessor now checks your work.
Level 3: Expert
Level 3 is reserved for programs facing the most advanced threats, and it raises the bar in two ways. It builds on the full NIST SP 800-171 baseline and adds a subset of the enhanced requirements from NIST SP 800-172, and it is assessed by the government rather than a commercial assessor. Relatively few companies need Level 3, but for those handling the most critical information, it reflects the reality that determined, well-resourced adversaries target the defense supply chain.
Security requirements by CMMC level
Source: NIST SP 800-171, NIST SP 800-172, and DoD CMMC program. Level 3 adds a DoD-selected subset of NIST SP 800-172 enhanced requirements on top of the 110 in 800-171.
| Level | Name | Protects | Based On | How It Is Verified |
|---|---|---|---|---|
| Level 1 | Foundational | Federal Contract Information (FCI) | FAR 52.204-21 (15 requirements) | Annual self-assessment |
| Level 2 | Advanced | Controlled Unclassified Information (CUI) | NIST SP 800-171 (110 requirements) | Self-assessment or C3PAO third-party assessment |
| Level 3 | Expert | CUI in the highest-risk programs | NIST SP 800-171 plus selected NIST SP 800-172 | Government-led assessment |
Get help identifying the right CMMC level for your contracts
Source: NIST SP 800-171 | Federal Register, CMMC Program final rule
4CMMC vs. NIST SP 800-171: Clearing Up the Confusion
The single most common point of confusion is the relationship between CMMC and NIST SP 800-171. People often use the two terms as if they were interchangeable, and they are not, though they are tightly connected.
Think of it this way. NIST SP 800-171 is the rulebook: a catalog of 110 security requirements, published by the National Institute of Standards and Technology, for protecting Controlled Unclassified Information on non-government systems. CMMC is the referee: the DoD program that checks, through assessment, whether you actually follow the rulebook. NIST 800-171 tells you what to do; CMMC Level 2 confirms and certifies that you have done it.
The reason the distinction matters is practical. Under the older DFARS self-attestation approach, a contractor could implement NIST 800-171 on paper, post a self-assessment score, and win work without anyone independently checking. CMMC closes that gap by requiring verification, and for sensitive CUI, that verification comes from an independent C3PAO. So the controls you implement are largely the same. What changes is that someone else now confirms them, and the standard of proof is higher.
| Aspect | NIST SP 800-171 | CMMC |
|---|---|---|
| What it is | A catalog of security requirements | A DoD certification program |
| Who publishes it | NIST | U.S. Department of Defense |
| What it does | Defines the 110 controls for protecting CUI | Verifies that the controls are actually in place |
| How it is proven | Historically self-attested | Self-assessment or independent C3PAO assessment |
| Relationship | The standard | The verification of that standard (Level 2 = 800-171) |
Source: NIST SP 800-171 | Federal Register, CMMC Program final rule
5What CMMC Protects: FCI vs. CUI
To know which level applies to you, you first have to know what kind of government information you touch. CMMC exists to protect two categories, and the difference between them determines almost everything about your obligation.
Federal Contract Information (FCI) is information provided by or generated for the government under a contract that is not intended for public release, but is not especially sensitive. Think of routine contract details and communications that should not be posted publicly. Handling FCI, without any CUI, generally puts you at Level 1.
Controlled Unclassified Information (CUI) is more sensitive, government-created or government-owned information that requires safeguarding under law or policy, even though it is not classified. Technical drawings, specifications, and other data tied to defense work commonly fall here. Handling CUI raises you to Level 2 and the full NIST SP 800-171 baseline, and in the highest-risk cases, Level 3.
Myth: “We only make parts, so CMMC does not apply to us.”
Manufacturers frequently assume CMMC is a prime-contractor problem. In practice, the moment you receive a technical drawing or specification marked as CUI in order to build something, you are handling exactly the information CMMC protects, and the requirement flows down to you through your customer’s contract. Being a subcontractor or supplier does not exempt you. It is one of the most common ways a small manufacturer discovers, often late, that it needs to certify.
Because the FCI-versus-CUI question drives your level, getting it right early is worth real effort. Misjudging it, and assuming FCI when you actually hold CUI, is how contractors under-scope their program and get caught short when a contract requires certification. When it is unclear, treat the classification of your data as the first thing to nail down, ideally with experienced help.
Source: Federal Register, CMMC Program final rule | NIST SP 800-171
6Why CMMC Matters for Contractors and Manufacturers
CMMC is not paperwork for its own sake. It exists because the defense supply chain is a real and heavily targeted attack surface, and because a single weak supplier can expose sensitive information across an entire program. For a contractor or manufacturer, the requirement carries two kinds of weight: eligibility for revenue, and genuine protection against threats that are actively hunting your sector.
Start with the scope of who is affected. The Department of Defense’s supply chain is enormous, spanning small shops and large primes alike, and CMMC reaches across it.
The threat side is just as concrete. Manufacturing has repeatedly ranked as the most-attacked industry in IBM’s X-Force Threat Intelligence Index, a reflection of how attractive production environments and their intellectual property are to attackers. When a defense manufacturer is compromised, the fallout is not only downtime and recovery cost. It can mean the loss of controlled technical data that a nation-state adversary was specifically after. For the underlying figures on attacks, downtime, and operational-technology risk in this sector, see our roundup of manufacturing cybersecurity statistics.
Put the two together and the business case is clear. The controls CMMC requires are the same controls that keep a breach from happening or contain it when it does, which is why the program is best treated as risk reduction rather than a compliance tax. The contractors that thrive are the ones that build these safeguards into how they operate, then let certification follow, an approach that also strengthens the broader technology backbone of a modern manufacturing operation.
Source: IBM Cost of a Data Breach Report 2025 | IBM X-Force Threat Intelligence Index
7How to Get Started With CMMC Compliance
The scale of CMMC can be paralyzing if you look at all 110 requirements at once, so the practical answer is to work it as a sequence. The path below takes a contractor or manufacturer from uncertainty to an audit-ready, certifiable posture. The order matters: each step makes the next one easier, and the biggest mistake is jumping to a formal assessment before the groundwork is done.
- Determine your level and scope. Establish whether you handle FCI, CUI, or both, and identify every system where that information lives. Your level and the boundary of your assessment both fall out of this step.
- Run a gap assessment against your level’s requirements. Measure your current controls against the 15 requirements for Level 1 or the 110 for Level 2, and produce a ranked list of what is missing. This is the single most valuable step, because it converts the whole standard into a concrete to-do list.
- Remediate the gaps. Implement and correctly configure the missing controls: multi-factor authentication, encryption of CUI, access management, logging, patching, endpoint protection, and security awareness training. Configuration matters as much as deployment, because a control that is not enforced everywhere will not pass.
- Document everything as evidence. Write the required policies, including a System Security Plan, and capture the records that prove each control works. In an assessment, what you cannot document effectively did not happen.
- Self-assess or engage a C3PAO. For Level 1 and self-assessed Level 2, complete and affirm your assessment in SPRS. For third-party Level 2, schedule a certified C3PAO once you are confident the evidence holds up.
- Maintain and re-affirm. Keep controls enforced, monitor continuously, re-affirm annually, and reassess on the required cycle so you stay eligible as contracts renew.
Most contractors do not have the in-house time or specialized expertise to run this alone, which is where a partner earns its keep. Ongoing monitoring, patching, logging, and evidence collection are exactly the continuous work a managed IT and security partner handles day to day, while the strategic side, scoping, framework interpretation, and program ownership, is the role a virtual CISO or Virtual CIO fills without the cost of a full-time executive.
Build a certifiable CMMC security program with expert help
Source: NIST SP 800-171 | Federal Register, CMMC Program final rule
8Common CMMC Mistakes to Avoid
The same missteps trip up contractors again and again, and knowing them in advance saves months of wasted effort. Each of these turns a manageable project into a scramble.
Waiting for a contract to require it. By the time a solicitation names a required level, there is rarely enough time to scope, remediate, document, and pass an assessment before the deadline. Certification is a lead time, not a last-minute box.
Mis-scoping the environment. Defining the boundary too broadly makes the project needlessly expensive; too narrowly leaves CUI unprotected and the assessment invalid. Accurate scoping is the foundation everything else rests on.
Confusing tools with compliance. Buying security products and assuming the requirement is met. A control only counts when it is configured, enforced everywhere in scope, and documented.
Neglecting documentation. Doing the right things but keeping no records. A System Security Plan and supporting evidence are not optional; they are what an assessor actually reviews.
Assuming flow-down does not apply. Treating CMMC as someone else’s problem because you are a subcontractor, then losing a supplier relationship when your customer requires certification you do not have.
The common thread: almost every CMMC failure is a gap between doing something and being able to prove it, combined with starting too late. Contractors that assign ownership, keep evidence, and begin early clear certification with far less pain than those that treat it as a fire drill. For a broader view of how these habits apply across every regulation a business faces, our guide to IT compliance for small business puts CMMC in context with the other frameworks you may need to meet.
Related Terms
- NIST SP 800-171: The catalog of 110 security requirements for protecting Controlled Unclassified Information that CMMC Level 2 is built on. See our IT compliance guide for how it fits the wider picture.
- Controlled Unclassified Information (CUI): Sensitive but unclassified government information that requires safeguarding, the trigger for CMMC Level 2.
- C3PAO: A Certified Third-Party Assessment Organization authorized to conduct CMMC Level 2 certification assessments.
- DFARS 252.204-7012: The Defense contract clause that first required contractors to implement NIST SP 800-171 to safeguard defense information.
- SPRS: The DoD’s Supplier Performance Risk System, where assessment scores and affirmations are recorded.
- SOC 2: A separate, commercial attestation many service providers pursue; our guide to SOC 1 vs SOC 2 explains where it fits.
- Managed Security Services (MSSP): An outsourced model for running the continuous security work CMMC requires; see what an MSSP does.
Frequently Asked Questions
What is CMMC compliance?
What are the three levels of CMMC?
Who has to comply with CMMC?
Is CMMC the same as NIST 800-171?
When does CMMC take effect?
How long does it take to become CMMC compliant?
What happens if I am not CMMC compliant?
Methodology and Sources
This guide describes the CMMC program using official primary sources and cites them inline. The program’s structure, purpose, and December 16, 2024 effective date come from the CMMC Program final rule published in the Federal Register (89 FR 83092). The 110 security requirements for protecting Controlled Unclassified Information come from NIST Special Publication 800-171, and the enhanced requirements referenced for Level 3 come from NIST Special Publication 800-172. The Level 1 requirement count reflects FAR clause 52.204-21. Breach-cost data is drawn from the IBM Cost of a Data Breach Report 2025, and the observation that manufacturing is among the most-attacked industries reflects the IBM X-Force Threat Intelligence Index. Requirement counts and level definitions reflect the CMMC program as published; contractors should confirm the exact obligations in their specific solicitations. This guide is educational and does not constitute legal advice; verify your CMMC level and scope with qualified counsel or a certified assessor.
Last Updated: August 2026.


related posts
OKRs vs. KPIs: What’s the Difference?
September 22, 2026An OKR (Objective and Key Results) is a goal-setting framework that pairs an ambitious objective with…
Password Statistics for 2026: Reuse, Cracks, and the Passkey Shift
September 22, 2026Weak and stolen passwords are still the number one way attackers get in. In 2025, stolen…
15 Microsoft Teams Tips and Tricks to Boost Team Productivity
September 21, 2026Microsoft Teams is where most of the workday now happens: it passed 320 million monthly active…
Mobile Security Software for Business: A Buyer’s Guide
September 21, 2026Choosing mobile security software for business comes down to two decisions: how you will manage the…