A business associate agreement (BAA) is a HIPAA-required contract between a covered entity and a vendor that handles protected health information on its behalf. It defines how that vendor may use and protect the data and makes the vendor directly liable for safeguarding it. Without a signed BAA, sharing that data is itself a HIPAA violation.
The moment a medical practice hands patient records to an outside vendor, whether a cloud host, a billing company, or the IT firm that manages its servers, HIPAA requires a specific contract to travel with that data. That contract is the business associate agreement. It is short to sign and easy to overlook, yet a missing one has cost healthcare organizations hundreds of thousands of dollars in federal penalties, sometimes with no data breach involved at all. Here is exactly what a BAA is, who has to have one, what it must contain, and why skipping it is one of the most expensive shortcuts in healthcare compliance.
- A BAA is a mandatory HIPAA contract, not paperwork. Any time protected health information leaves a covered entity for a vendor to create, receive, maintain, or transmit, federal law requires a signed BAA first.
- The agreement makes the vendor directly liable. Since the 2013 Omnibus Rule, business associates can be fined by regulators on their own, and the obligations flow all the way down to subcontractors.
- Missing a BAA is a violation by itself. The first federal settlement based purely on absent BAAs was $31,000, with no breach of patient data at all.
- Penalties scale with culpability. As of January 28, 2026, HIPAA fines run from $145 per violation up to an annual cap of $2,190,294 for a single type of violation.
- Managed IT providers are business associates. If an outside IT partner can touch systems that hold patient data, that partner needs a signed BAA, and a compliant one is a baseline sign of a serious vendor.
What’s in This Guide
What Is a Business Associate Agreement?
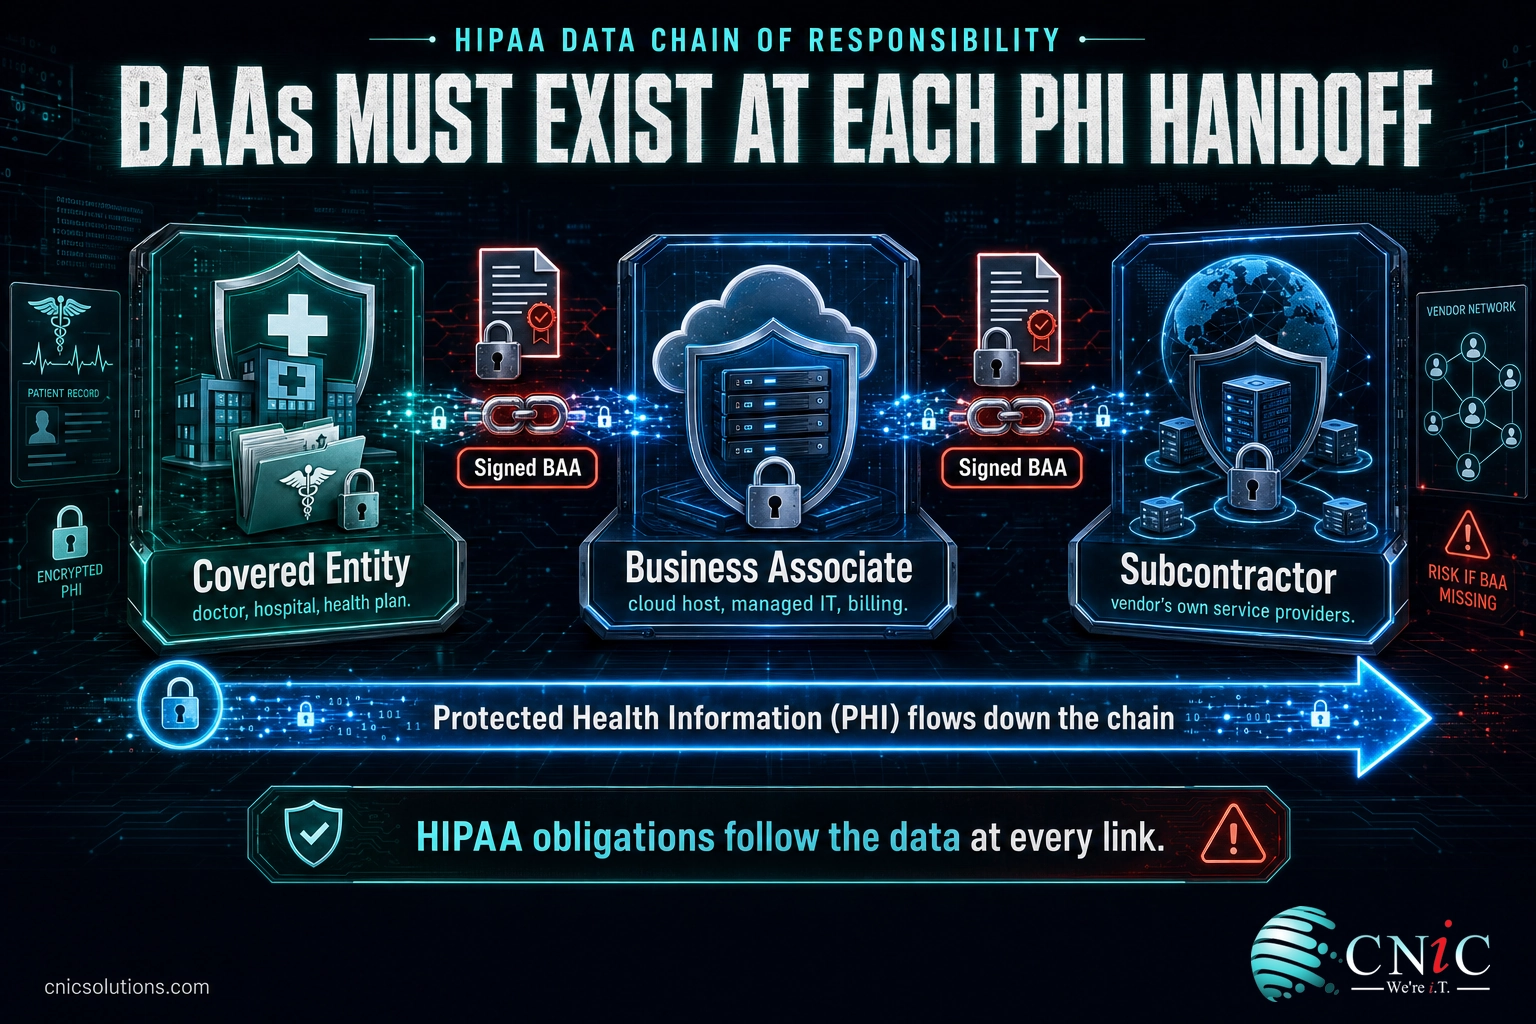
A business associate agreement is a written contract required by the HIPAA Privacy and Security Rules. It governs the relationship between a covered entity (a healthcare provider, health plan, or healthcare clearinghouse) and a business associate (an outside party that handles protected health information, or PHI, on the covered entity’s behalf). The U.S. Department of Health and Human Services (HHS) requires this contract to be in place before any PHI is shared.
The agreement does three core things. It establishes the permitted and required uses of PHI so the vendor cannot use the data for its own purposes. It obligates the vendor to safeguard that data, including applying the HIPAA Security Rule to any electronic PHI. And it creates accountability, so if something goes wrong, the responsibilities and the reporting duties are already defined in writing.
Think of it like handing a spare key to a trusted contractor. You are not just giving them access, you are setting the terms: which rooms they can enter, what they can do inside, that they must lock up when they leave, and that they will tell you immediately if a key goes missing. A BAA is that set of terms for patient data, backed by federal law rather than a handshake.
Crucially, a BAA is a specific legal instrument. A general vendor contract, a master services agreement, or a non-disclosure agreement does not satisfy HIPAA on its own. The required clauses come straight from the regulation at 45 CFR 164.504(e), and an agreement is only valid if it contains them.
Source: HHS Office for Civil Rights, Business Associates guidance
What Is a Business Associate?
To understand the agreement, you first have to understand who a business associate actually is. HHS defines a business associate as a person or organization, other than a member of the covered entity’s own workforce, that performs functions or services involving the use or disclosure of protected health information on behalf of a covered entity.
The test is functional, not by industry label. If a vendor creates, receives, maintains, or transmits PHI to do its job, it is a business associate, whether or not it ever looks at the data. Common examples include:
- Cloud and hosting providers that store electronic health records or backups.
- Managed IT and MSP partners that administer the servers, networks, and email systems where PHI lives.
- Billing, coding, and claims processing companies.
- Document storage and shredding services that handle physical records.
- Email, e-fax, and secure messaging vendors.
- Attorneys, accountants, and consultants who receive PHI to perform their work.
- Answering services and transcription providers.
One point catches many organizations off guard: an IT provider that manages a healthcare network is a business associate even if it never intentionally views a single patient record. The ability to access systems that contain PHI is enough to trigger the requirement. That is why any credible managed IT partner serving healthcare will sign a BAA as a matter of course. If a prospective provider hesitates or does not understand the request, treat that as a warning sign.
Source: HHS Office for Civil Rights, Business Associates guidance
Covered Entity vs. Business Associate
The single most common source of confusion is the difference between a covered entity and a business associate. The two roles carry different responsibilities under HIPAA, and knowing which one you are determines what you have to do. Here is how they compare.
| Attribute | Covered Entity | Business Associate |
|---|---|---|
| Who it is | Healthcare provider, health plan, or healthcare clearinghouse | Outside vendor performing a service that involves PHI |
| Relationship to the patient | Direct, collects PHI to deliver or pay for care | Indirect, receives PHI only to serve the covered entity |
| Examples | Doctor’s office, hospital, dental practice, insurer | Cloud host, MSP, billing company, shredding service |
| Must sign a BAA? | Yes, with each of its business associates | Yes, with the covered entity and with its own subcontractors |
| Directly liable to regulators? | Yes | Yes, since the 2013 Omnibus Rule |
A single organization can be both at once. A billing company is a business associate to the practices it serves, but it becomes a covered entity’s business associate that itself hires a subcontractor, and so it must sign BAAs in both directions. This chaining is deliberate. HIPAA follows the data, so the protections extend to every party that touches it, not just the first one.
What a BAA Must Include
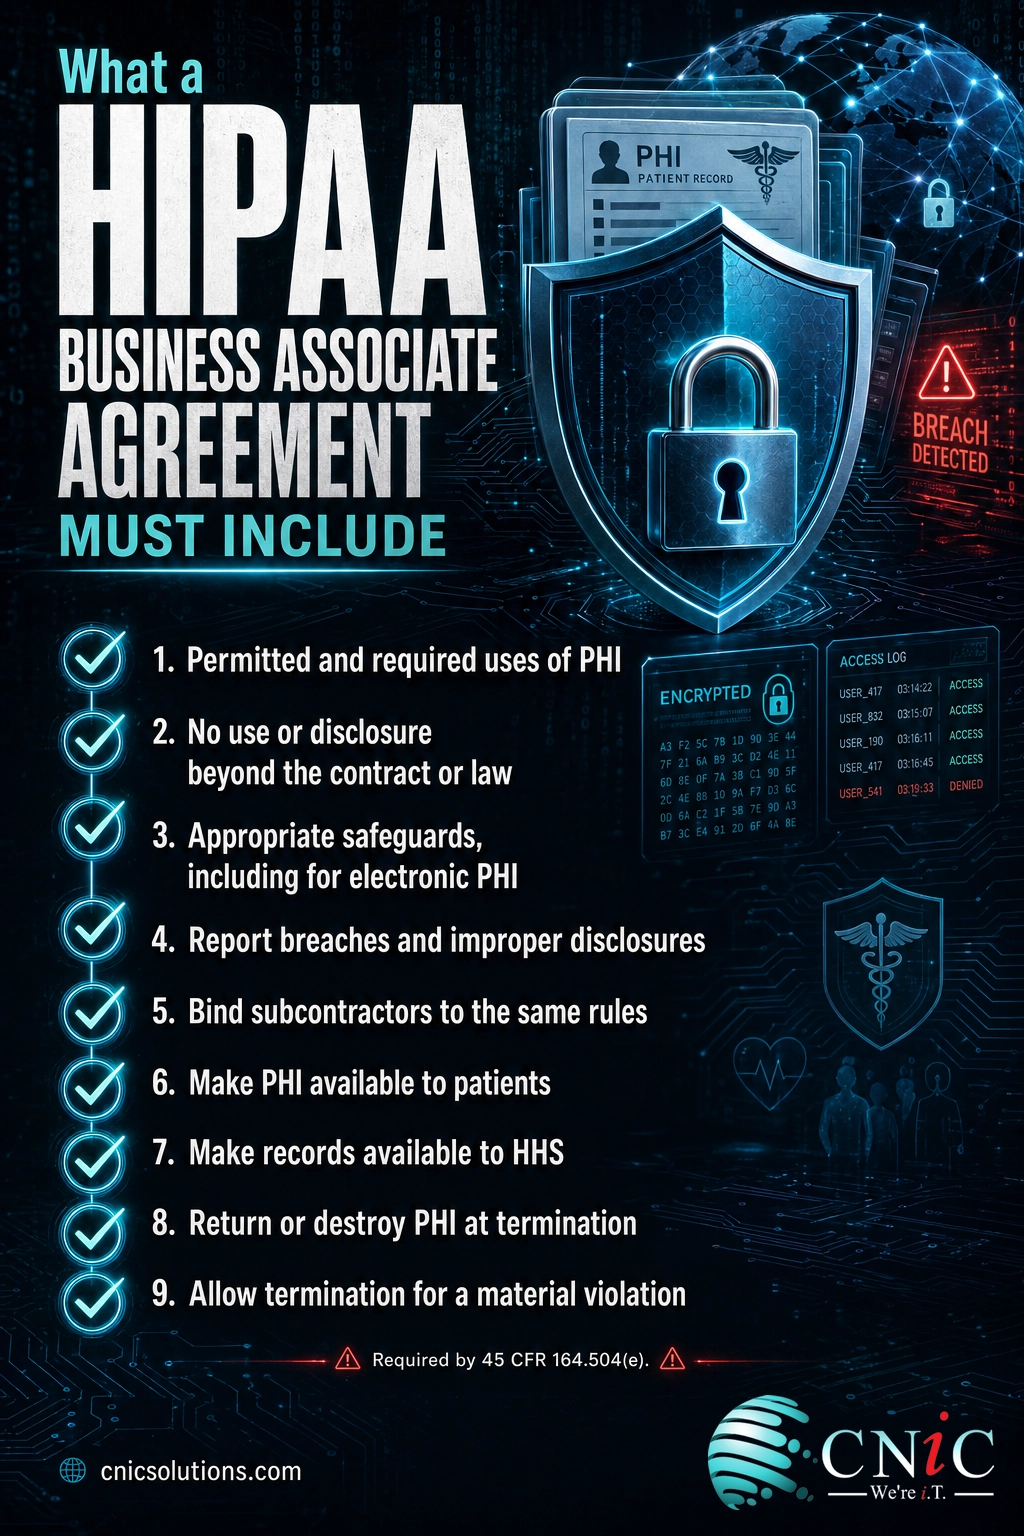
A BAA is not freeform. HHS specifies the provisions a compliant agreement must contain. A contract that leaves these out is not a valid BAA, even if both parties signed it in good faith. At minimum, a business associate agreement must:
- Describe the permitted and required uses of PHI by the business associate.
- Prohibit further use or disclosure of PHI beyond what the contract or the law allows.
- Require appropriate safeguards to prevent unauthorized use or disclosure, including Security Rule protections for electronic PHI.
- Mandate reporting of any use or disclosure not permitted by the contract, including breaches of unsecured PHI.
- Bind subcontractors to the same restrictions and conditions through their own agreements (the flow-down requirement).
- Make PHI available to satisfy patients’ rights of access, amendment, and an accounting of disclosures.
- Make internal practices and records available to HHS for a compliance investigation.
- Return or destroy all PHI at termination of the contract, where feasible.
- Authorize termination by the covered entity if the business associate violates a material term.
HHS publishes sample business associate agreement provisions that healthcare organizations can adapt, but the sample is a starting point, not a substitute for legal review. The clauses have to match the real relationship, the specific services, and the way PHI actually moves between the parties.
Myth: signing a vendor’s standard terms of service counts as a BAA. It does not. A generic terms-of-service click-through or a standard master services agreement almost never contains the clauses required by 45 CFR 164.504(e). Reputable healthcare-facing vendors offer a real, separate BAA and will execute it on request. If a vendor cannot produce one, it is not ready to handle PHI, and neither are you if you use it anyway.
Source: HHS, Sample Business Associate Agreement Provisions
Why a BAA Matters: Penalties and Liability
A BAA is not a formality you can circle back to later. Failing to have one, or having an inadequate one, is a HIPAA violation on its own terms, and federal regulators have repeatedly enforced it. Two realities make the stakes concrete.
First, the penalties are steep and tiered by culpability. The HHS Office for Civil Rights sets civil monetary penalties across four tiers, from an entity that had no knowledge of a violation up to willful neglect that was never corrected. As of the inflation adjustment effective January 28, 2026, the ranges are as follows.
| Tier | Culpability | Per-violation range |
|---|---|---|
| Tier 1 | No knowledge, could not have known with reasonable diligence | $145 to $73,011 |
| Tier 2 | Reasonable cause, not willful neglect | $1,461 to $73,011 |
| Tier 3 | Willful neglect, corrected within 30 days | $14,602 to $73,011 |
| Tier 4 | Willful neglect, not corrected | $73,011 to $2,190,294 |
Every tier shares the same annual ceiling for repeated violations of a single provision, which now stands at $2,190,294.
Second, regulators have fined organizations specifically for missing BAAs, sometimes with no data breach at all. In 2017, the Center for Children’s Digestive Health settled with OCR for $31,000 after it could not produce signed business associate agreements with a records storage vendor. No patient data was shown to be exposed. The violation was the absent paperwork itself.
That case was not an outlier. BAA failures have surfaced in a string of OCR settlements, often alongside larger security lapses, and the dollar figures climb quickly.
OCR Settlements Where a Missing or Inadequate BAA Was Cited
Federal settlements in which a missing or deficient business associate agreement was among the cited failures. Source: HHS Office for Civil Rights resolution agreements.
The lesson for any covered entity is simple. A BAA is one of the cheapest, fastest compliance steps available, and the absence of one is among the easiest violations for a regulator to prove. When an incident does occur, the first question investigators ask about any involved vendor is whether a valid agreement was in place.
Source: HHS Office for Civil Rights, Resolution Agreements | Federal Register, HHS civil monetary penalty adjustments
Who Needs a BAA and Who Doesn’t
The rule of thumb is direct: if a vendor will create, receive, maintain, or transmit PHI for a covered entity, a BAA is required. But two categories fall outside the requirement, and mixing them up causes trouble in both directions.
The conduit exception. Organizations that merely transport data without accessing it, in the way a postal service or an internet service provider does, are treated as conduits, not business associates. The exception is narrow. It covers transient transmission, not storage. A courier that carries sealed records is a conduit; a cloud vendor that stores those records is a business associate, even if it promises never to look at them. HHS has been explicit that persistent access to data, not actual viewing, is what matters.
Members of your own workforce. Employees and, in many cases, contracted staff who work under the covered entity’s direct control are part of the workforce, not business associates. They are governed by internal HIPAA policies and training rather than a BAA.
Everyone in between needs an agreement. When you are unsure, the safe and correct default is to ask: does this party need PHI, or access to systems holding PHI, to do the job? If yes, get the BAA signed first. This is exactly the kind of question a structured IT compliance program is built to answer before data ever changes hands.
How to Put BAAs in Place
Getting your BAAs in order is a manageable project, not a legal ordeal. The work breaks into a few clear steps.
- Inventory every vendor that touches PHI. List all outside parties, including cloud services, IT support, billing, email, backup, and document handling. This vendor map is the foundation, and it is usually longer than people expect.
- Confirm which are business associates. For each vendor, apply the create, receive, maintain, or transmit test. When in doubt, treat them as a business associate.
- Execute a compliant BAA with each one. Use an agreement built on the required clauses, reviewed by counsel, and matched to the actual service. Keep the signed copies where you can retrieve them for an audit.
- Extend the chain to subcontractors. Confirm that each business associate has its own agreements with the subcontractors it uses, so the obligations flow all the way down.
- Review on a schedule. Re-check BAAs when you add a vendor, change services, or at least annually, so the paperwork keeps pace with how data actually moves.
For most small and midsize healthcare organizations, this is where a capable managed IT partner earns its keep. A provider that already understands HIPAA can help build the vendor inventory, run the technical safeguards the BAA promises, and sign a compliant agreement for its own role in one motion. If your practice is weighing that step, our team can walk you through it as part of a broader IT and security program built for healthcare providers.
Get a Free Security and Compliance Assessment
See the Small Business Compliance Checklist
Common Questions About BAAs
What is a business associate agreement (BAA)?
Who needs a business associate agreement?
What must a HIPAA business associate agreement include?
What happens if you don’t have a BAA?
Is a BAA the same as a standard vendor contract or NDA?
Related Terms
- Protected health information (PHI): individually identifiable health information that HIPAA safeguards, the data a BAA is written to protect.
- Covered entity: a healthcare provider, health plan, or clearinghouse that collects PHI directly and must sign a BAA with each of its vendors.
- Business associate: an outside party that handles PHI for a covered entity and is directly liable under HIPAA.
- HIPAA Security Rule: the standards for protecting electronic PHI that a BAA obligates a business associate to follow.
- Omnibus Rule (2013): the update that made business associates and their subcontractors directly liable to regulators.
- IT compliance: the broader discipline of meeting the legal and regulatory requirements that apply to your technology, of which HIPAA is one framework among many.
- Data governance: the policies that control how data is handled across an organization. See what data governance means for a business.
- CMMC compliance: the defense-sector equivalent of contractual data protection requirements. Learn what CMMC compliance requires.
About This Guide
Definitions of business associates, covered entities, and required agreement provisions are drawn from the U.S. Department of Health and Human Services Office for Civil Rights and the HIPAA regulations at 45 CFR 164.504(e). Civil monetary penalty amounts reflect the inflation-adjusted figures effective January 28, 2026, as published by HHS in the Federal Register. Enforcement examples are taken from HHS OCR resolution agreements and are cited to illustrate how BAA failures have been penalized, not as predictions for any specific organization. Nothing here is legal advice; consult qualified counsel for your own agreements.
Sources: HHS OCR, Business Associates | HHS, Sample BAA Provisions | HHS OCR, Resolution Agreements | Federal Register, HHS penalty adjustments
Talk to CNiC About HIPAA-Ready IT and Security


related posts
OKRs vs. KPIs: What’s the Difference?
September 22, 2026An OKR (Objective and Key Results) is a goal-setting framework that pairs an ambitious objective with…
Password Statistics for 2026: Reuse, Cracks, and the Passkey Shift
September 22, 2026Weak and stolen passwords are still the number one way attackers get in. In 2025, stolen…
15 Microsoft Teams Tips and Tricks to Boost Team Productivity
September 21, 2026Microsoft Teams is where most of the workday now happens: it passed 320 million monthly active…
Mobile Security Software for Business: A Buyer’s Guide
September 21, 2026Choosing mobile security software for business comes down to two decisions: how you will manage the…