The best cybersecurity certifications in 2026 are the ones that match a real career stage and a real job, not the ones with the most impressive acronym. For someone starting out, that means ISC2’s Certified in Cybersecurity or CompTIA Security+. For a senior leader, it means CISSP or CISM. And if you are a business owner rather than a candidate, these same credentials are the clearest signal of whether the people protecting your network actually know what they are doing. This guide explains the nine certifications that matter most, what each one costs, who it is for, and how to read them when you are hiring or choosing a provider.
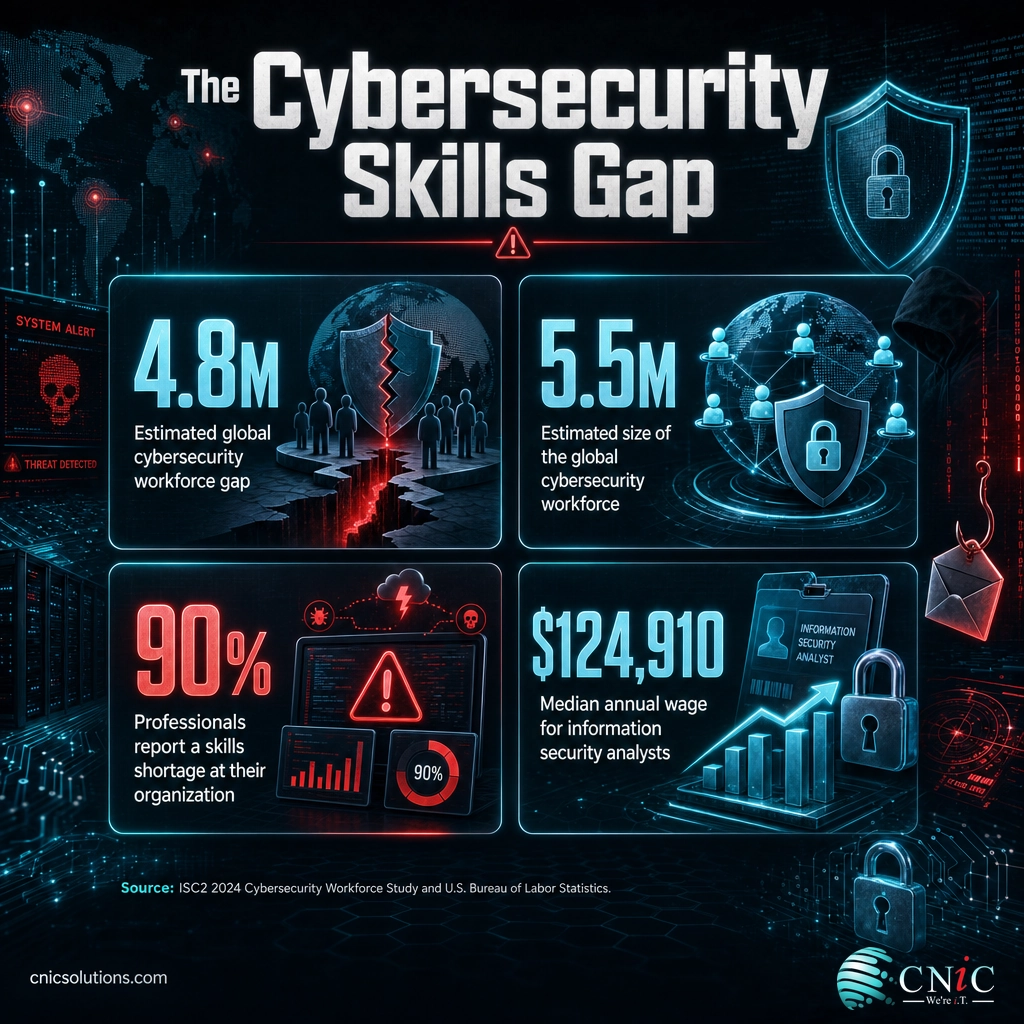
- The talent gap is the backdrop. ISC2’s 2024 Workforce Study put the global shortage at 4.8 million professionals, a 19% jump in a single year, which is why certified skills command a premium.
- Start where you stand. ISC2’s Certified in Cybersecurity (CC) needs no experience and costs 199 dollars; Security+ is the baseline for anyone already in IT.
- The senior credentials gate the senior pay. CISSP and CISM both require five years of experience, and the roles they unlock sit well above the 124,910 dollar median wage the BLS reports for information security analysts.
- Vendor-neutral beats vendor-specific for proving general skill. Security+, CySA+, CISSP, and OSCP test capability, not a single product line.
- For business owners, certifications are a vetting tool. Ask which credentials the people on your account hold; “we are certified” with no specifics is a warning sign.
What’s in This Guide
The 9 best cybersecurity certifications:
- 1. ISC2 Certified in Cybersecurity (CC)
- 2. CompTIA Security+
- 3. CompTIA CySA+
- 4. Certified Ethical Hacker (CEH)
- 5. OffSec OSCP
- 6. CISSP
- 7. CISM
- 8. CISA
- 9. CCSP
Put it to use:
Why Cybersecurity Certifications Matter in 2026
A certification is a shortcut for trust. It tells an employer, a client, or an auditor that a person has proven a defined body of knowledge against an independent standard, rather than just claiming to know it. In a field where a single misconfiguration can cost a business everything, that verification carries real weight, and the market pays for it.
The demand is not subtle. ISC2’s 2024 Cybersecurity Workforce Study estimated the global workforce at 5.5 million people while the gap between the talent organizations need and the talent available reached 4.8 million, a 19% increase year over year. Ninety percent of the professionals surveyed said their organization faces a skills shortage. When qualified people are that scarce, a credential that proves capability becomes one of the fastest ways to stand out or, if you are hiring, to filter.
Pay follows the scarcity. The U.S. Bureau of Labor Statistics reported a median annual wage of 124,910 dollars for information security analysts in May 2024, with the top 10 percent earning more than 186,420 dollars. The BLS also projects the role to grow 29 percent between 2024 and 2034, far faster than the average occupation, with roughly 16,000 openings each year. Certifications are how professionals signal they belong in the higher band of that range, and how employers decide whom to interview.
There is a second audience for this information. If you run a business and rely on an internal IT person or an outside provider, the certifications those people hold are one of the few objective ways to judge their depth. A team that keeps its credentials current is a team that is still learning in a field that changes every quarter. We come back to that lens in the section for business owners below.
Source: ISC2 2024 Cybersecurity Workforce Study | U.S. Bureau of Labor Statistics, Information Security Analysts
How We Grouped These Certifications
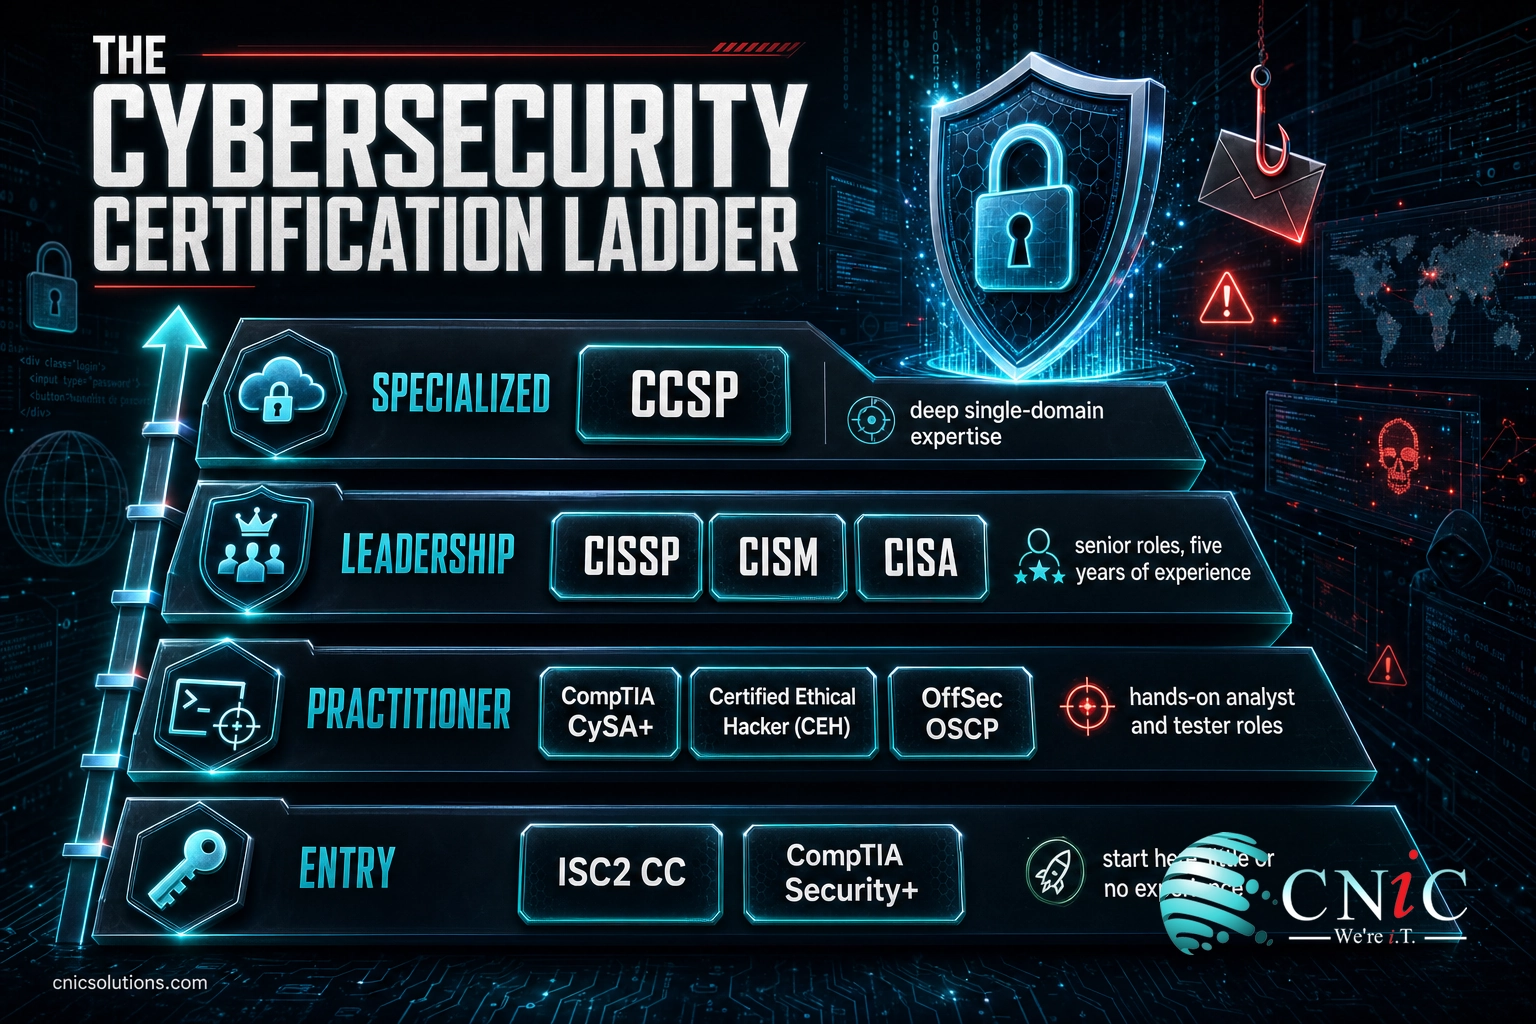
Cybersecurity certifications are not a single ladder you climb in order. They branch by role and by depth. The right one for a help-desk technician moving into security is the wrong one for an experienced engineer aiming at a leadership seat. To make the list usable, we sorted the nine credentials into four bands based on where they fit in a career.
- Entry level (start here): credentials that assume little or no prior security experience and prove you understand the fundamentals. ISC2 CC and CompTIA Security+.
- Practitioner and technical: hands-on credentials for analysts, defenders, and offensive testers who do the work day to day. CompTIA CySA+, Certified Ethical Hacker, and OffSec OSCP.
- Leadership and management: senior credentials that gate roles running security programs, requiring years of experience. CISSP, CISM, and CISA.
- Specialized: deep credentials in a specific domain, earned once the fundamentals are in place. CCSP for cloud security.
Two distinctions cut across all four bands. The first is vendor-neutral versus vendor-specific. The certifications in this guide are all vendor-neutral: they prove general capability rather than fluency in one company’s product. Vendor certifications (Microsoft, Cisco, AWS, Fortinet) are valuable on top of these, but they answer a narrower question. The second is knowledge versus hands-on. Most exams test what you know through multiple-choice questions; a few, notably OSCP, make you actually break into systems in a timed lab. Both have their place, and the strongest resumes usually pair one of each.
1 ISC2 Certified in Cybersecurity (CC)
Level: Entry. Best for: Career changers and newcomers with no security experience who want a recognized first credential.
Certified in Cybersecurity is ISC2’s answer to a real problem: every senior credential wants experience, but you cannot get experience without a first job, and the first job wants proof you know the basics. CC breaks that loop. It has no work-experience prerequisite, the exam runs about 199 dollars, and ISC2 offers free official self-paced training to prepare for it. The exam is 100 to 125 adaptive questions over two hours, covering security principles, access control, network security, and basic operations.
Why it matters: It gives a newcomer a name-brand credential from the same body that issues the CISSP, which carries more weight with hiring managers than a generic online course certificate. For a business, a junior hire or help-desk technician holding CC shows they take the field seriously.
How to earn it: Register with ISC2, use the free official training or a low-cost study guide, and pass the exam. After passing you pay a 50 dollar annual maintenance fee and earn continuing education credits to keep it active. If you are brand new to security, this is the single best place to spend your first study hours.
Source: ISC2 Certified in Cybersecurity official page
2 CompTIA Security+
Level: Entry. Best for: Anyone already in IT who wants the credential employers and government contracts recognize as the security baseline.
If there is one certification the whole industry agrees on as a starting point, it is Security+. It is vendor-neutral, it maps to the U.S. Department of Defense baseline requirements for certain roles, and it appears in more entry-level job postings than any other security credential. The current SY0-701 exam covers threats and attacks, architecture, operations, and governance, and the direct exam fee from CompTIA is 439 dollars as of mid-2026.
Why it matters: Security+ is the credential that gets a resume past the first filter for a security analyst or administrator role. Unlike CC, it assumes some working familiarity with IT, so it proves you can apply concepts, not just recall them. For regulated employers and contractors, it often satisfies a compliance checkbox on its own.
How to earn it: CompTIA recommends Network+ and about two years of IT experience first, though neither is mandatory. Study the SY0-701 objectives, buy a voucher (authorized resellers often price below CompTIA’s list), and pass one exam. Renewal runs on a three-year cycle through 50 continuing education units.
CC or Security+, not both. These two overlap heavily. If you have zero IT background, start with CC to build confidence, then move to Security+ once you have some footing. If you already work in IT, skip straight to Security+; it is the one hiring managers explicitly look for, and paying for both adds little.
Source: CompTIA Security+ official page
3 CompTIA CySA+
Level: Practitioner. Best for: Analysts moving into a security operations or blue-team role focused on detection and response.
CySA+ (Cybersecurity Analyst) sits one tier above Security+ in CompTIA’s lineup and shifts the focus from broad fundamentals to the daily work of a defender: reading logs, hunting threats, analyzing data from security tools, and responding to incidents. Where Security+ proves you understand security, CySA+ proves you can operate a security program’s detection layer. It is a natural second certification for someone who has landed an analyst seat and wants to formalize the skills.
Why it matters: Detection and response is where most real defensive work happens, and CySA+ is one of the few vendor-neutral credentials aimed squarely at it. It signals that a candidate can work inside a security operations center rather than just describe one. That maps directly to the kind of monitoring a business needs, whether staffed in-house or delivered through a managed security services provider (MSSP).
How to earn it: CompTIA recommends Security+ and a few years of hands-on experience first. It is a single exam (CS0-003) that includes performance-based questions, so lab practice matters more than for Security+. Renewal follows the same three-year continuing-education model.
Source: CompTIA CySA+ official page
4 Certified Ethical Hacker (CEH)
Level: Practitioner. Best for: Professionals moving toward offensive security who value broad name recognition, especially with government and corporate HR.
EC-Council’s Certified Ethical Hacker is the best-known name in offensive security certifications, and that recognition is its main strength. The credential surveys the attacker’s toolkit, reconnaissance, scanning, exploitation, and the common vulnerability classes, so a holder can think like an adversary while working defensively. It is frequently listed by name in job postings and government role requirements, which is why it endures despite debate about its depth.
Why it matters: CEH opens doors specifically because so many HR filters and contracts ask for it by name. It is more knowledge-focused than hands-on, so it pairs well with a practical credential like OSCP for anyone serious about penetration testing.
How to earn it: There are two paths. Complete official EC-Council training (which waives the experience requirement), or self-study and prove at least two years of information security experience plus a 100 dollar application fee. The exam voucher is about 1,199 dollars at a Pearson VUE testing center. Budget for training if you take the self-study route, because the exam assumes structured preparation.
A certification is not the same as competence. This matters most with well-known credentials like CEH. A multiple-choice exam proves someone studied a body of knowledge; it does not prove they can defend your network under pressure. The strongest professionals treat certifications as a floor, then back them with hands-on labs, real incident experience, and continuing education. When you evaluate a person or a provider, ask what they have actually done, not only what they have passed. Paper credentials with no practical track record behind them are exactly how underqualified vendors pass a first-glance check.
Source: EC-Council Certified Ethical Hacker official page
5 OffSec OSCP
Level: Practitioner (advanced). Best for: Aspiring penetration testers who want a credential that proves hands-on skill, not just knowledge.
The Offensive Security Certified Professional is the credential that hiring managers in offensive security respect most, because you cannot pass it by memorizing. The exam is a grueling 24-hour practical: you are dropped into a lab of vulnerable machines and have to actually compromise them, then write a professional report on how you did it. It earns its reputation the hard way, and “try harder” is its unofficial motto for a reason.
Why it matters: OSCP is proof of capability rather than recall. A candidate who holds it has demonstrably broken into real systems under time pressure, which is why it often outweighs a stack of multiple-choice certifications for a penetration testing role. For a business commissioning a security assessment, an OSCP-holding tester is a strong signal the work will be real, not a checklist scan.
How to earn it: The standard path is OffSec’s PEN-200 course-and-certification bundle at 1,749 dollars, which includes 90 days of lab access and one exam attempt. Expect months of dedicated practice; OSCP rewards volume of hands-on work more than reading. It is not a first certification, but it is a career-defining one for offensive specialists.
Source: OffSec PEN-200 and OSCP official page
What These Certifications Cost
Sticker price is only part of the picture. The exam fee is the headline number, but training, study materials, and annual maintenance fees add up, and the senior credentials cost far more in time than in money because of their experience requirements. Here is how the 2026 exam fees compare at a glance, from the hands-on OSCP bundle down to the entry-level CC.
2026 Exam Fee by Certification (USD, base exam or bundle)
Base exam or bundle fees as published by each certification body in 2026. ISACA figures shown are member rates; non-members pay 760 dollars plus a 50 dollar application fee. Verify current pricing before registering.
Two things stand out. First, the entry-level credentials are genuinely affordable, so cost is rarely the reason not to start. Second, the leadership credentials (CISSP, CISM, CISA) look mid-priced on the exam alone, but their true cost is the five years of qualifying experience they require. That experience is the barrier, not the fee, which is exactly what makes them credible.
Source: ISC2 certification fees | CompTIA Security+ | ISACA CISM
6 CISSP
Level: Leadership. Best for: Experienced professionals moving into senior security engineering, architecture, or management.
The Certified Information Systems Security Professional is the flagship of the industry. Issued by ISC2, it covers eight domains spanning the full breadth of security, from asset management and architecture to operations and software security. It is the credential most often named in senior job descriptions and the one that most reliably separates a mid-level practitioner from a candidate ready to own a security program. Its authority comes from its experience bar as much as its exam.
Why it matters: CISSP is a management-track credential as much as a technical one. It proves both breadth of knowledge and the years of real work behind it, which is why it commands respect and salary. For a business, a provider with CISSP-holding staff has demonstrably senior security leadership on the bench.
How to earn it: You need five years of cumulative paid work experience across at least two of the eight domains (four years with a qualifying degree or approved credential). The exam fee is 749 dollars. Maintaining it requires 125 continuing professional education credits over three years and a 125 dollar annual maintenance fee. If you pass the exam without the experience, you become an Associate of ISC2 while you accrue it.
If your business would rather borrow senior security leadership than build it, that is what a Virtual CIO and security leadership program is designed to provide.
Source: ISC2 CISSP official page
7 CISM
Level: Leadership. Best for: Professionals moving from doing security to managing it, on a governance and program track.
ISACA’s Certified Information Security Manager is the leadership credential for people who run security rather than configure it. Where CISSP leans technical-plus-management, CISM is squarely about governance: building and managing an information security program, aligning it to business goals, managing risk, and handling incidents at a strategic level. It is a favorite for anyone aiming at a security manager or CISO seat.
Why it matters: CISM proves you can translate security into business terms and run a program, not just execute controls. That is exactly the skill a growing company needs at the top of its security function, and it is why the credential is tied to some of the highest salaries in the field.
How to earn it: You need five years of information security work experience, including at least three in security management, though ISACA allows waivers of up to two years for holding certain credentials or degrees. The exam is 575 dollars for ISACA members and 760 for non-members, plus a 50 dollar application fee. A CISM Associate path exists if you pass before completing the experience.
CISSP or CISM? They overlap at the top but aim differently. Choose CISSP if you want the broadest, most widely recognized credential and expect to stay close to the technical architecture. Choose CISM if your path is purely management and governance. Many senior leaders eventually hold both, but early on, pick the one that matches the job you actually want.
Source: ISACA CISM official page
8 CISA
Level: Leadership. Best for: Professionals in IT audit, controls, and compliance, especially in regulated industries.
ISACA’s Certified Information Systems Auditor is the standard for the audit and assurance side of security. It proves a holder can evaluate an organization’s IT systems and controls, identify gaps, and confirm that safeguards actually work as intended. For businesses in healthcare, finance, or any field with heavy compliance obligations, CISA is the credential that maps directly to the audit function regulators expect.
Why it matters: Security and compliance are related but distinct, and CISA covers the compliance and verification half that CISSP and CISM only touch. A provider or hire with CISA can speak the language of auditors, which is invaluable when your business faces a formal risk assessment or a compliance review.
How to earn it: CISA requires five years of experience in information systems auditing, control, or assurance, with some substitutions available. Like CISM, the exam is 575 dollars for members and 760 for non-members plus a 50 dollar application fee, and a CISA Associate designation exists for those who pass before earning the experience. Maintenance requires 120 continuing professional education hours over three years.
Source: ISACA CISA official page
9 CCSP
Level: Specialized. Best for: Experienced professionals responsible for securing cloud environments across AWS, Azure, or Google Cloud.
As businesses move workloads to the cloud, securing those environments has become its own discipline, and ISC2’s Certified Cloud Security Professional is the leading vendor-neutral credential for it. CCSP covers cloud architecture, data security, platform and infrastructure security, and legal and compliance considerations across providers, rather than the specifics of a single cloud vendor. It is a specialist credential earned once the fundamentals are solid.
Why it matters: Cloud misconfiguration is one of the most common causes of modern breaches, and CCSP proves someone understands how to prevent it in a vendor-neutral way. For a business running critical systems in the cloud, staff or a provider holding CCSP is direct evidence of cloud-specific security depth.
How to earn it: CCSP requires five years of IT experience, including three in security and at least one in a CCSP domain. Notably, holding CISSP waives the entire experience requirement, which is why the two are often earned in sequence. The exam is 599 dollars. ISC2 updated the CCSP exam outline effective August 1, 2026, so study from current materials.
Source: ISC2 CCSP official page
How to Prioritize (and Where to Start)
Nine credentials is a menu, not a to-do list. Almost no one should pursue all of them, and pursuing them in the wrong order wastes money and time. The right sequence depends entirely on where you are now and where you want to land. Use the table below to match a credential to a stage.
| Certification | Priority for | Difficulty | Impact |
|---|---|---|---|
| ISC2 CC | Complete newcomers | Low | Foundational |
| Security+ | Anyone entering security from IT | Low to moderate | High (baseline hiring signal) |
| CySA+ | New security analysts | Moderate | High for defensive roles |
| CEH | Offensive-curious, HR-filtered roles | Moderate | Medium (name recognition) |
| OSCP | Serious penetration testers | High | Very high for offensive roles |
| CISSP | Senior engineers and future leaders | High | Very high (career-defining) |
| CISM | Security managers and aspiring CISOs | High | Very high for management |
| CISA | Audit and compliance roles | High | High in regulated industries |
| CCSP | Cloud security specialists | High | High for cloud-heavy environments |
If you only make three moves from this list:
- Brand new? Earn ISC2 CC or Security+ and land any security-adjacent job. Experience is the real unlock.
- A few years in? Add the credential that matches your direction: CySA+ or OSCP if you want to stay hands-on, the path toward CISSP if you want to lead.
- Aiming at leadership? Set your sights on CISSP or CISM once you have the five years. That is the credential that changes the roles and the salary available to you.
The pattern across every stage is the same: certifications accelerate a career, but experience powers it. The best professionals treat each credential as a checkpoint that confirms real skill, not as a substitute for it.
Summary Comparison Table
Here is the full list in one view, with the 2026 exam fee, the experience each credential requires, and the career band it fits. Member rates are shown for ISACA credentials; confirm current pricing on each body’s official site before registering.
| Certification | Issuer | Level | Exam fee (2026) | Experience required |
|---|---|---|---|---|
| Certified in Cybersecurity (CC) | ISC2 | Entry | $199 | None |
| Security+ | CompTIA | Entry | $439 | None required (2 yrs recommended) |
| CySA+ | CompTIA | Practitioner | Mid-range CompTIA tier | None required (experience advised) |
| CEH | EC-Council | Practitioner | ~$1,199 voucher | 2 yrs, or official training |
| OSCP | OffSec | Practitioner (advanced) | $1,749 bundle | None required (hands-on exam) |
| CISSP | ISC2 | Leadership | $749 | 5 yrs (4 with degree) |
| CISM | ISACA | Leadership | $575 member | 5 yrs incl. 3 in management |
| CISA | ISACA | Leadership | $575 member | 5 yrs in audit / control |
| CCSP | ISC2 | Specialized | $599 | 5 yrs (waived for CISSP holders) |
For Business Owners: Reading a Provider’s Credentials
If you are not chasing a certification yourself but relying on people who should hold them, this list is a vetting tool. You do not need to memorize the acronyms, only to know what each one signals when it appears on a proposal or a LinkedIn profile.
A team with Security+ or CySA+ holders has current, tested fundamentals rather than sales training. A CISSP or CISM on staff means genuine senior security leadership is available to your account, the difference between a technician who follows a checklist and an architect who can design your defenses. CISA is the one to look for if your industry is regulated, because it proves real audit and compliance capability. And an OSCP-holding tester behind a security assessment means the work is hands-on, not an automated scan with a logo on it.
Two questions that separate real providers from resellers:
- “Which certifications do the people actually assigned to my account hold?” A company can advertise partnerships and badges while staffing your work with uncertified junior technicians. Ask about the individuals, not the logo wall.
- “How do you keep those certifications current?” Every credential here requires ongoing continuing education. A team that lets its certifications lapse is a team that has stopped learning in a field that never stops changing.
For most small and midsize businesses, the honest conclusion is that building a fully certified internal security team is neither realistic nor necessary. The alternative is to partner with a provider that already carries those credentials on staff. That is precisely the model behind CNiC’s managed cybersecurity services, and our broader managed IT program, where certified expertise is delivered as a service instead of a hire. If you are weighing that route, our guide to what a managed security services provider does and our roundup of top cybersecurity companies in 2026 are useful next reads.
Frequently Asked Questions
What is the best cybersecurity certification to start with?
Which cybersecurity certification pays the most?
How much do cybersecurity certifications cost?
Do cybersecurity certifications expire?
Should a small business owner care which certifications their IT provider holds?
Methodology and Sources
How this guide was built
The nine certifications were selected for recognition among employers, relevance across the main cybersecurity career tracks (defensive, offensive, leadership, audit, and cloud), and standing with the bodies that issue them. They were grouped by career band rather than ranked head to head, because the credentials serve different roles and are not direct substitutes. Exam fees, experience requirements, and maintenance terms were drawn from each certification body’s official documentation as of 2026; fees change, so verify current pricing on the official pages linked in each section before registering.
Workforce and salary figures come from primary research:
- ISC2 2024 Cybersecurity Workforce Study: the 4.8 million workforce gap, 5.5 million workforce estimate, and 90% skills-shortage figure.
- U.S. Bureau of Labor Statistics, Occupational Outlook Handbook: the 124,910 dollar median wage (May 2024) and 29% projected growth for information security analysts.
- Certification bodies: ISC2 (CC, CISSP, CCSP), CompTIA (Security+, CySA+), ISACA (CISM, CISA), EC-Council (CEH), and OffSec (OSCP).
CNiC Solutions is a Houston-based managed IT and cybersecurity provider. Where this guide notes what certifications signal when vetting a provider, it reflects CNiC’s own emphasis on maintaining certified staff, disclosed for transparency.


related posts
Types of Servers and How They Work: A Business Guide
September 29, 2026A server is a computer that provides a service, data, or resource to other computers, called…
Types of Phishing Attacks Every Business Should Know
September 29, 2026Phishing is a cyberattack in which criminals pose as a trusted person or organization to trick…
Types of Malware: A Guide to the Most Common Threats
September 28, 2026Malware (short for malicious software) is any program or code created to damage, disrupt, or gain…
Threat vs. Vulnerability vs. Risk: What’s the Difference in Cybersecurity?
September 28, 2026Quick definition: In cybersecurity, a vulnerability is a weakness that could be exploited, a threat is…